

I conducted penetration testing using and used it to extract user information from Active Directory (hereafter – AD). At that time, I focused on gathering information related to security group memberships, and then used this information to move laterally within the network. In any case, AD contains confidential information about employees, some of which really should not be accessible to everyone in the organization. In fact, there is an equivalent problem in Windows file systems, , which can also be exploited by both internal and external attackers.
But before we discuss privacy issues and how to address them, let’s take a look at the data stored in AD.
Active Directory is like a corporate Facebook
But in this case, you’re already friends with everyone! You may not learn about your colleagues’ favorite movies, books, and restaurants, but AD contains sensitive contact
information and other fields that can be exploited by hackers and even insiders with little technical skill.
System administrators are certainly familiar with the screenshot below. This is the Active Directory Users and Computers (ADUC) interface, where they set and edit user information and assign users to appropriate groups.
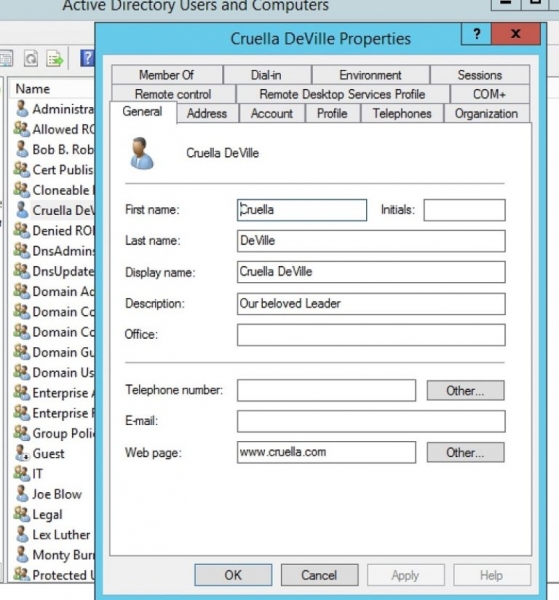
AD contains fields with employee names, addresses, and phone numbers, making it similar to a phone book. But there’s a lot more! Other tabs also include email addresses and web addresses, direct supervisors, and notes.
Should everyone in the organization be able to see this information, especially in the age of , where every new detail makes the search for additional information even easier?
Certainly not! The problem is compounded when the data of upper management is accessible to all employees.
PowerView for Everyone
This is where PowerView comes into play. It provides a very user-friendly PowerShell interface for the underlying (and tangled) Win32 functions that interact with AD. In short:
it makes retrieving AD fields as easy as typing a very short cmdlet.
Let's take the example of gathering information about employee Cruella Deville, who is one of the executives of the company. For this, we will use the PowerView cmdlet get-NetUser:
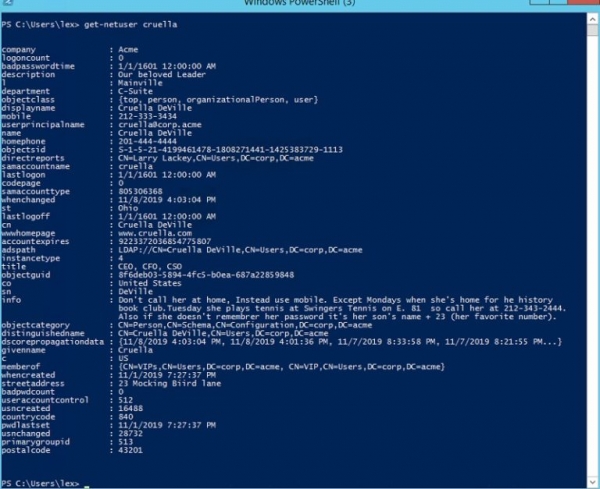
Installing PowerView is not a serious issue – see for yourself on the page . More importantly, you do not need elevated privileges to execute many PowerView commands, such as get-NetUser. Thus, a motivated but not very technically savvy employee can start poking around in AD without much effort.
From the screenshot above, it’s clear that an insider can quickly learn a lot about Cruella. Did you also notice that in the 'info' field, personal habits and the user's password are revealed?
This is not a theoretical possibility. From I found out that they scan AD for passwords in unencrypted form, and often these attempts, unfortunately, succeed. They know that companies are careless with information in AD, and generally do not know about the next subject – permissions in AD.
Active Directory has its own ACLs
The AD Users and Computers interface allows setting permissions for AD objects. AD has ACLs, and administrators can grant or deny access through them. You need to click 'Advanced' in the ADUC View menu, and then when you open a user, you will see the 'Security' tab where you set the ACL.
In my scenario with Cruella, I did not want all authenticated users to see her personal information, so I denied them read access:
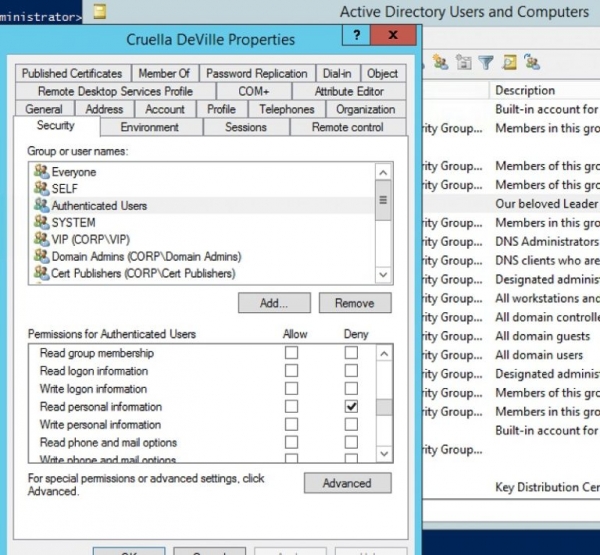
And now a normal user will see this if they try Get-NetUser in PowerView:
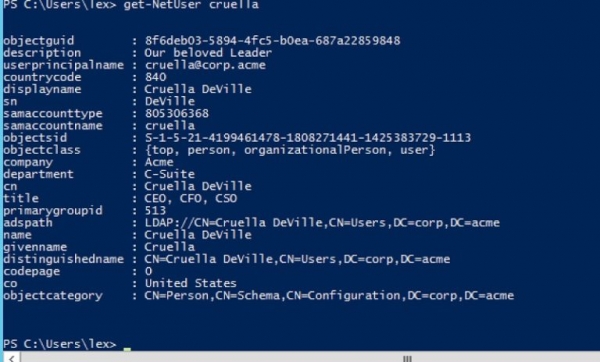
I managed to hide potentially useful information from prying eyes. To maintain access for relevant users, I created another ACL to allow members of the VIP group (Cruella and her other high-ranking colleagues) to access this confidential data. In other words, I implemented AD permissions based on a role model, which made sensitive data unavailable to most employees, including insiders.
However, you can make group membership invisible to users by appropriately setting the ACL for the group object in AD. This helps in terms of privacy and security.
In my I demonstrated how to navigate the system by exploring group membership using PowerViews Get-NetGroupMember. In my scenario, I restricted read access to the membership of a specific group. You can see the command output results before and after the changes:
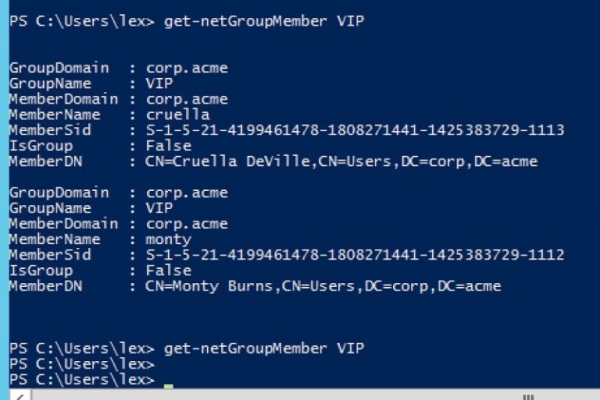
I was able to hide the membership of Cruella and Monty Burns in the VIP group, making it more difficult for hackers and insiders to probe the infrastructure.
This post was intended to motivate you to take a closer look at the fields
AD and the associated permissions. AD is a great resource, but think about how you
would like to share sensitive information and personal data, especially,
when it comes to the executives in your organization.
Source: habr.com
