

The WorldSkills movement is aimed at equipping participants primarily with practical skills in demand in the modern labor market. The 'Network and Systems Administration' competency consists of three modules: Network, Windows, Linux. The tasks change from championship to championship, as do the conditions of the competition; however, the structure of the tasks mostly remains unchanged.
The Network island will be first due to its simplicity compared to the Linux and Windows islands.
The following tasks will be discussed in the article:
- Assign names to ALL devices according to the topology
- Assign the domain name wsrvuz19.ru to ALL devices
- Create a user wsrvuz19 on ALL devices with the password cisco
- The user's password must be stored in the configuration as the result of a hash function.
- The user must have the highest privilege level.
- Implement the AAA model for ALL devices.
- Authentication on the remote console must be performed using the local database (except for devices RTR1 and RTR2)
- After successful authentication when accessing the remote console, the user should immediately enter the mode with the highest privilege level.
- Configure the need for authentication on the local console.
- Upon successful authentication on the local console, the user should enter the mode with the minimum privilege level.
- On BR1, upon successful authentication on the local console, the user should enter the mode with the highest privilege level.
- On ALL devices, set the password wsr for entering privileged mode.
- The password must NOT be stored in the configuration as the result of a hash function.
- Configure a mode where all passwords in the configuration are stored in encrypted form.
The network topology at the physical level is presented in the following diagram:
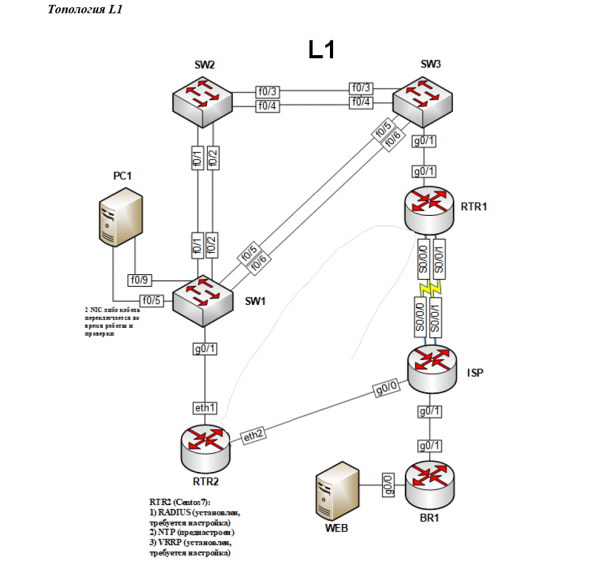
1. Assign names to ALL devices according to the topology
To set the device name (hostname), you need to enter the command from global configuration mode hostname SW1, where instead of SW1 the name of the equipment provided in the tasks must be written.
You can check the configuration visually — instead of the pre-installed Switch it became SW1:
Switch(config)# hostname SW1
SW1(config)#
The main task after making any configurations is to save the configuration.
This can be done from global configuration mode using the command do write:
SW1(config)# do write
Building configuration...
Compressed configuration from 2142 bytes to 1161 bytes[OK]
Or from privileged mode using the command exit:
SW1# write
Building configuration...
Compressed configuration from 2142 bytes to 1161 bytes[OK]
2. Assign the domain name wsrvuz19.ru to ALL devices
The default domain name wsrvuz19.ru can be set from global configuration mode using the command ip domain-name wsrvuz19.ru.
Verification is done with the command do show hosts summary from global configuration mode:
SW1(config)# ip domain-name wsrvuz19.ru
SW1(config)# do show hosts summary
Name lookup view: Global
Default domain is wsrvuz19.ru
...
3. Create the user wsrvuz19 with password cisco on ALL devices
It is necessary to create such a user who has the maximum level of privileges, and the password is stored as a hash function. All these conditions are taken into account with the command username wsrvuz19 privilege 15 secret cisco.
Here:
username wsrvuz19 — username;
privilege 15 — privilege level (0 — minimum level, 15 — maximum level);
secret cisco — storing the password as an MD5 hash.
The command show running-config allows you to check the current configuration settings, where you can find the line with the added user and make sure that the password is stored in encrypted form:
SW1(config)# username wsrvuz19 privilege 15 secret cisco
SW1(config)# do show running-config
...
username wsrvuz19 privilege 15 secret 5 $1$EFRK$RNvRqTPt5wbB9sCjlBaf4.
...
4. Implement the AAA model for ALL devices
The AAA model is a system of authentication, authorization, and accounting. To accomplish this task, the first step is to enable the AAA model and specify that authentication will be performed using the local database:
SW1(config)# aaa new-model
SW1(config)# aaa authentication login default local
a. Authentication on the remote console should be performed using the local database (except for devices RTR1 and RTR2)
The tasks define two types of consoles: local and remote. The remote console allows for remote connections, such as via SSH or Telnet protocols.
To accomplish this task, the following commands need to be entered:
SW1(config)# line vty 0 4
SW1(config-line)# login authentication default
SW1(config-line)# exit
SW1(config)#
The command line vty 0 4 transitions to the configuration of virtual terminal lines from 0 to 4.
The command login authentication default enables the default authentication mode on the virtual console, and the default mode was set in the previous task by the command aaa authentication login default local.
Exiting the remote console configuration mode is done using the command sigreturn.
A reliable check will be a test connection via Telnet from one device to another. It should be noted that basic switching and IP addressing must be configured on the selected equipment for this.
SW3#telnet 2001:100::10
User Access Verification
Username: wsrvuz19
Password:
SW1>
b. After successful authentication when logging in from the remote console, the user must immediately enter the maximum privilege level mode
To resolve such a task, it is necessary to return to the configuration of virtual terminal lines and set the privilege level with the command privilege level 15, where 15 is again the maximum level and 0 is the minimum privilege level:
SW1(config)# line vty 0 4
SW1(config-line)# privilege level 15
SW1(config-line)# exit
SW1(config)#
The verification will be the solution from the previous subsection — remote connection via Telnet:
SW3#telnet 2001:100::10
User Access Verification
Username: wsrvuz19
Password:
SW1#
After authentication, the user immediately enters privileged mode, bypassing unprivileged mode, which means the task has been completed correctly.
c-d. Configure the requirement on the local console, and upon successful authentication, the user should enter the minimum privilege level mode
The command structure in these tasks matches the previously solved tasks 4.a and 4.b. The command line vty 0 4 is replaced with console 0:
SW1(config)# line console 0
SW1(config-line)# login authentication default
SW1(config-line)# privilege level 0
SW1(config-line)# exit
SW1(config)#
As mentioned, the minimum privilege level is defined by the number 0. The check can be done as follows:
SW1# exit
User Access Verification
Username: wsrvuz19
Password:
SW1>
After authentication, the user enters unprivileged mode, as stated in the tasks.
e. On BR1, upon successful authentication on the local console, the user should enter the maximum privilege level mode
The local console configuration on BR1 will look as follows:
BR1(config)# line console 0
BR1(config-line)# login authentication default
BR1(config-line)# privilege level 15
BR1(config-line)# exit
BR1(config)#
The check is performed in the same way as in the previous item:
BR1# exit
User Access Verification
Username: wsrvuz19
Password:
BR1#
After authentication, a switch to privileged mode occurs.
5. Set the wsr password for entry into privileged mode on ALL devices.
The tasks state that the password for privileged mode should be stored in plaintext by default, but the password encryption mode will prevent viewing the password in plaintext. To set a password for entry into privileged mode, you need to use the command enable password wsr. By using the keyword password, the format in which the password will be stored is defined. If during user creation the password needs to be encrypted, the keyword used would be secret, and for storing in plaintext, the term used is password.
You can check the settings by viewing the current configuration:
SW1(config)# enable password wsr
SW1(config)# do show running-config
...
enable password wsr
!
username wsrvuz19 privilege 15 secret 5 $1$5I66$TB48YmLoCk9be4jSAH85O0
...
It is evident that the user's password is stored in an encrypted format, while the password for privileged mode is stored in plaintext, as stated in the tasks.
To ensure all passwords are stored in an encrypted format, you should use the command service password-encryption. The current configuration view will now look as follows:
SW1(config)# do show running-config
...
enable password 7 03134819
!
username wsrvuz19 privilege 15 secret 5 $1$5I66$TB48YmLoCk9be4jSAH85O0
...
The password is no longer accessible for viewing in plaintext.
Source: habr.com
