

Continuing the analysis of the module tasks of the Network competition at WorldSkills in the competence of 'Network and System Administration.'
The following tasks will be discussed in the article:
- Create virtual interfaces, sub-interfaces, and loopback interfaces on ALL devices. Assign an IP address according to the topology.
- Enable the SLAAC mechanism for issuing IPv6 addresses in the MNG network on the RTR1 router interface;
- On the virtual interfaces in VLAN 100 (MNG) on switches SW1, SW2, SW3, enable IPv6 auto-configuration mode;
- Manually assign link-local addresses on ALL devices (except PC1 and WEB);
- Disable ALL unused ports in the task on ALL switches and move them to VLAN 99;
- On switch SW1, enable a 1-minute lockout after two incorrect password entries within 30 seconds;
- All devices must be accessible for management via SSH protocol version 2.
The network topology at the physical level is presented in the following diagram:
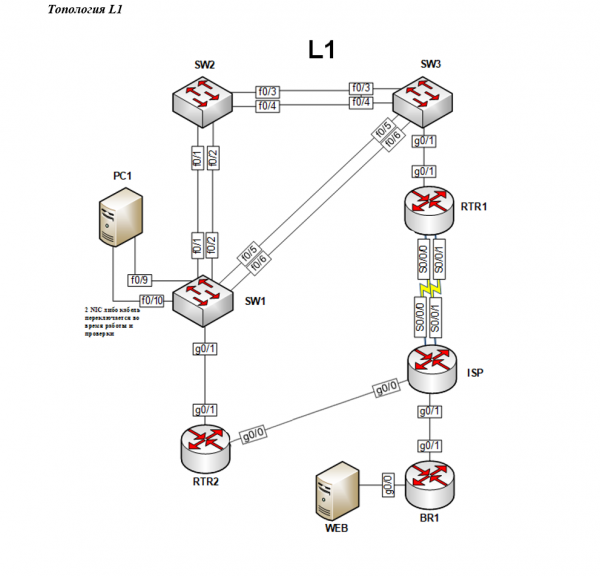
The network topology at the data link layer is presented in the following diagram:
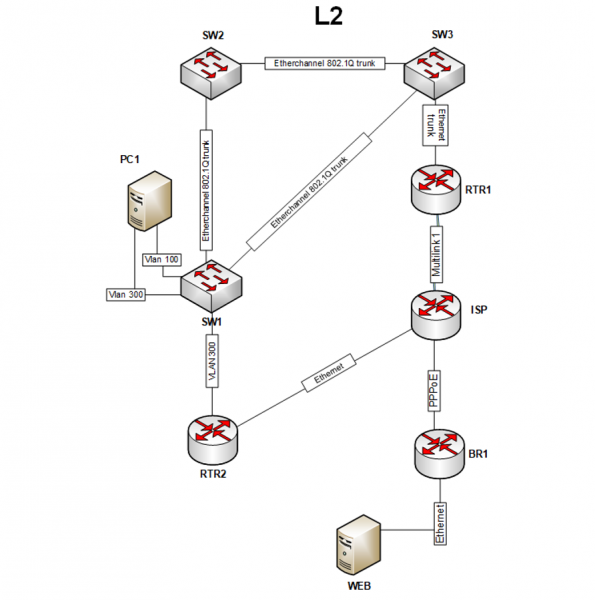
The network topology at the network layer is presented in the following diagram:
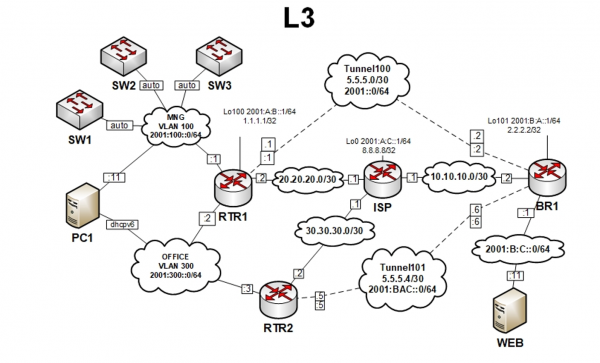
Pre-setup
Before performing the above tasks, it is advisable to set up basic switching on switches SW1-SW3, as it will be easier to verify their settings later. The configuration of switching will be described in detail in the following article, but for now, only settings will be defined.
First, you need to create VLANs numbered 99, 100, and 300 on all switches:
SW1(config)#vlan 99
SW1(config-vlan)#exit
SW1(config)#vlan 100
SW1(config-vlan)#exit
SW1(config)#vlan 300
SW1(config-vlan)#exit
The next step will be to move interface g0/1 on SW1 to VLAN number 300:
SW1(config)#interface gigabitEthernet 0/1
SW1(config-if)#switchport mode access
SW1(config-if)#switchport access vlan 300
SW1(config-if)#exit
Interfaces f0/1-2, f0/5-6, which point to other switches, should be switched to trunk mode:
SW1(config)#interface range fastEthernet 0/1-2, fastEthernet 0/5-6
SW1(config-if-range)#switchport trunk encapsulation dot1q
SW1(config-if-range)#switchport mode trunk
SW1(config-if-range)#exit
On switch SW2, the interfaces f0/1-4 will be in trunk mode:
SW2(config)#interface range fastEthernet 0/1-4
SW2(config-if-range)#switchport trunk encapsulation dot1q
SW2(config-if-range)#switchport mode trunk
SW2(config-if-range)#exit
On switch SW3, the interfaces f0/3-6, g0/1 will be in trunk mode:
SW3(config)#interface range fastEthernet 0/3-6, gigabitEthernet 0/1
SW3(config-if-range)#switchport trunk encapsulation dot1q
SW3(config-if-range)#switchport mode trunk
SW3(config-if-range)#exit
At this stage, the configuration of the switches will allow tagged packets to be exchanged, which will be necessary for completing the tasks.
1. Create virtual interfaces, sub-interfaces, and loopback interfaces on ALL devices. Assign IP addresses according to the topology.
First, configure the router BR1. According to the L3 topology, a loopback interface, also known as loopback, needs to be configured with the number 101:
// Создание loopback
BR1(config)#interface loopback 101
// Назначение ipv4-адреса
BR1(config-if)#ip address 2.2.2.2 255.255.255.255
// Включение ipv6 на интерфейсе
BR1(config-if)#ipv6 enable
// Назначение ipv6-адреса
BR1(config-if)#ipv6 address 2001:B:A::1/64
// Выход из режима конфигурирования интерфейса
BR1(config-if)#exit
BR1(config)#
To check the state of the created interface, you can use the command show ipv6 interface brief:
BR1#show ipv6 interface brief
...
Loopback101                [up/up]
    FE80::2D0:97FF:FE94:5022	//link-local address
    2001:B:A::1			//IPv6 address
...
BR1#
It is evident here that the loopback is active, its state UP. If you look further down, you can see two IPv6 addresses, although only one command was used to set the IPv6 address. The thing is that FE80::2D0:97FF:FE94:5022 — is a link-local address assigned when IPv6 is enabled on the interface with the command ipv6 enable.
And to view the IPv4 address, a similar command is used:
BR1#show ip interface brief
...
Loopback101        2.2.2.2      YES manual up        up
...
BR1#
For BR1, the g0/0 interface should be configured immediately, where it is necessary to simply assign an IPv6 address:
// Переход в режим конфигурирования интерфейса
BR1(config)#interface gigabitEthernet 0/0
// Включение интерфейса
BR1(config-if)#no shutdown
BR1(config-if)#ipv6 enable
BR1(config-if)#ipv6 address 2001:B:C::1/64
BR1(config-if)#exit
BR1(config)#
You can check the settings using the same command show ipv6 interface brief:
BR1#show ipv6 interface brief
GigabitEthernet0/0         [up/up]
    FE80::290:CFF:FE9D:4624	//link-local address
    2001:B:C::1			//IPv6 address
...
Loopback101                [up/up]
    FE80::2D0:97FF:FE94:5022	//link-local address
    2001:B:A::1			//IPv6 address
Next, the ISP router will be configured. Here, according to the task, a loopback with number 0 will be configured, but additionally, it is preferable to set up the g0/0 interface, which should have the address 30.30.30.1, because nothing will be mentioned about configuring these interfaces in subsequent tasks. First, configure the loopback with number 0:
ISP(config)#interface loopback 0
ISP(config-if)#ip address 8.8.8.8 255.255.255.255
ISP(config-if)#ipv6 enable
ISP(config-if)#ipv6 address 2001:A:C::1/64
ISP(config-if)#exit
ISP(config)#
The command show ipv6 interface brief you can ensure the correctness of the interface setup. Then configure the g0/0 interface:
BR1(config)#interface gigabitEthernet 0/0
BR1(config-if)#no shutdown
BR1(config-if)#ip address 30.30.30.1 255.255.255.252
BR1(config-if)#exit
BR1(config)#
Next, the router RTR1 will be configured. Here, a loopback under the number 100 also needs to be created:
BR1(config)#interface loopback 100
BR1(config-if)#ip address 1.1.1.1 255.255.255.255
BR1(config-if)#ipv6 enable
BR1(config-if)#ipv6 address 2001:A:B::1/64
BR1(config-if)#exit
BR1(config)#
Additionally, on RTR1, two virtual sub-interfaces for VLANs numbered 100 and 300 need to be created. This can be done as follows.
First, the physical interface g0/1 should be enabled with the command no shutdown:
RTR1(config)#interface gigabitEthernet 0/1
RTR1(config-if)#no shutdown
RTR1(config-if)#exit
Next, sub-interfaces with numbers 100 and 300 are created and configured:
// Создание подынтерфейса с номером 100 и переход к его настройке
RTR1(config)#interface gigabitEthernet 0/1.100
// Установка инкапсуляции типа dot1q с номером vlan'a 100
RTR1(config-subif)#encapsulation dot1Q 100
RTR1(config-subif)#ipv6 enable
RTR1(config-subif)#ipv6 address 2001:100::1/64
RTR1(config-subif)#exit
// Создание подынтерфейса с номером 300 и переход к его настройке
RTR1(config)#interface gigabitEthernet 0/1.300
// Установка инкапсуляции типа dot1q с номером vlan'a 100
RTR1(config-subif)#encapsulation dot1Q 300
RTR1(config-subif)#ipv6 enable
RTR1(config-subif)#ipv6 address 2001:300::2/64
RTR1(config-subif)#exit
The sub-interface number can differ from the VLAN number it will operate in, but for convenience, it's better to use a sub-interface number that matches the VLAN number. If encapsulation type is set when configuring the sub-interface, the number should match the VLAN number. Thus, following the command encapsulation dot1Q 300 the sub-interface will only pass packets from the VLAN with number 300.
The final part of this task involves the router RTR2. The connection between SW1 and RTR2 must be in access mode; the switch interface will only pass packets intended for the VLAN with number 300 to RTR2, as stated in the topology task for L2. Therefore, only the physical interface will be configured on router RTR2 without creating sub-interfaces:
RTR2(config)#interface gigabitEthernet 0/1
RTR2(config-if)#no shutdown
RTR2(config-if)#ipv6 enable
RTR2(config-if)#ipv6 address 2001:300::3/64
RTR2(config-if)#exit
RTR2(config)#
Then, the g0/0 interface is configured:
BR1(config)#interface gigabitEthernet 0/0
BR1(config-if)#no shutdown
BR1(config-if)#ip address 30.30.30.2 255.255.255.252
BR1(config-if)#exit
BR1(config)#
At this point, the configuration of router interfaces for the current task is complete. The configuration of other interfaces will be carried out as subsequent tasks are performed.
a. Enable the SLAAC mechanism for issuing IPv6 addresses in the MNG network on the router interface RTR1.
The SLAAC mechanism is enabled by default. The only thing that needs to be done is to enable IPv6 routing. This can be accomplished with the following command:
RTR1(config-subif)#ipv6 unicast-routing
Without this command, the equipment acts as a host. In other words, thanks to the aforementioned command, it becomes possible to use additional IPv6 features, including issuing IPv6 addresses, configuring routing, and more.
b. On the virtual interfaces in VLAN 100 (MNG) on the switches SW1, SW2, SW3, enable the IPv6 autoconfiguration mode.
The L3 topology shows that the switches are connected to the VLAN 100 network. This means that virtual interfaces need to be created on the switches, and then they should be assigned to receive default IPv6 addresses. The initial configuration was specifically set up so that the switches could obtain default addresses from RTR1. This task can be accomplished using the following list of commands suitable for all three switches:
// Создание виртуального интерфейса
SW1(config)#interface vlan 100
SW1(config-if)#ipv6 enable
// Получение ipv6 адреса автоматически
SW1(config-if)#ipv6 address autoconfig
SW1(config-if)#exit
You can check using the same command show ipv6 interface brief:
SW1#show ipv6 interface brief
...
Vlan100                [up/up]
    FE80::A8BB:CCFF:FE80:C000		// link-local address
    2001:100::A8BB:CCFF:FE80:C000	// received IPv6 address
In addition to the link-local address, an IPv6 address has been acquired from RTR1. This task has been successfully completed, and the same commands need to be written for the other switches.
c. On ALL devices (except for PC1 and WEB), manually assign link-local addresses
Thirty-digit IPv6 addresses do not bring joy to administrators, so there is an option to manually change the link-local address, shortening its length to a minimum. The tasks do not specify which addresses to choose, so there is freedom of choice here.
For example, on the SW1 switch, it is necessary to set the link-local address fe80::10. This can be done with the following command from the configuration mode of the selected interface:
// Вход в виртуальный интерфейс vlan 100
SW1(config)#interface vlan 100
// Ручная установка link-local адреса
SW1(config-if)#ipv6 address fe80::10 link-local
SW1(config-if)#exit
Now the addressing looks much more appealing:
SW1#show ipv6 interface brief
...
Vlan100                [up/up]
    FE80::10		//link-local address
    2001:100::10	//IPv6 address
In addition to the link-local address, the received IPv6 address has also changed, as the address is allocated based on the link-local address.
On the SW1 switch, it was necessary to set the link-local address on only one interface. More configuration needs to be done with the RTR1 router — it is necessary to set link-local on two sub-interfaces, on the loopback, and later configurations will include a tunnel interface 100.
To avoid excessive command writing, the same link-local address can be set on all interfaces at once. This can be done using the keyword range followed by listing all interfaces:
// Переход к настройке нескольких интерфейсов
RTR1(config)#interface range gigabitEthernet 0/1.100, gigabitEthernet 0/1.300, loopback 100
// Ручная установка link-local адреса
RTR1(config-if)#ipv6 address fe80::1 link-local
RTR1(config-if)#exit
When checking the interfaces, you will see that the link-local addresses on all selected interfaces have been modified:
RTR1#show ipv6 interface brief
gigabitEthernet 0/1.100		[up/up]
    FE80::1
    2001:100::1
gigabitEthernet 0/1.300		[up/up]
    FE80::1
    2001:300::2
Loopback100            		[up/up]
    FE80::1
    2001:A:B::1
All other devices are configured in a similar manner
d. Disable ALL unused ports on ALL switches as specified and assign them to VLAN 99
The main idea is the same as selecting multiple interfaces for configuration using the command range, followed by writing the commands to move to the desired VLAN and subsequently shutdown the interfaces. For instance, on the switch SW1, according to the L1 topology, ports f0/3-4, f0/7-8, f0/11-24 and g0/2 will be disabled. The configuration for this example will be as follows:
// Выбор всех неиспользуемых портов
SW1(config)#interface range fastEthernet 0/3-4, fastEthernet 0/7-8, fastEthernet 0/11-24, gigabitEthernet 0/2
// Установка режима access на интерфейсах
SW1(config-if-range)#switchport mode access
// Перевод в VLAN 99 интерфейсов
SW1(config-if-range)#switchport access vlan 99
// Выключение интерфейсов
SW1(config-if-range)#shutdown
SW1(config-if-range)#exit
When verifying the settings with the already known command, note that all unused ports should have a status of administratively down, indicating that the port is shut down:
SW1#show ip interface brief
Interface          IP-Address   OK? Method   Status                  Protocol
...
fastEthernet 0/3   unassigned   YES unset    administratively down   down
To see which VLAN a port belongs to, you can use another command:
SW1#show ip vlan
...
99   VLAN0099     active    Fa0/3, Fa0/4, Fa0/7, Fa0/8
                            Fa0/11, Fa0/12, Fa0/13, Fa0/14
                            Fa0/15, Fa0/16, Fa0/17, Fa0/18
                            Fa0/19, Fa0/20, Fa0/21, Fa0/22
                            Fa0/23, Fa0/24, Gig0/2
...
All unused interfaces should be listed here. It is important to note that you will not be able to assign interfaces to a VLAN if that VLAN has not been created. This is precisely why all necessary VLANs were created in the initial setup.
e. On switch SW1, enable the lockout for one minute after two incorrect password attempts within 30 seconds
This can be done with the following command:
// Блокировка на 60с; Попытки: 2; В течение: 30с
SW1#login block-for 60 attempts 2 within 30
You can also check these settings in the following way:
SW1#show login
...
   If more than 2 login failures occur in 30 seconds or less,
     logins will be disabled for 60 seconds.
...
Where it clearly explains that after two failed attempts within 30 seconds or less, login access will be blocked for 60 seconds.
2. All devices must be accessible for management via SSH protocol version 2
For devices to be accessible via SSH version 2, the equipment must be configured beforehand, so for the sake of information, the equipment will initially be configured with factory settings.
To change the protocol version, you can do so as follows:
// Установить версию SSH версии 2
Router(config)#ip ssh version 2
Please create RSA keys (of at least 768 bits size) to enable SSH v2.
Router(config)#
The system prompts to create RSA keys for the operation of SSH version 2. Following the recommendation from the smart system, RSA keys can be created using the following command:
// Создание RSA ключей
Router(config)#crypto key generate rsa
% Please define a hostname other than Router.
Router(config)#
The system does not allow the command to be executed because the hostname has not been changed. After changing the hostname, you need to enter the key generation command again:
Router(config)#hostname R1
R1(config)#crypto key generate rsa
% Please define a domain-name first.
R1(config)#
Now the system does not allow creating RSA keys due to the absence of a domain name. Only after setting the domain name will it be possible to create RSA keys. The length of RSA keys must be at least 768 bits for SSH version 2 to function:
R1(config)#ip domain-name wsrvuz19.ru
R1(config)#crypto key generate rsa
How many bits in the modulus [512]: 1024
% Generating 1024 bit RSA keys, keys will be non-exportable...[OK]
As a result, the following is necessary for SSHv2 to function:
- Change the hostname;
- Change the domain name;
- Generate RSA keys.
In the previous article, the configuration for changing the hostname and domain name on all devices was provided, so continuing the configuration of the current devices, it is only necessary to generate RSA keys:
RTR1(config)#crypto key generate rsa
How many bits in the modulus [512]: 1024
% Generating 1024 bit RSA keys, keys will be non-exportable...[OK]
SSH version 2 is active, but the devices are still not fully configured. The final step will be to configure virtual consoles:
// Переход к настройке виртуальных консолей
R1(config)#line vty 0 4
// Разрешение удаленного подключения только по протоколу SSH
RTR1(config-line)#transport input ssh
RTR1(config-line)#exit
In the previous article, an AAA model was configured, where authentication was set on virtual consoles using the local database, and the user should go directly to the privileged mode after authentication. The simplest check for SSH functionality is to attempt to connect to your own equipment. On RTR1, there is a loopback with the IP address 1.1.1.1; you can try connecting to this address:
//Подключение по ssh
RTR1(config)#do ssh -l wsrvuz19 1.1.1.1
Password:
RTR1#
After the key -l the login of an existing user is entered, followed by the password. After authentication, the transition to privileged mode occurs immediately, which means that SSH is configured correctly.
Source: habr.com
