

Hello everyone. In anticipation of the start of the course we have prepared a translation of an interesting article for you.
Today's guide will introduce you to the fundamentals to begin working with the package aircrack-ng. Of course, it’s impossible to provide all the necessary information and cover every scenario. So be prepared to do your homework and conduct research on your own. There are many additional tutorials and useful information on and in .
Although it does not cover all steps from start to finish, the guide elaborates on working with aircrack-ng.
Setting up hardware, installing Aircrack-ng
The first step in ensuring proper functionality aircrack-ng in your Linux system is to patch and install the appropriate driver for your wireless network card. Many cards work with multiple drivers, some of which provide the necessary functionality for using aircrack-ng, while others do not.
I think it’s unnecessary to mention that you need a network card compatible with the package aircrack-ng. This means hardware that is fully compatible and can inject packets. With a compatible network card, you can crack a wireless access point in less than an hour.
To determine which category your card falls into, review the page . Read , if you’re unsure how to navigate the table. Nevertheless, this will not hinder you while reading the guide, which will help you learn something new and confirm various properties of your card.
To start, you need to know which chipset is used in your network card and which driver you will need for it. You should determine this using the information from the paragraph above. In the section you will learn which drivers you require.
Installing aircrack-ng
You can obtain the latest version of aircrack-ng by , or you can use a distribution for penetration testing, such as Kali Linux or Pentoo, which includes the latest version. aircrack-ng.
To install aircrack-ng, refer to the .
Basics of IEEE 802.11
Well, now that everything is ready, it's time to take a break before we start acting and learn a little about how wireless networks work.
The next part is important to understand in order to troubleshoot if something doesn't work as expected. Understanding how this all works will help you find the problem or at least describe it accurately so that someone else can assist you. This part is a bit complex, and you might want to skip it. However, cracking wireless networks requires some knowledge, so it's a little more than just typing one command and letting aircrack do everything for you.
How to find a wireless network
This section is a brief introduction to managed networks that operate with access points (Access Point, AP). Each access point sends about 10 so-called beacon frames per second. These packets contain the following information:
- Network name (ESSID);
- Whether encryption is used (and what type of encryption is used, but note that this information may not be truthful simply because the access point reports it);
- What data transfer rates are supported (in MBit);
- What channel the network is on.
This information is displayed in the tool that connects specifically to this network. It shows up when you allow the card to scan networks using iwlist <interface> scan
Each access point has a unique MAC address (48 bits, 6 pairs of hexadecimal numbers). It looks something like this: 00:01:23:4A:BC:DE. Every network device has such an address, and network devices interact with each other using it. So it's somewhat like a unique name. MAC addresses are unique, and no two devices have the same MAC address.
Network connection
There are several ways to connect to a wireless network. In most cases, Open System Authentication is used. (Optional: if you want to know more about authentication, .)
Open System Authentication:
- Requests authentication from the access point;
- The access point responds: OK, you are authenticated.
- Requests association with the access point;
- The access point responds: OK, you are connected.
This is the simplest case, but problems arise when you do not have access rights because:
- WPA/WPA2 is used, and you need APOL authentication. The access point will respond with a refusal at the second step.
- The access point has a list of allowed clients (MAC addresses) and will not allow anyone else to connect. This is called MAC filtering.
- The access point uses Shared Key Authentication, which means you need to provide the correct WEP key to connect. (See the section to learn more about it)
Simple sniffing and hacking
Network discovery
The first thing to do is find a potential target. The aircrack-ng package has a tool for this, but you can also use other programs such as .
Before searching for networks, you need to switch your card to what is known as "monitor mode." Monitor mode is a special mode that allows your computer to listen to network packets. This mode also allows for injections. We will talk about injections next time.
To switch the network card to monitor mode, use :
airmon-ng start wlan0This will create another interface and add to it "mon."So, wlan0 the optional status of Paint and WordPad. These two programs are among the oldest, and it seems they will be installable or removable independently, just like any other applications. becomes wlan0mon.To check if the network card is truly in monitor mode, execute iwconfig and verify it for yourself.
Then, run to search for networks:
airodump-ng wlan0monIf airodump-ng if unable to connect to the WLAN device, you will see something like:
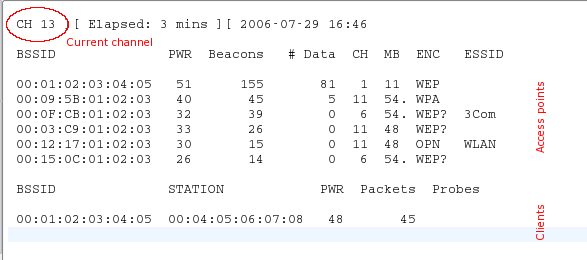
jumping from channel to channel and showing all access points from which it receives beacons. Channels 1 to 14 are used for 802.11 b and g standards (in the USA, only channels 1 to 11 are allowed; in Europe, channels 1 to 13 with some exceptions; in Japan, channels 1 to 14). 802.11a operates in the 5 GHz range, and its availability varies across countries more than in the 2.4 GHz range. In general, known channels start from 36 (32 in some countries) to 64 (68 in some countries) and from 96 to 165. You can find more detailed information about channel availability on Wikipedia. In Linux, the permission/restriction for transmission on certain channels for your country is managed by ; however, it must be configured appropriately.
The current channel is shown in the top left corner.
After a while, access points will appear and (hopefully) some associated clients.
The upper block shows the detected access points:
bssid
MAC address of the access point
pwr
signal quality when the channel is selected
pwr
signal strength. Some drivers do not report it.
beacons
the number of received beacons. If you do not have a signal strength indicator, you can measure it in beacons: the more beacons, the better the signal.
data
the number of received data frames
ch
the channel on which the access point operates
mb
the speed or mode of the access point. 11 is pure 802.11b, 54 is pure 802.11g. Values in between are a mixture.
enc
encryption: opn: no encryption, wep: WEP encryption, wpa: WPA or WPA2, wep?: WEP or WPA (unclear for now)
essid
network name, sometimes hidden
The lower block shows detected clients:
bssid
MAC address that the client is associated with at this access point
station
MAC address of the client itself
pwr
signal strength. Some drivers do not report it.
packets
the number of received data frames
probes
network names (essid) that this client has probed already
Now you need to monitor the target network. At least one client must be connected to it, as hacking networks without clients is a more complex subject (see section ). It should use WEP encryption and have a good signal. You might be able to adjust the antenna position to improve signal reception. Sometimes just a few centimeters can be crucial for signal strength.
In the example above, there is a network 00:01:02:03:04:05. It turned out to be the only possible target since only one client is connected to it. Plus, it has a good signal, which makes it a suitable target for practice.
Sniffing Initialization Vectors
Due to hopping between channels, you will not capture all packets from the target network. Therefore, we want to listen only on one channel and additionally save all data to disk so that we can later use it for hacking:
airodump-ng -c 11 --bssid 00:01:02:03:04:05 -w dump wlan0mon With the parameter -c you choose the channel, and the parameter after -w is the prefix for network dumps recorded to the disk. The flag –bssid together with the MAC address of the access point limits packet capture to a single access point. The flag –bssid is only available in newer versions. airodump-ng.
Before exploiting WEP, you will need between 40,000 to 85,000 different Initialization Vectors (IVs). Each data packet contains an initialization vector. They can be reused, so the number of vectors is usually slightly less than the number of intercepted packets.
Therefore, you will have to wait to intercept between 40k to 85k data packets (with IVs). If the network is not busy, this can take a very long time. You can speed up this process by using an active attack (or replay attack). We'll discuss these in the next section.
Hacking
If you already have enough intercepted initialization vectors stored in one or more files, you can try to crack the WEP key:
aircrack-ng -b 00:01:02:03:04:05 dump-01.cap The MAC address after the flag -b – is the target BSSID, and dump-01.cap – is the file containing the intercepted packets. You can use multiple files; just add all the names to the command or use a wildcard, for example dump*.cap.
You can get more information about the options , output, and usage from .
The number of initialization vectors needed to crack the key is not fixed. This is because some vectors are weaker and reveal more information about the key than others. Typically, these initialization vectors are mixed with stronger ones. So, if you're lucky, you might crack the key with just 20,000 initialization vectors. However, often this is not enough, aircrack-ng it can take a long time (a week or more in cases with high error rates) and then tell you that the key cannot be cracked. The more initialization vectors you have, the faster the crack can occur, and usually this happens in a few minutes or even seconds. Experience shows that 40,000 – 85,000 vectors are sufficient for cracking.
There are more advanced access points that use special algorithms to filter out weak initialization vectors. As a result, you will not be able to obtain more than N vectors from the access point, or you will need millions of vectors (for example, 5-7 million) to crack the key. You can , what to do in such situations.
Active attacks
Most devices do not support injections, at least without patched drivers. Some only support certain attacks. Refer to and check the column for aireplay. Sometimes this table does not provide accurate information, so if you see the word "NO" next to your driver, do not get discouraged; instead, check the driver's homepage, or the driver mailing list at . If you successfully performed a replay with a driver not listed as supported, feel free to suggest changes on the compatibility table page and add a link to a short guide. (To do this, you need to request a wiki account on IRC.)
First, you need to ensure that packet injection works with your network card and driver. The easiest way to test this is to perform a test injection attack. Before proceeding, make sure you have completed this test. Your card must be capable of injecting to proceed to the next steps.
You will need the BSSID (MAC address of the access point) and the ESSID (network name) of the access point that does not perform MAC address filtering (for example, your own) and is within range.
Try connecting to the access point with :
aireplay-ng --fakeauth 0 -e "your network ESSID" -a 00:01:02:03:04:05 wlan0mon The value after -a will be the BSSID of your access point.
Injection was successful if you see something like this:
12:14:06  Sending Authentication Request
12:14:06  Authentication successful
12:14:06  Sending Association Request
12:14:07  Association successful :-)
If not:
- Double-check the ESSID and BSSID;
- Ensure that MAC address filtering is disabled on your access point;
- Try this on another access point;
- Ensure that your driver is correctly configured and supported;
- Instead of "0", try "6000 -o 1 -q 10."
ARP replay
Now that we know packet injection works, we can do something that will significantly speed up capturing initialization vector attacks: ARP request injection .
The main idea
In simple terms, ARP works by sending a broadcast request to an IP address, and the device with that IP address sends back a response. Since WEP does not protect against replay attacks, you can sniff the packet and resend it over and over as long as it is valid. Thus, you only need to intercept and replay the ARP request sent to the access point to create traffic (and obtain initialization vectors).
Lazy method
First, open a window with airodump-ng, which sniffs traffic (see above). Aireplay-ng and airodump-ng can work simultaneously. Wait for a client to appear on the target network and begin the attack:
aireplay-ng --arpreplay -b 00:01:02:03:04:05 -h 00:04:05:06:07:08 wlan0mon-b indicates the target BSSID, -h to the MAC address of the connected client.
Now you need to wait for an ARP packet. Usually, it takes a few minutes (or read further in the article).
If you're lucky, you will see something like this:
Saving ARP requests in replay_arp-0627-121526.cap
You must also start airodump to capture replies.
Read 2493 packets (got 1 ARP requests), sent 1305 packets...
If you need to stop replaying, you don't have to wait for the next ARP packet; you can just use previously intercepted packets with the option -r <filename>
When using ARP injections, you can apply the PTW method to crack the WEP key. It significantly reduces the number of packets needed, and thus the time for cracking. You need to capture a full packet using airodump-ng, meaning do not use the option “--ivs” when executing the command. For aircrack-ng use “aircrack -z <file name>”
If the number of data packets received airodump-ng stops increasing, you may need to reduce the replay speed. Do this with the option -x <packets per second>
Aggressive method
Most operating systems clear the ARP cache when disconnected. If you need to send the next packet after reconnecting (or just using DHCP), they send an ARP request. As a side effect, you may sniff the ESSID and possibly the keystream during reconnection. This is useful if the ESSID of your target is hidden or it uses shared-key authentication.
Let’s airodump-ng and aireplay-ng get to work. Open another window and launch :
Here -a – this is the BSSID of the access point, -c the MAC address of the selected client.
Wait a few seconds and the ARP replay will work.
Most clients attempt to automatically reconnect. However, the risk of someone detecting this attack, or at least noticing what’s happening on the WLAN, is higher than with other types of attacks.
You can find more tools and information about them .
Source: habr.com
