

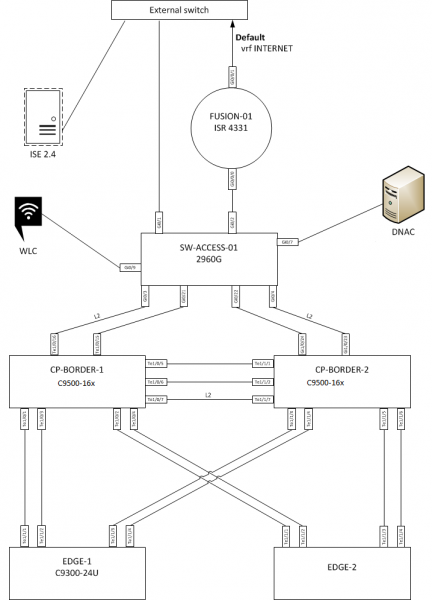
You can touch the stand in our lab if you want to.
SD-WAN and SD-Access are two different new proprietary approaches to building networks. In the future, they should merge into a single overlay network, but for now, they are only getting closer. The idea is this: take a network from the 1990s and apply all the necessary patches and features to it, without waiting for it to become a new open standard in another 10 years.
SD-WAN is a patch for SDN on distributed corporate networks. Transport is separate, control is separate, which simplifies control.
The advantages are that all communication channels are actively used, including the backup one. There is packet routing to applications: what goes through which channel and with what priority. The procedure for deploying new points is simplified: instead of applying a config, you only specify the address of the Cisco server in the public Internet, the KROK data center, or the customer, from where the configs specifically for your network are obtained.
SD-Access (DNA) is the automation of local network management: configuration from a single point, wizards, user-friendly interfaces. Essentially, a different network is built with different transport at the protocol level over your existing one, and compatibility with legacy networks is ensured at the perimeter boundaries.
We will also cover this further below.
Now let's see some demonstrations on test stands in our lab, showing how this looks and works.
Let's start with SD-WAN. Key features include:
- Simplification of deploying new points (ZTP) assumes that you somehow feed the point the address of the server with the settings. The point connects to it, receives the config, applies it, and integrates into your control panel. This ensures Zero-Touch Provisioning (ZTP). To deploy an endpoint device, the network engineer does not need to visit the site. The key is to properly power on the device on-site and connect all cables; then the equipment will connect to the system itself. Configs can be loaded via DNS requests in the vendor's cloud from a connected USB drive, or you can open a hyperlink from a laptop connected to the device via Wi-Fi or Ethernet.
- Simplifying routine network administration — configurations from templates, global policies, customizable centrally for as few as five branches or as many as 5,000. All from a single location. To avoid a long road — a very convenient option for automatic rollback to the previous configuration.
- Application-level traffic management — ensuring quality and continuously updating application signatures. Policies are configured and applied centrally (no need to write and update route maps for each router as before). It's clear who is sending what and where.
- Network segmentation. Independent isolated VPNs across the entire infrastructure — each with its own routing. By default, traffic between them is closed, allowing access only to specific types of traffic in designated network nodes, for instance, passing everything through a large firewall or proxy.
- Visibility of network performance history — how applications and channels were functioning. Very useful for analyzing and resolving issues before users start complaining about application instability.
- Visibility across channels — whether they are worth their cost, whether two different operators are actually connected to your site, or if they are passing through the same network and degrading/failing simultaneously.
- Visibility for cloud applications and steering traffic through various channels based on it (Cloud Onramp).
- One piece of hardware contains both a router and a firewall (more specifically, an NGFW). Fewer devices mean lower costs for deploying a new branch.
Components and architecture of SD-WAN solutions.
End devices — WAN routers, which can be hardware or virtual.
Orchestrators — network management tools. They set parameters for end devices, traffic routing policies, and security functionalities. Configurations are automatically sent through the control network to the nodes. Simultaneously, the orchestrator listens to the network and conducts monitoring — availability of devices, ports, communication channels, and interface load.
Analytical tools. They create reports based on data collected from end devices: history of channel performance, network applications, node availability, etc.
Controllers are responsible for implementing traffic routing policies on the network. Their closest equivalent in traditional networks can be considered a BGP Route Reflector. The global policies that the administrator configures in the orchestrator cause the controllers to modify their routing tables and send updated information to end devices.
What IT services gain from SD-WAN:
- The backup channel is constantly in use (not idle). It becomes less expensive, as you can afford two smaller bandwidth channels.
- Automatic switching of application traffic between channels.
- Administrator time: you can globally develop the network rather than crawling through each hardware device with configurations.
- The speed of bringing new branches online. It is significantly higher.
- Fewer downtimes during the replacement of failed equipment.
- Quick reconfiguration of the network for new services.
What businesses gain from SD-WAN:
- Guaranteed operation of business applications over a distributed network, including through open internet channels. This is about business predictability.
- Instant support for new business applications across the distributed network regardless of the number of branches. This is about business speed.
- Rapid and secure connection of branches in any remote locations using any connection technologies (the Internet is everywhere, while dedicated lines and VPNs are not). This is about business flexibility in location choice.
- This can be a project with delivery and commissioning, or it can be a service
with monthly payments from the IT company, telecom operator, or cloud operator. Whatever is convenient.
The benefits of SD-WAN for businesses can vary greatly; for example, one client told us that a top manager had requested a direct line with all employees of a large company and the ability to deliver content.
For us, it was like a "military operation." At that moment, we were already working on modernizing the CSPD. And when we realize that we need to be involved in equipment renovation in principle, and the technological stack has advanced, why should we engage in renewing the same technologies and services when we can move further?
The SD-WAN is installed on-site by technician teams. This is crucial for remote branches where a competent admin might not be available. You send it via mail and say: 'Plug cable 1 into box 1, cable 2 into box 2, and don’t mix them up! Don’t mix them up, #@$@%!'. If they don’t mix them up, the device connects itself to the central server, retrieves, and applies its configurations, and that office becomes a part of the company’s secure network. It’s nice not to have to travel and to justify it easily in the budget.
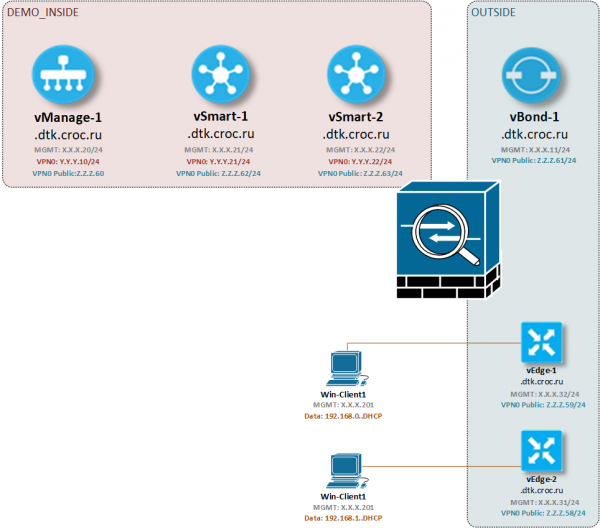
Here's the stand diagram:
A few configuration examples:
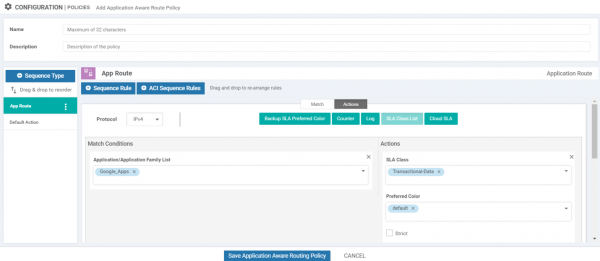
Policy — global traffic management rules. Editing the policy.
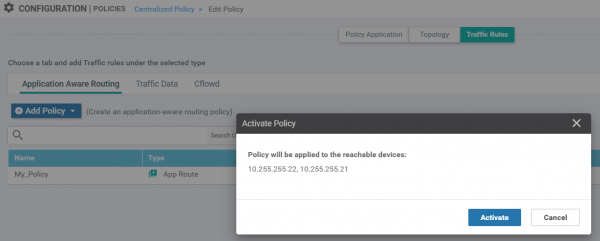
Activating the traffic management policy.
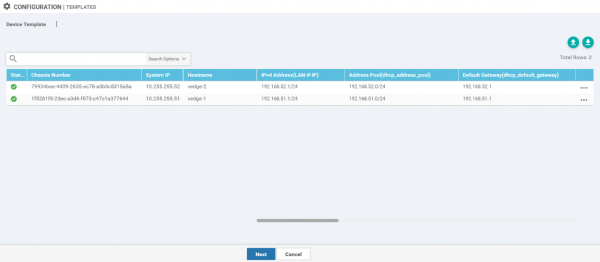
Mass configuration of main device parameters (IP addresses, DHCP pools).
Screenshots of application performance monitoring
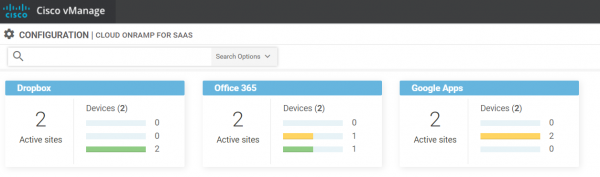
For cloud applications.
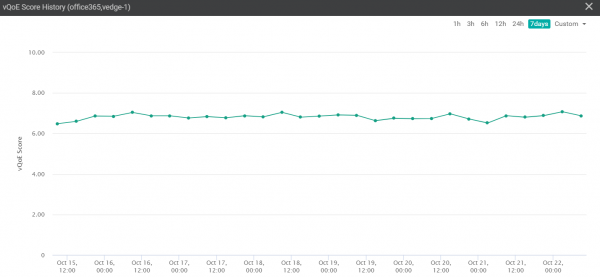
In detail for Office365.
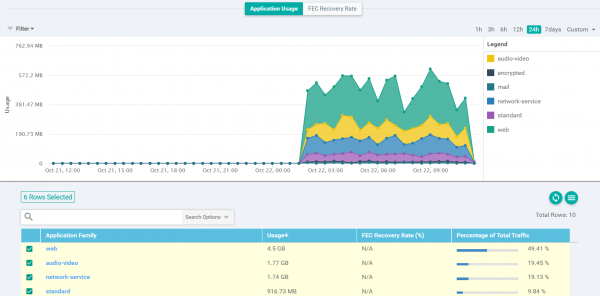
For on-prem applications. Unfortunately, we could not find any applications with errors on our stand (FEC Recovery rate is zero everywhere).
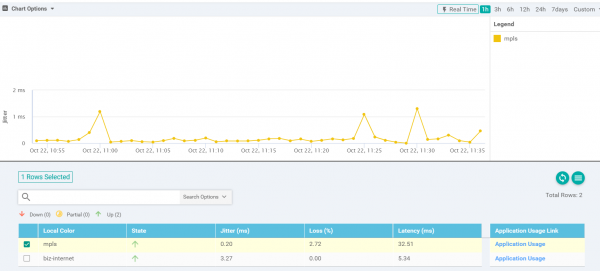
Additionally — performance of data transmission channels.
Which hardware is supported on SD-WAN
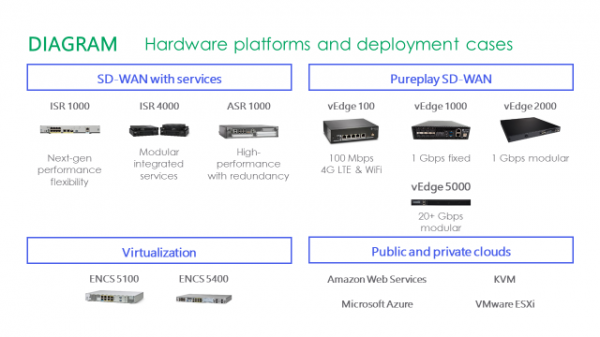
1. Hardware platforms:
- Cisco vEdge routers (formerly known as Viptela vEdge), operating under the Viptela OS.
- Integrated Services Router (ISR) series 1000 and 4000 routers, operating under IOS XE SD-WAN.
- Aggregation Services Router (ASR) series 1000 router, operating under IOS XE SD-WAN.
2. Virtual platforms:
- Cloud Services Router (CSR) 1000v, operating under IOS XE SD-WAN.
- vEdge Cloud Router, operating under the Viptela OS.
Virtual platforms can be deployed on Cisco x86 computing platforms, such as the Enterprise Network Compute System (ENCS) series 5000, Unified Computing System (UCS), and Cloud Services Platform (CSP) series 5000. Virtual platforms can also run on any x86 device using a hypervisor, such as KVM or VMware ESi.
How to onboard a new device
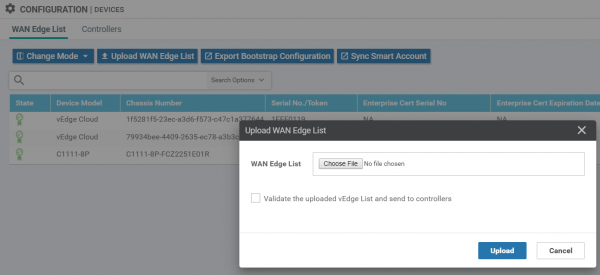
The list of licensed devices for deployment is either downloaded from the smart account in Cisco or uploaded via a CSV file. I’ll try to get more screenshots later; we currently do not have new devices for deployment.
The sequence of steps the device goes through during deployment.
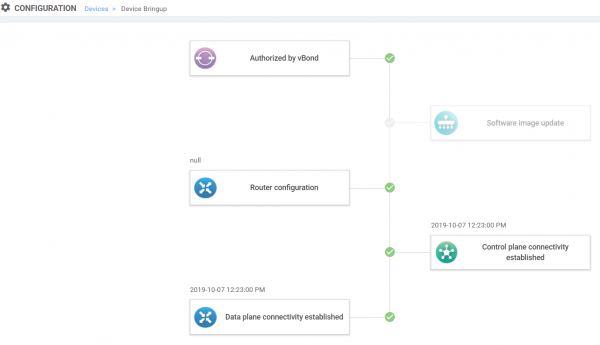
How to onboard a new device/config delivery method
Registering devices in the Smart Account.
You can upload a CSV file or add one by one:
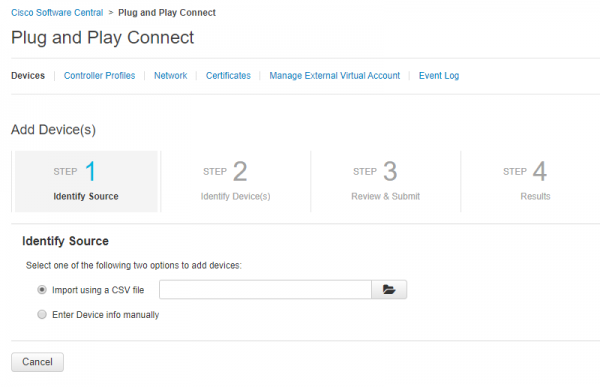
Fill in the device parameters:
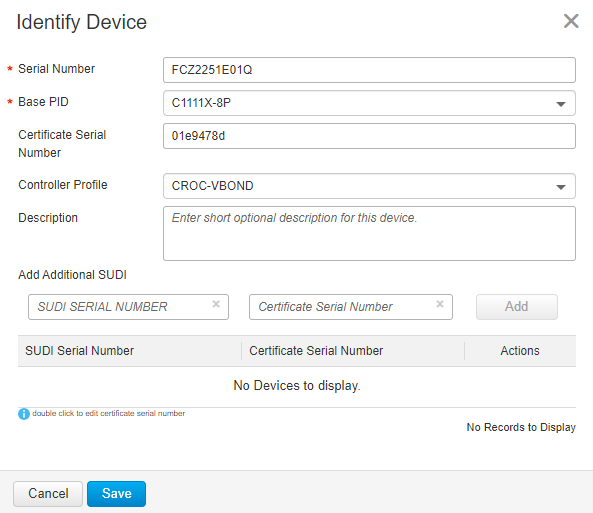
Next, in vManage, we synchronize the data with the Smart Account. The device appears in the list:
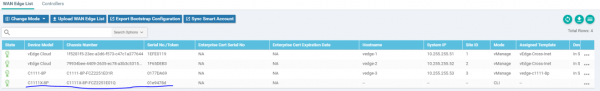
In the dropdown menu next to the device, click Generate Bootstrap Configuration
and receive the initial config:
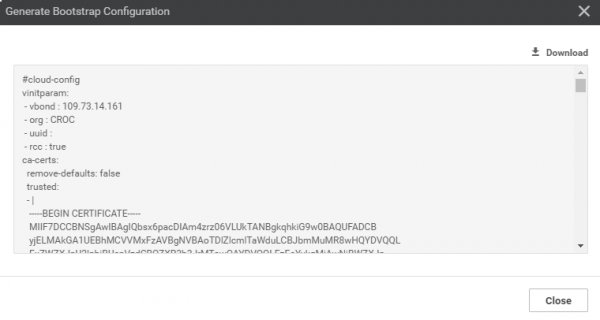
This config needs to be fed to the device. The easiest way is to connect a USB drive with the saved file named ciscosd-wan.cfg. Upon booting, the device will look for this file.
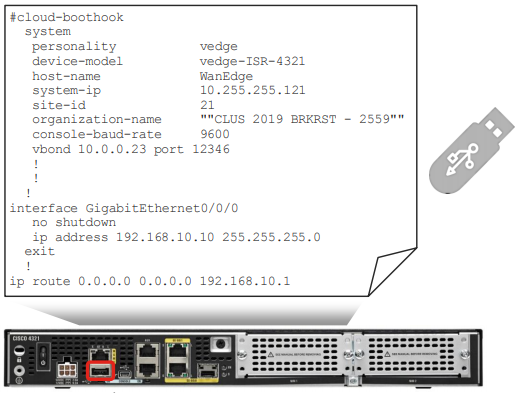
Once the initial config is received, the device will be able to reach out to the orchestrator and obtain a complete configuration from there.
Let's look at SD-Access (DNA)
SD-Access simplifies port configuration and access rights for connecting users. This is done through wizards. Port parameters are set according to groups like 'Administrators', 'Accounting', 'Printers', rather than by VLAN and IP subnets. This minimizes errors related to human factors. For example, if a company has many branches across Russia and the central office is overloaded, SD-Access allows for more tasks to be resolved locally. This includes troubleshooting tasks.
For security purposes, it is important that SD-Access enforces a clear separation of users and devices into groups and defines interaction policies between them, authorization at any client connection to the network, and ensures access rights across the network. Following this approach makes administration significantly easier.
The launch process for new offices is also simplified thanks to Plug-and-Play agents in the switches. There is no need to run to the cross-connects with a console or even to travel on-site.
Here are examples of the configuration:
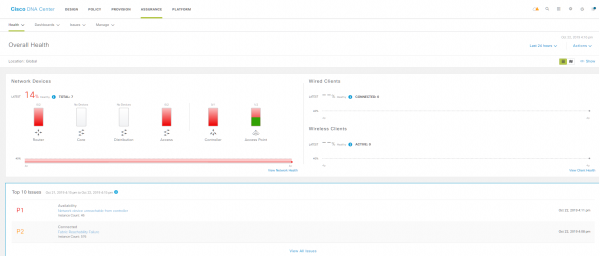
Overall status.
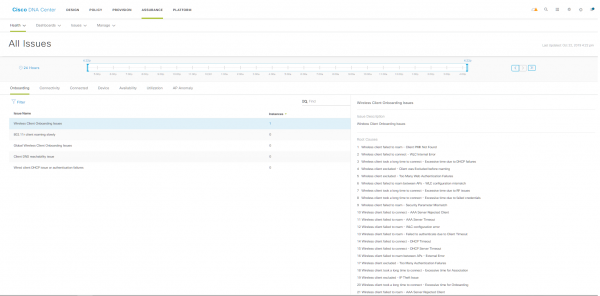
Incidents that the administrator should review.
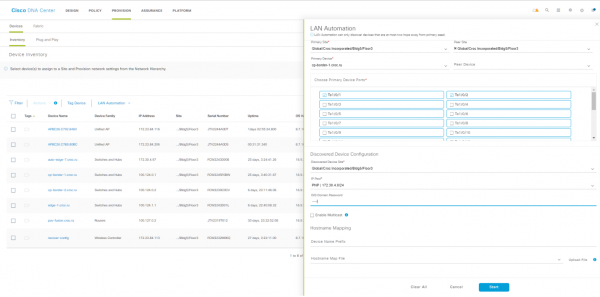
Automated recommendations on what changes to make in the configs.
Plan for integrating SD-WAN with SD-Access
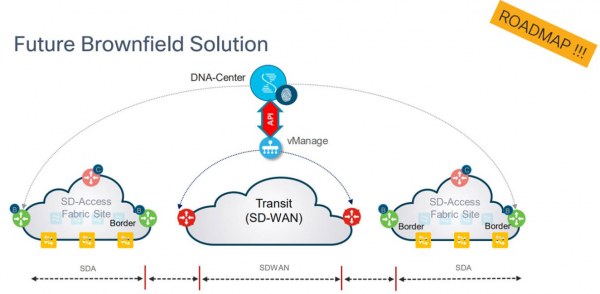
I've heard that Cisco has plans for SD-WAN and SD-Access. This should significantly reduce the hassle of managing geographically distributed and local CSPs.
vManage (SD-WAN orchestrator) is managed through the API with DNA Center (SD-Access controller).
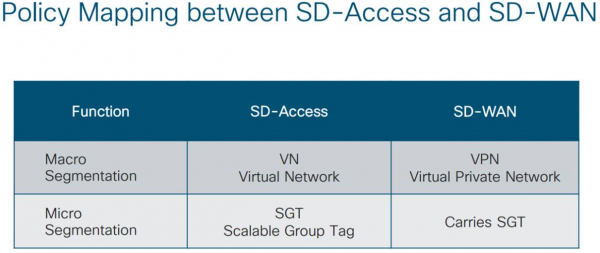
Micro- and macro-segmentation policies are mapped as follows:
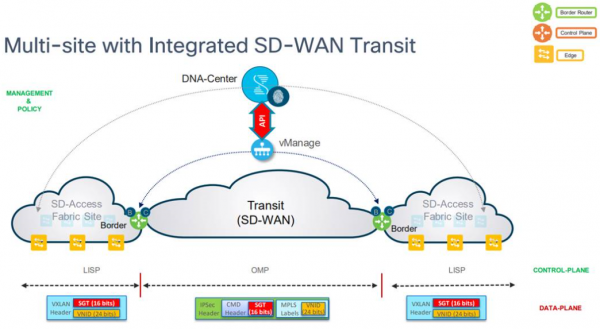
At the packet level, it looks like this:
What do people think about this?
We have been working with SD-WAN since 2016 in a dedicated lab where we test various solutions tailored for retail, banking, transportation, and industry.
We communicate a lot with real clients.
I can say that retail is already confidently testing SD-WAN, and some companies are doing this with vendors (most often with Cisco), but there are also those who are trying to solve the issue independently: they are developing their own software version that resembles SD-WAN in functionality.
Everyone wants to achieve centralized management of all the varied equipment. This serves as a single administration point for non-standard installations and standard setups for different vendors and technologies. It is important to minimize manual work because, firstly, it reduces the risk of human error when configuring equipment, and secondly, it frees up IT resources to address other tasks. Usually, the need for this understanding arises due to very long update cycles nationwide. For example, if retail is selling alcohol, constant communication is necessary for sales. An update or downtime during the day directly impacts revenue.
Currently, there is a clear understanding in retail of the tasks for which IT will use SD-WAN:
- Rapid deployment (often needed on LTE before a cable provider arrives, often needed so that a new point can be set up by an admin in the city through a government contract, and then the center just monitors and configures).
- Centralized management, communication for overseas locations.
- Reduction in telecom costs.
- Various additional services (DPI features allow prioritizing the delivery of traffic from important applications like cash registers).
- Channel management automatically, rather than manually.
And there is also compliance checking — many talk about it, but no one perceives it as a problem. Ensuring that everything works correctly fits into this paradigm as well. Many believe that the entire network technology market will move in this direction.
Banks are, in my opinion, currently testing SD-WAN rather as a new technological feature. They are waiting for the end of support for previous generations of equipment, and only then will they consider changing. Banks have a unique atmosphere regarding communication channels, so the current state of the industry doesn't bother them much. The issues lie more in other areas.
Unlike the Russian market, SD-WAN is being actively adopted in Europe. They have more expensive communication channels, and therefore European companies bring their stack to Russian divisions. In Russia, there is a certain stability because the cost of channels (even when a region is 25 times more expensive than the center) seems quite reasonable and raises no questions. Year after year, budgets for communication channels are allocated without hesitation.
Here is an example from global practice where a company saved time and money using SD-WAN on Cisco.
There is a company called National Instruments. At a certain point, they realized that the global computing network, formed as a result of merging 88 sites worldwide, was inefficient. In addition, the company lacked bandwidth and performance of the WAN. There was no balance between the company's continuous growth and the limited IT budget.
SD-WAN helped National Instruments reduce their MPLS costs by 25% (saving $450,000 by the end of 2018), while increasing bandwidth by 3,075%.
As a result of implementing SD-WAN, the company received a smart software-defined network and centralized policy management to automatically optimize traffic and application performance. — a detailed case study.
a completely crazy case of S7 relocating to another office, where it all started off difficult yet interesting — it was necessary to redo 1,500 ports. But then things went awry and, in the end, the admins became the last ones before the deadline to whom all the accumulated delays were directed.
Read more in English:
- .
- .
- .
- .
- Here is on network trends worldwide.
In Russian:
- .
- .
- .
- .
- My email, if you have any questions or want to test your tasks on our stand, is mkazakov@croc.ru.
Source: habr.com
