

According to statistics, the volume of network traffic increases by about 50% each year. This leads to an increase in the load on equipment and, in particular, raises the performance requirements for IDS/IPS. One can purchase expensive specialized hardware, but there is a cheaper option — implementing one of the open-source systems. Many novice administrators believe that installing and configuring a free IPS is quite difficult. In the case of Suricata, this is not entirely true — it can be installed and configured to respond to typical attacks with a set of free rules in just a few minutes.
Why do we need another open IPS?
For a long time, the system Snort, considered the standard, has been developed since the late nineties, so initially, it was single-threaded. Over the years, it has acquired all the modern features, such as IPv6 support, the ability to analyze application layer protocols, and a universal data access module.
The basic Snort 2.X engine learned to work with multiple cores, but it remained single-threaded and therefore cannot optimally leverage the advantages of modern hardware platforms.
The problem was resolved in the third version of the system, but its development took so long that Suricata, written from scratch, emerged on the market. In 2009, it was developed specifically as a multi-threaded alternative to Snort, equipped with IPS features out of the box. The code is distributed under the GPLv2 license, but financial partners of the project have access to a closed version of the engine. Some scalability issues in the early versions of the system arose, but they were resolved fairly quickly.
Why Suricata?
Suricata has several modules (just like Snort): capture, collection, decoding, detection, and output. By default, the captured traffic is processed in a single thread before decoding, which can put a heavier load on the system. If necessary, threads can be split in the settings and distributed across processors—Suricata is very well optimized for specific hardware, although this is no longer at the HOWTO level for beginners. It's also worth noting the advanced HTTP inspection tools based on the HTP library found in Suricata. These can also be used for traffic logging without detection. The system also supports IPv6 decoding, including IPv4-in-IPv6 tunnels, IPv6-in-IPv6, and others.
Various interfaces can be used to intercept traffic (NFQueue, IPFRing, LibPcap, IPFW, AF_PACKET, PF_RING), and in Unix Socket mode, you can automatically analyze PCAP files captured by another sniffer. Additionally, Suricata's modular architecture simplifies the integration of new components for capturing, decoding, analyzing, and processing network packets. It's also important to note that in Suricata, traffic blocking is carried out using the built-in filtering capabilities of the operating system. In GNU/Linux, there are two options for IPS operation: through the NFQUEUE queue (NFQ mode) and through zero copy (AF_PACKET mode). In the first case, packets hitting the iptables are directed to the NFQUEUE, where they can be processed at the user level. Suricata processes them according to its rules and issues one of three verdicts: NF_ACCEPT, NF_DROP, and NF_REPEAT. The first two don't require further explanation, while the last one allows marking packets and sending them to the beginning of the current iptables table. The AF_PACKET mode has higher performance but imposes several restrictions on the system: it must have two network interfaces and operate as a gateway. A blocked packet is simply not forwarded to the second interface.
An important feature of Suricata is the ability to utilize developments from Snort. Administrators can access, in particular, the Sourcefire VRT rule sets and OpenSource Emerging Threats, as well as the commercial Emerging Threats Pro. The unified output can be analyzed using popular backends, and output to PCAP and Syslog is also supported. The system settings and rules are stored in YAML format files, which are easily readable and can be processed automatically. The Suricata engine recognizes numerous protocols, so there is no need to tie rules to port numbers. Additionally, the concept of flowbits is actively practiced in Suricata rules. Session variables are used to track triggers, allowing the creation and application of various counters and flags. Many IDS see different TCP connections as separate entities and may not recognize the relationships between them that indicate the onset of an attack. Suricata aims to see the big picture and, in many cases, identifies malicious traffic distributed across different connections. We can discuss its advantages for a long time; let's move on to installation and configuration.
How to install?
We will install Suricata on a virtual server running Ubuntu 18.04 LTS. All commands must be executed as the superuser (root). The safest option is to connect to the server via SSH as a regular user and then use the sudo utility to elevate privileges. First, we need to install the packages we will need:
sudo apt -y install libpcre3 libpcre3-dev build-essential autoconf automake libtool libpcap-dev libnet1-dev libyaml-0-2 libyaml-dev zlib1g zlib1g-dev libmagic-dev libcap-ng-dev libjansson-dev pkg-config libnetfilter-queue-dev geoip-bin geoip-database geoipupdate apt-transport-httpsAdd the external repository:
sudo add-apt-repository ppa:oisf/suricata-stable
sudo apt-get update
Install the latest stable version of Suricata:
sudo apt-get install suricataIf necessary, we edit the configuration files' name, replacing the default eth0 with the actual name of the server's external interface. Default settings are stored in the file /etc/default/suricata, while user settings can be found in /etc/suricata/suricata.yaml. Configuring IDS mostly involves editing this configuration file. It contains many parameters that are named and designed similarly to those in Snort. However, the syntax is completely different, but the file is much easier to read than Snort configs, plus it is well-commented.
sudo nano /etc/default/suricata 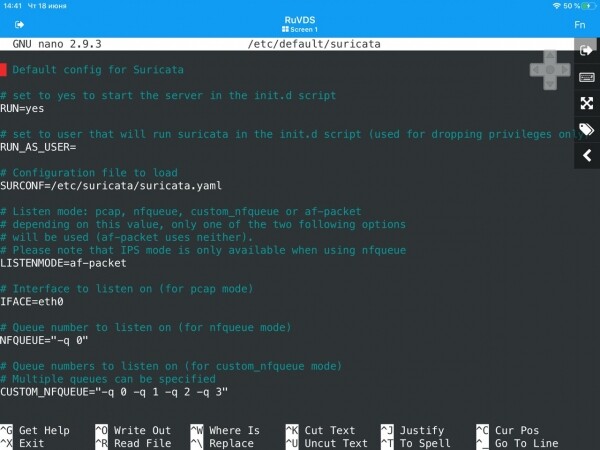
and
sudo nano /etc/suricata/suricata.yaml 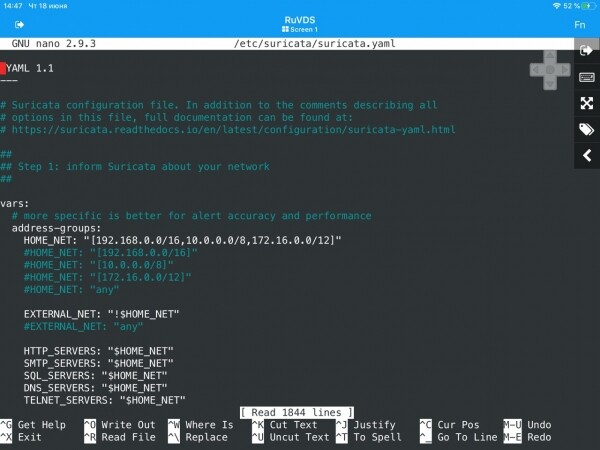
Attention! Before starting, check the values of the variables in the vars section.
To complete the setup, it is necessary to install suricata-update for updating and loading rules. This is quite simple to do:
sudo apt install python-pip
sudo pip install pyyaml
sudo pip install <a href="https://github.com/OISF/suricata-update/archive/master.zip">https://github.com/OISF/suricata-update/archive/master.zip</a>
sudo pip install --pre --upgrade suricata-update
Next, we need to run the suricata-update command to install the Emerging Threats Open ruleset:
sudo suricata-update 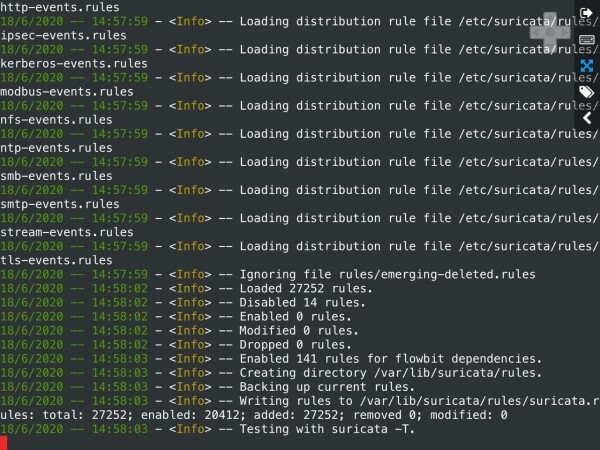
To view the list of rule sources, we execute the following command:
sudo suricata-update list-sources 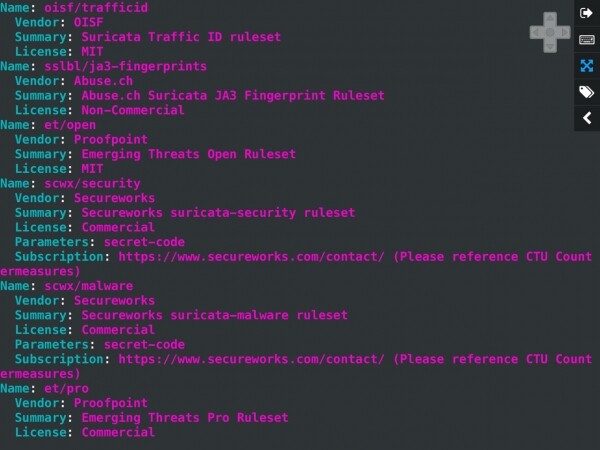
Updating rule sources:
sudo suricata-update update-sources 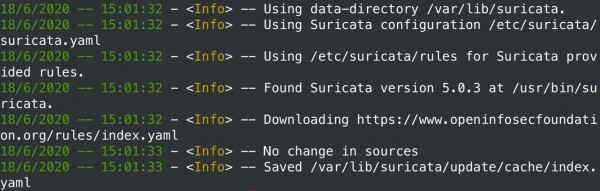
Rechecking the updated sources:
sudo suricata-update list-sourcesIf needed, you can enable the available free sources:
sudo suricata-update enable-source ptresearch/attackdetection
sudo suricata-update enable-source oisf/trafficid
sudo suricata-update enable-source sslbl/ssl-fp-blacklist
After this, it is necessary to update the rules again:
sudo suricata-updateAt this point, the installation and initial configuration of Suricata on Ubuntu 18.04 LTS can be considered complete. Next, the most interesting part begins: in the following article, we will connect the virtual server to the office network via VPN and start analyzing all incoming and outgoing traffic. Special attention will be paid to blocking DDoS attacks, malware activities, and attempts to exploit vulnerabilities in services accessible from public networks. For clarity, attacks of the most common types will be simulated.
Source: habr.com
