

Information security has separated from telecommunications into its own industry with its own specifics and equipment. However, there is a lesser-known class of devices that stands at the intersection of telecom and infosec — network packet brokers (Network Packet Broker), also known as load balancers, specialized/monitoring switches, traffic aggregators, Security Delivery Platforms, Network Visibility, and so on. As a Russian developer and manufacturer of such devices, we are eager to share more details about them.
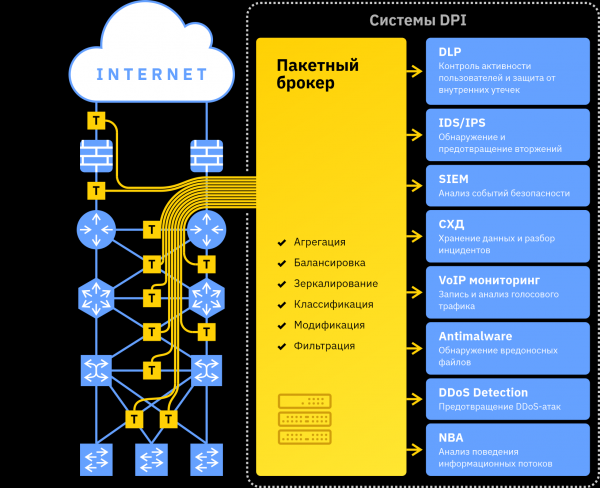
Application area and tasks solved
Network packet brokers are specialized devices that have found their greatest use in information security systems. This class of devices is relatively new and less common in the established network infrastructure compared to switches, routers, etc. The pioneer in the development of this type of device was the American company Gigamon. Currently, the number of players in this market has significantly increased (including similar solutions from the well-known test suite manufacturer — IXIA), but knowledge of such devices remains limited to a narrow circle of professionals. As noted earlier, even the terminology lacks clarity: names vary from 'network transparency assurance systems' to simply 'balancers.'
In developing network packet brokers, we faced the challenge that, in addition to analyzing functional development directions and testing in labs/test zones, it is necessary to simultaneously educate potential consumers about the existence of this class of equipment, as not everyone is aware of it.
Fifteen to twenty years ago, there was little traffic on the network, and it mainly consisted of insignificant data. However, almost mirrors : the speed of internet connection increases annually by 50%. The volume of traffic is also steadily growing (the graph shows a forecast from 2017 by Cisco, source: Cisco Visual Networking Index: Forecast and Trends, 2017–2022):
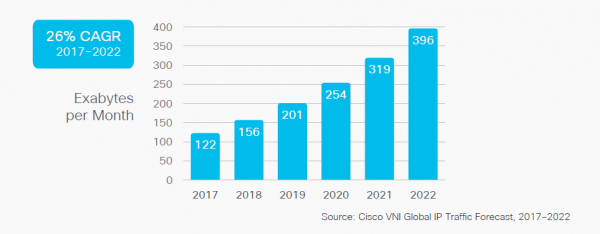
With increased speed comes the growing importance of circulating information (including trade secrets and so-called personal data) and the overall functionality of the infrastructure.
Consequently, an information security industry has emerged. The industry responded to this by creating a wide range of deep traffic analysis (DPI) devices: from DDoS attack prevention systems to security information and event management systems, including IDS, IPS, DLP, NBA, SIEM, Antimailware, and so on. Typically, each of these tools is software installed on a server platform, with each program (analysis tool) requiring its own server platform; different software vendors develop them, and significant computational resources are necessary for analysis at L7.
When building an information security system, it is necessary to address a number of key tasks:
- How to transmit traffic from the infrastructure to the analysis systems? (Initially designed SPAN ports are insufficient in both quantity and performance in modern infrastructure.)
- How to distribute traffic among different analysis systems?
- How to scale systems when a single instance of the analyzer lacks the performance to process all incoming traffic?
- How to monitor 40G/100G interfaces (and in the near future, 200G/400G), as analysis tools currently only support interfaces of 1G/10G/25G?
And the following related tasks:
- How to minimize non-target traffic that does not require processing but ends up on analysis tools and consumes their resources?
- How to process encapsulated packets and packets with equipment service tags, whose preparation for analysis turns out to be either resource-intensive or impossible to implement at all?
- How to exclude from analysis certain traffic that does not fall under security policy regulations (for example, the traffic of executives).
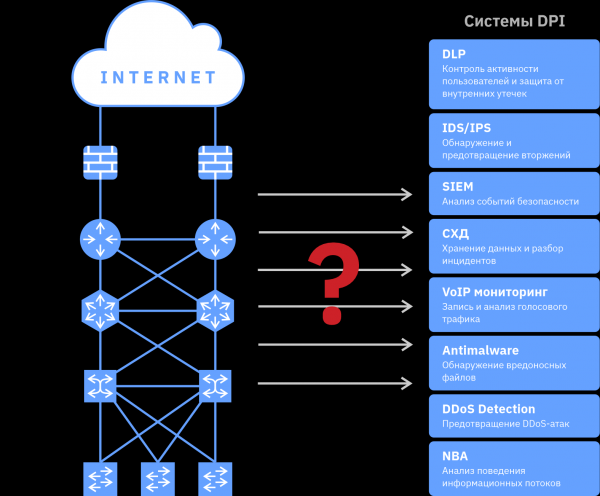
As is well known, demand creates supply, and in response to these needs, network packet brokers began to emerge.
General description of network packet brokers.
Packet brokers operate at the packet level, making them similar to standard switches. The main difference from switches is that the rules for distributing and aggregating traffic in packet brokers are entirely defined by configurations. Packet brokers lack standardized forwarding table constructions (MAC tables) and protocols for communication with other switches (such as STP), so the range of possible settings and comprehensible fields is much wider. A broker can evenly distribute traffic from one or several input ports across a designated range of output ports with a function for even load balancing at the output. Rules can be set for copying, filtering, classification, deduplication, and modification of traffic. These rules can be applied to different groups of input ports of the packet broker and can also be applied sequentially within the device itself. An important advantage of the packet broker is its ability to process traffic at full stream speed while maintaining session integrity (in the case of traffic balancing across several similar DPI systems).
Maintaining session integrity involves sending all packets of a transport layer session (TCP/UDP/SCTP) to a single port. This is crucial because DPI systems (typically software running on a server connected to the output port of the packet broker) analyze traffic content at the application level, and all packets sent/received by a single application must arrive at the same instance of the analyzer. If packets of one session are lost or distributed among various DPI devices, each device will find itself in a situation similar to reading a disjointed text, picking words from it. Most likely, the text will not make sense.
Thus, being focused on information security systems, packet brokers have functionalities that help connect DPI software suites to high-speed telecommunication networks and reduce the load on them: they perform preliminary filtering, classification, and preparation of traffic to simplify subsequent processing.
Moreover, since packet brokers provide a wide range of statistics and are often connected to various network points, they also play a role in diagnosing issues with the network infrastructure itself.
Basic Functions of Packet Brokers
The term 'specialized/monitoring switches' arose from their basic purpose: to collect traffic from the infrastructure (usually using passive optical splitters TAP and/or SPAN ports) and distribute it among analysis tools. Between different types of systems, traffic is mirrored (duplicated), while between similar types, it is balanced. The basic functions typically include filtering by fields up to L4 (MAC, IP, TCP/UDP port, etc.) and aggregating several lightly loaded channels into one (for example, for processing on a single DPI system).
This functionality addresses the fundamental task of connecting DPI systems to the network infrastructure. Packet brokers from various manufacturers, which limit themselves to basic functionality, can process up to 32 100G interfaces in 1U (more interfaces physically cannot fit on the front panel of 1U). However, they do not alleviate the load on analysis tools, and for complex infrastructures, they fail to meet even the basic functional requirements: a session distributed across multiple tunnels (or equipped with MPLS labels) may become unbalanced across different instances of the analyzer and, overall, fall out of analysis.
In addition to adding 40/100G interfaces and, consequently, increasing performance, packet brokers are actively evolving in providing fundamentally new capabilities: from header-based balancing of tunnels to traffic decryption. Unfortunately, such models cannot boast terabit performance, but they allow for the construction of a truly high-quality and technically 'beautiful' information security system, in which each analysis tool receives only the information it requires in the most suitable form for analysis.
Advanced Functions of Packet Brokers
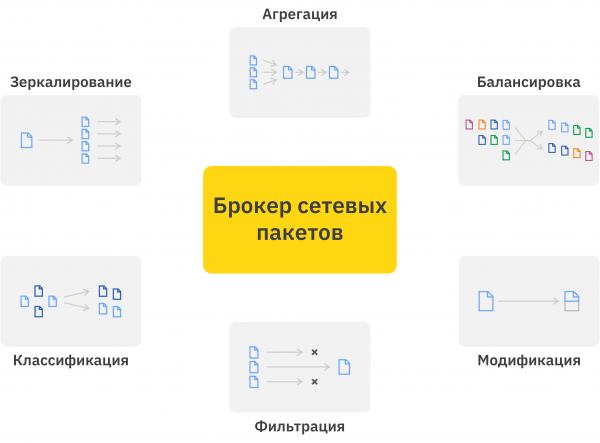
1. The aforementioned balancing based on embedded headers in tunneled traffic.
Why is this important? Let's consider three aspects that may be critical together or individually:
- ensuring even load balancing with a small number of tunnels. If there are only 2 tunnels at the security system connection point, it won't be possible to balance them by external headers across 3 server platforms while maintaining session continuity. Consequently, traffic flows unevenly in the network, and directing each tunnel to a separate processing unit will require excessive performance from the latter;
- ensuring the integrity of sessions and streams of multi-session protocols (e.g., FTP and VoIP), where packets find themselves in different tunnels. The complexity of the network infrastructure is continually increasing: redundancy, virtualization, simplifying administration, and so on. On one hand, this enhances reliability in data transmission, while on the other hand, it complicates the operations of security systems. Even with sufficient performance from analyzers for processing a dedicated channel with tunnels, the problem remains unsolvable because part of the packets from the user session is transmitted through a different channel. Whereas some infrastructures are still making efforts to maintain the integrity of sessions, multi-session protocols can take entirely different routes;
- balancing in the presence of MPLS, VLANs, individual equipment labels, etc. While they are not exactly tunnels, equipment with basic functionality can interpret this traffic not as IP and balance it by MAC addresses, once again disrupting the uniformity of balancing or the integrity of sessions.
The packet broker analyzes external headers and sequentially navigates through pointers to the innermost IP header, balancing based on it. As a result, the number of streams significantly increases (thus enabling more uniform balancing across a greater number of platforms), and the DPI system receives all packets of the session and all related sessions of multi-session protocols.
2. Traffic modification.
One of the broadest functionalities in terms of possibilities, the number of sub-functions and their application options are numerous:
- removing payload means that only the headers of the packets are sent to the analysis tool. This is relevant for analysis tools or types of traffic where the content of the packets is either irrelevant or cannot be analyzed. For example, for encrypted traffic, the parameter data of the exchange (who, with whom, when, and how much) may be of interest, while the payload is essentially garbage that occupies the channel and the computational resources of the analyzer. There can be variations where the payload is truncated starting from a specified offset – this provides additional opportunities for analysis tools;
- detunneling, specifically removing headers that signify and identify tunnels. The goal is to reduce the burden on analysis tools and enhance their efficiency. Detunneling can be performed based on a fixed offset or with dynamic analysis of headers and determination of the offset for each packet;
- removing certain parts of the packet headers: MPLS labels, VLAN, specific fields from third-party equipment;
- masking part of the headers, for example, masking IP addresses to ensure traffic anonymization;
- adding service information to the packet: timestamps, input port, traffic class labels, etc.
3. Deduplication – clearing out duplicate traffic packets sent to analysis tools. Duplicate packets most often arise due to the nature of the connection to the infrastructure – traffic may pass through multiple analysis points and get mirrored from each. There is also the issue of resending undelivered TCP packets, but if there are many, it is more of a network quality monitoring concern rather than an information security issue.
4. Advanced filtering functions – from searching for specific values at a given offset to signature analysis across the entire packet.
5. Generation of NetFlow/IPFIX – gathering a wide range of statistics from the passing traffic and sending it to analysis tools.
6. Decryption of SSL traffic, works provided that the certificate and keys are preloaded into the packet broker. However, this significantly reduces the load on analysis tools.
There are many more useful and marketing functions, but the main ones are probably listed.
The development of intrusion detection systems (DDoS attacks) into prevention systems, as well as the implementation of active DPI tools, required a shift from passive integration (through TAP or SPAN ports) to active integration (in-line). This situation increased reliability requirements (as failure in this case leads to the entire network's operational disruption rather than just the loss of control over information security) and resulted in the replacement of optical splitters with optical bypasses (to address the issue of network operational dependency on the functionality of information security systems), while the main functionality and requirements remained unchanged.
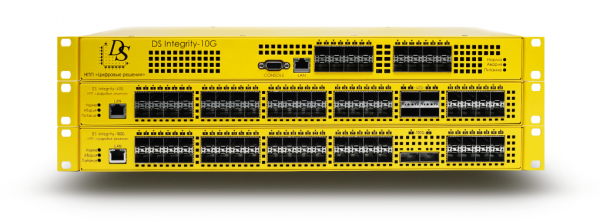
We developed DS Integrity network packet brokers with 100G, 40G, and 10G interfaces, from design and circuitry to built-in software. Unlike other packet brokers, our functions for modifying and balancing nested tunnel headers are implemented in hardware, operating at full port speed.
Source: habr.com
