

, that 80% of emails in the world are spam. This means emails that are completely unnecessary for the recipient (which is unfortunate). But as if that weren't enough, among spam, there are often messages sent with malicious intent: for example, to steal or delete data, or to extort money.
KDPV:
As we know, for an email to actually harm computer systems, merely delivering the email to the recipient is usually not enough. A 'cooperative opponent' is required, i.e., the user must take actions that will lead to the malicious intent being executed.
Usually, this action is 'opening' the attachment in the email, meaning manually launching the file with the appropriate processing program within the user's operating system.
What is even more unfortunate is that the cooperative opponent is not a rare bird, and our spammer-criminal can certainly count on them.
And this leads to
In short, our accountant opens an account, and instead of an account, there is a virus.
Malicious emails, of course, have important differences. But hoping for the attentiveness and awareness of users is a bad idea. Even extravagant concerts on the theme of 'don't open this' with fireworks and a solo vocal performance from the CEO (the composition 'Polymers') eventually fade from the memory of an office worker.
Of course, well-configured systems will protect us from most of these attacks. But the key word is still 'most.' No one can provide a 100% guarantee; and when it comes to the user, reinforcing them, as one of the weakest points in systems, is a good deed.
In the realm of computer crime, technology and social engineering go hand in hand. The attacker realizes that it's difficult to pretend to be someone the user trusts unconditionally, and is therefore forced to use other tactics: intimidation, coercion, imitating recognized authorities, and/or using corresponding false titles – for example, sending emails on behalf of government agencies and large companies.
And as the ancients teach us: if we cannot defeat them, we must lead them. Indeed, how are we worse than spammers? We are much better! We even have more opportunities. And the task itself will require only minimal programming skills and will hardly affect existing systems.
Disclaimer: the author is not a spammer, and a spammer is not the author. The author is solely on the side of good.
The task is very simple:
we will send emails to our users that resemble malicious ones. In the attachments to these emails, we will include documents that say in large letters, “DO NOT OPEN DOCUMENTS FROM SUCH EMAILS. Be more careful and cautious.”
Thus, the following conditions:
Condition 1. Emails must be different. If we send the same email to everyone each time, it will be no different from regular meeting reminders, to which users have a strong immunity. We must stimulate the user's learning system. This leads to the following conditions:
Condition 2. Emails must look like real ones. Sending emails from the company "Meat Company" or Barack Obama is possible, but ineffective. It makes sense to use real (and different!) names of organizations and authorities;
Condition 3. There are also it is important that the emails appear slightly strange. They should be somewhat suspicious to trigger the user's suspicions and activate the learning system in the brain;
Condition 4. And with all this, the emails must attract attention and provoke. Well, this is simple; we don't even need to come up with anything: spammers have already done everything for us. "Fines", "Court Decisions", and even just "Documents" in attachments, "Penalties", "Recalculation", "Charges" in the subject, and many words like "Urgent", "Immediately", "Must", "Pay" in the text – and the matter is settled.
To implement this magical set, minimal programming skills and a boring evening will be required. The author used Python 3 (because it was necessary to practice) and JS (for data collection, right from the browser console). However, most of the code can be easily implemented with native OS tools (bash, cmd), but you might struggle with encodings.
It is worth noting that the idea itself does not belong to the author; it was borrowed from a large international company. Nevertheless, the idea is so obvious that, upon hearing it, the author rushed to implement it exclaiming, 'Why didn't I think of this earlier?'
So, first and foremost, we need the components to compose the letter. Let's start with the From field — who will threaten our timid users? Well, who: undoubtedly banks, tax authorities, courts, and various strange LLCs. We might as well add templates for future auto-completion, like JSC. CmpNmF. See from.txt
Now we need, essentially, names. LLC Chamomile and Vector, as well as the endlessly repeating 'Moscow Court', are unlikely to resonate with anyone.
Fortunately, the internet offers us amazing opportunities for gathering information. For example, can be easily obtained using a simple JavaScript command right in the browser console, like:
for (let el of document.getElementById("mw-content-text").querySelectorAll("li")) {console.log(el.innerText;)}This way, we can quickly gather a great database for our tasks (especially since the author has already done this for you 🙂). We'll save it as Plain text; a database for this task is overkill. The project uses UTF-8 encoding with BOM, in case of the usage of the most specific characters. See the txt files with corresponding names.
Next, we need to generate a valid (according to the standard, but not necessarily existing) sender email address, so that our letter displays correctly and is forwarded appropriately. For some names, the author used fixed domains; for others, auto-generation from the name using a transliteration library, like LLC 'Vector' -> warning@ooovektor.ru. The mailbox name is taken from a list in the code and is also intended to instill fear: 'vzyskanie', 'shtraf', 'dolg', 'alarm', and other 'zapros'.
Now — the subject of the letter.
The subject must definitely grab attention; otherwise, the letter will go unnoticed. Let your inner accountant scarecrow have free rein, and it will work: 'Closure of account(s) (CmpNm)', 'To the Chief Accountant (CmpNm)', 'Demand (for CmpNm)', 'Pay immediately (!!!)' and other mischief.
See subj.txt. Add to taste, mix, do not shake.
The text of the email should be somewhat strange. We have already captured the user's attention; now our task is to raise suspicions. Therefore, there's no need to be careful in this respect. Let’s borrow threatening phrases from spammers and combine them at random; absolute accuracy will only hinder us. It will result in nonsense like:
(important) Information (LLC "TEST") Regarding the account in the context of legal proceedings
 please open the attached documents
 ruling attached
See msg.txt. Contributions are welcome.
And finally, the attachment. The project currently provides for 3 types of attachments: pdf, doc, docx. Files are copied from samples without changing their content, and the attachment file is assigned a name from the list (e.g., "Resolution," "Court Decision," etc., see flnms.txt). For the first two types, the size is generated randomly by adding zeros at the end of the file. This does not work for docx (although after the recovery procedure, Word opens the file; LibreOffice, for example, opens docx files with added external files via archiving interface without any complaints).
And we will get this kind of miracle:
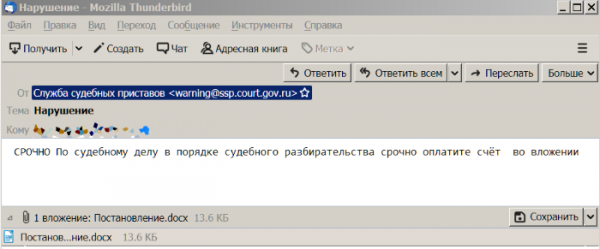
You can send:
gen_msg.py buh@oootest.ru
So, that’s all. An hour’s work, and the benefits… And there will be benefits. Because theory is dry, but the tree of life is lushly green – explanations are overlooked, reminders are forgotten, and people acquire skills only through practice. It’s better for us to be teachers than to restore everything from backups later, right?
Only registered users can participate in the survey. , please.
Have you tried it on your users? What were the results?
0,0%No one bit; they deleted it without questions.
0,0%Some reported suspicious emails but did not open the attachments.
50,0%Some opened the attachments (I’ll explain in the comments what happened next).
50,0%I got scolded by management.
6 users voted. 21 users abstained.
Source: habr.com
