

is an analytical solution in the field of cybersecurity that provides comprehensive threat monitoring in a distributed network. The core of StealthWatch's operation involves the collection of NetFlow and IPFIX from routers, switches, and other network devices. As a result, the network becomes a sensitive sensor, allowing administrators to see beyond the reach of traditional network security methods, such as Next Generation Firewall.
In previous articles, I have already written about StealthWatch: , as well as . Now, I suggest moving forward and discussing how to work with alarms and investigate security incidents generated by the solution. I will provide 6 examples that I hope will give a good indication of the product's usefulness.
First, it should be noted that StealthWatch has a certain distribution of triggers across algorithms and feeds. The former are different types of alarms (notifications), which, when triggered, can reveal suspicious activity in the network. The latter are security incidents. This article will cover 4 examples of algorithm triggers and 2 examples of feeds.
1. Analyzing the most significant interactions within the network
The initial step in configuring StealthWatch is to define hosts and networks by groups. In the web interface, the tab Configure > Host Group Management should be used to sort networks, hosts, and servers into their respective groups. Custom groups can also be created. By the way, analyzing interactions between hosts in Cisco StealthWatch is quite convenient, as not only can search filters for flows be saved, but also the results themselves.
To start, you should navigate to the tab in the web interface Analyze > Flow Search. Then, you should set the following parameters:
- Search Type — Top Conversations (most popular interactions)
- Time Range — 24 hours (time interval, another can be used)
- Search Name — Top Conversations Inside-Inside (any meaningful name)
- Subject — Host Groups → Inside Hosts (source — group of internal nodes)
- Connection (you can specify ports, applications)
- Peer — Host Groups → Inside Hosts (destination — group of internal nodes)
- In Advanced Options, you can additionally specify the collector from which the data is viewed, the sorting output (by bytes, flows, etc.). I will leave it as default.
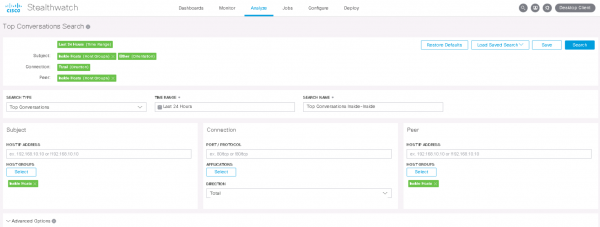
After clicking the button Search a list of interactions is provided, which are already sorted by the volume of transmitted data.
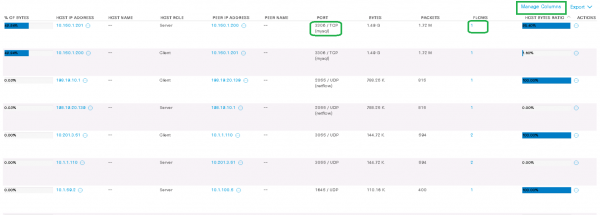
In my example, the host 10.150.1.201 (server) transmitted 1.5 GB traffic to the host 10.150.1.200 (client) via the mysqlprotocol. The button Manage Columns allows you to add more columns to the displayed data.
Next, at the administrator's discretion, a custom rule can be created that will constantly trigger for such interactions and notify via SNMP, email, or Syslog.
2. Analyzing the slowest client-server interactions within the network for latency
Tags SRT (Server Response Time), RTT (Round Trip Time) allow you to determine server delays and overall network latency. This tool is especially useful when you need to quickly identify the causes of user complaints about slow-running applications.
Note: almost all Netflow exporters cannot send SRT, RTT tags, so often to see such data on FlowSensor, you need to configure the traffic copy sending from network devices. FlowSensor, in turn, provides extended IPFIX to FlowCollector.
It is more convenient to conduct this analytics in the Java application StealthWatch, which is installed on the administrator's computer.
Right-click on Inside Hosts and go to the tab Flow Table.
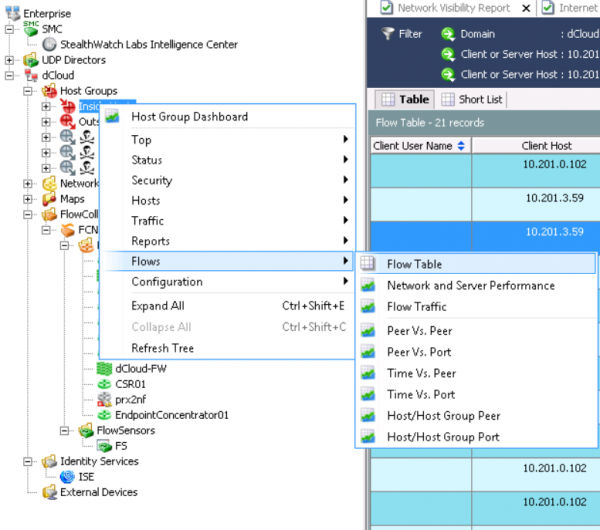
Click on Filter and set the necessary parameters. For example:
- Date/Time — For the last 3 days
- Performance — Average Round Trip Time >=50ms
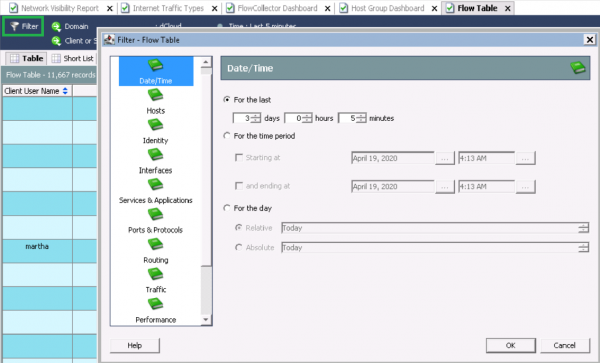
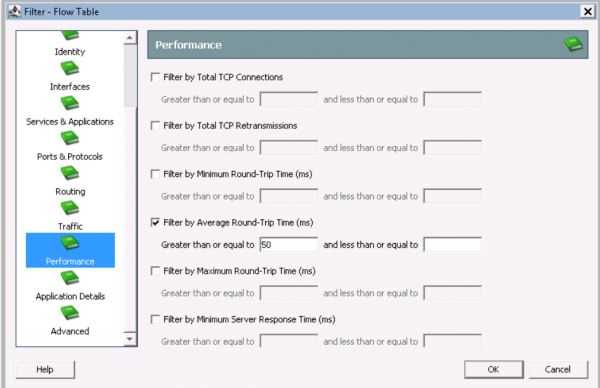
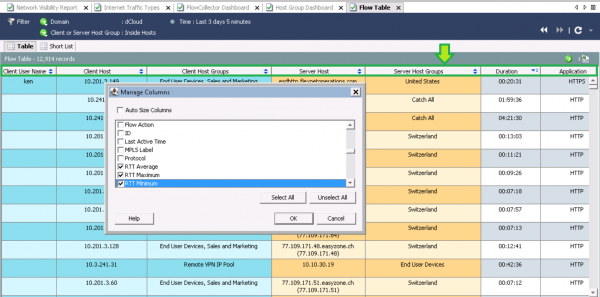
After displaying the data, you should add the desired RTT, SRT fields. To do this, click on the column in the screenshot and right-click to select Manage Columns. Then click on the RTT, SRT parameters.
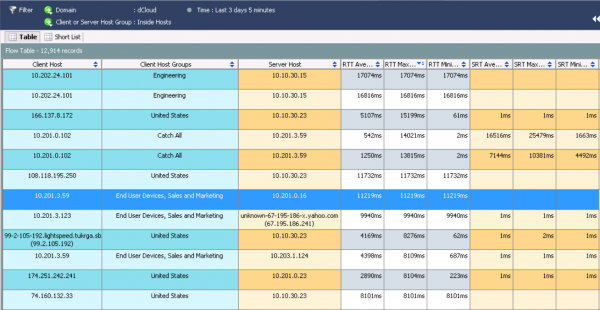
After processing the request, I sorted by RTT average and saw the slowest interactions.
To drill down into detailed information, right-click on the flow and select Quick View for Flow.
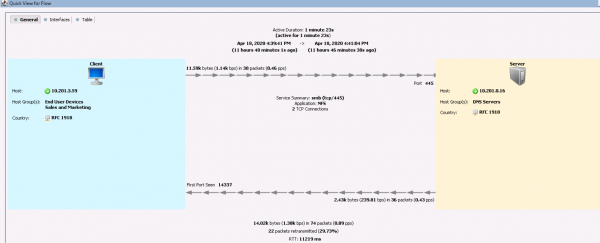
This information indicates that the host 10.201.3.59 from the group Sales and Marketing via the NFS calls has been sending data to the DNS server for 1 minute and 23 seconds with just terrible latency. In the tab Interfaces you can find out from which Netflow exporter the data was received. The tab Table displays more detailed information about the interaction.
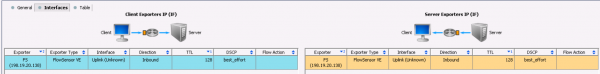
Next, you should find out which devices are sending traffic to FlowSensor, and the problem is likely there.
Moreover, StealthWatch is unique in that it performs deduplication data (combines the same streams). Consequently, it is possible to collect from almost all Netflow devices without worrying about excessive duplicate data. On the contrary, this scheme helps identify where the most significant delays occur.
3. Audit of HTTPS Cryptographic Protocols
ETA (Encrypted Traffic Analytics) — a technology developed by Cisco that allows for the detection of malicious connections in encrypted traffic without decryption. Moreover, this technology enables detailed analysis of HTTPS versions TLS and cryptographic protocols used during connections. This functionality is particularly useful for identifying network nodes that utilize weak cryptographic standards.
Note: before proceeding, the network app must be installed on StealthWatch — ETA Cryptographic Audit.
We go to the Dashboards → ETA Cryptographic Audit and select the group of hosts to analyze. For an overview, let’s choose Inside Hosts.
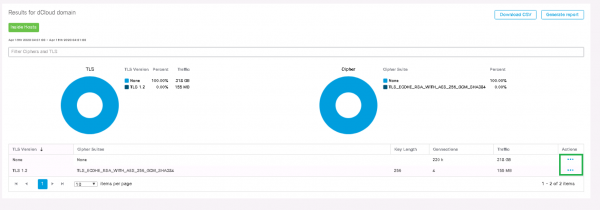
It can be observed that the TLS version and the corresponding cryptographic standard are displayed. Following the familiar layout in the column Actions we proceed to the View Flows and a search will start in a new tab.
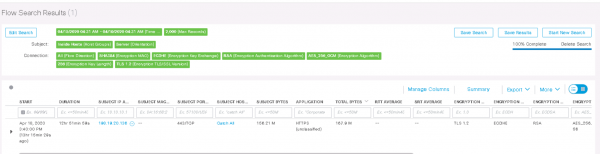
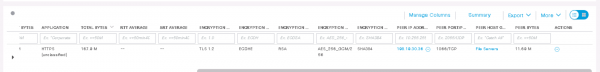
From the output, it is evident that the host 198.19.20.136 has used HTTPS with TLS 1.2 for 12 hours where the encryption algorithm AES-256 and hash function SHA-384. Thus, ETA helps identify weak algorithms in the network.
4. Network Anomaly Analysis
Cisco StealthWatch can recognize traffic anomalies in the network using three tools: Core Events (security events), Relationship Events (events of interactions between segments, network nodes) and behavioral analysis.
Behavioral analysis, in turn, allows for constructing a behavioral model for a specific host or group of hosts over time. The more traffic passes through StealthWatch, the more accurate the triggers will be thanks to this analysis. Initially, the system may trigger incorrectly often, so the rules need to be manually adjusted. I recommend not paying attention to these events for the first few weeks, as the system will self-tune, or alternatively, add these to exceptions.
Below is an example of a pre-configured rule Anomaly, which states that the event will trigger without an alarm if a host in the Inside Hosts group interacts with a group of Inside Hosts and the traffic exceeds 10 megabytes in 24 hours..
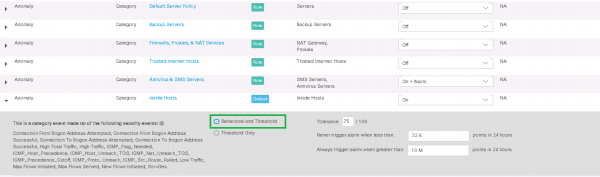
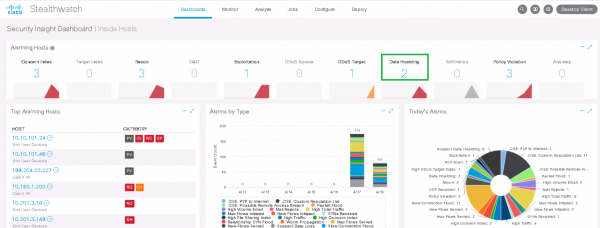
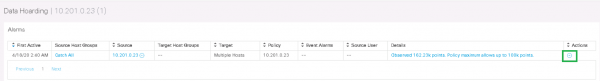
For example, let’s take the alarm Data Hoarding, which means that some source/destination host downloaded/uploaded an unusually large amount of data from a group of hosts or a host. We click on the event and drill down into the table where the triggering hosts are specified. Next, we select the host of interest in the column Data Hoarding.
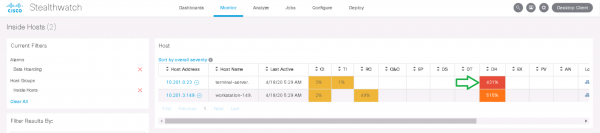
An event is displayed, indicating that 162k 'points' were detected, while the policy allows for 100k 'points' — these are internal metrics of StealthWatch. In the column Actions click View Flows.
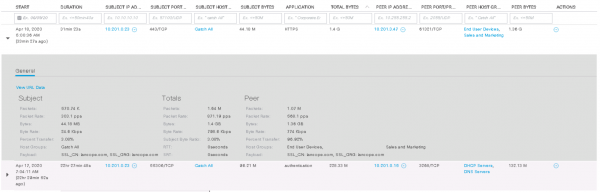
We can observe that the host interacted overnight with the host 10.201.3.47 from the department Sales & Marketing via the HTTPS and downloaded 1.4 GB. This example may not be entirely successful, but the detection of interactions involving several hundred gigabytes is carried out in exactly the same way. Therefore, further investigation of anomalies may lead to interesting results.
Note: in the SMC web interface, data in the tabs Dashboards is displayed only for the last week, and in the tab Monitor for the last 2 weeks. To analyze older events and to generate reports, you need to work with the Java console on the administrator's computer.
5. Finding internal network scans
Now let's consider a few examples of feeds — security incidents. This functionality is of more interest to security experts.
There are several predefined types of scanning events in StealthWatch:
- Port Scan — the source scans multiple ports of the destination node.
- Addr tcp scan — the source scans an entire network on the same TCP port, changing the destination IP address. During this, the source receives TCP Reset packets or does not receive any responses at all.
- Addr udp scan — the source scans an entire network on the same UDP port, changing the destination IP address. During this, the source receives ICMP Port Unreachable packets or does not receive any responses at all.
- Ping Scan — the source sends ICMP requests to an entire network in order to seek responses.
- Stealth Scan tcp/udp — the source used the same port to connect to multiple ports on the destination node at the same time.
For more convenient finding of all internal scanners at once, there is a network app for StealthWatch — Visibility Assessment. By going to the tab Dashboards → Visibility Assessment → Internal Network Scanners you will see security incidents related to scanning from the last 2 weeks.
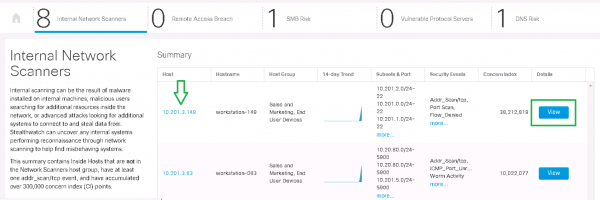
Clicking the button Details, the beginning of the scanning of each network, traffic trends, and corresponding alarms will be visible.
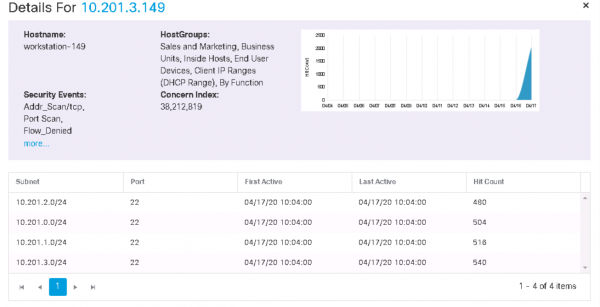
You can then “dive” into the host from the tab in the previous screenshot and see security events, as well as activity for the past week for this host.
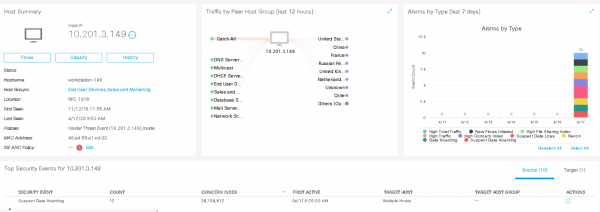
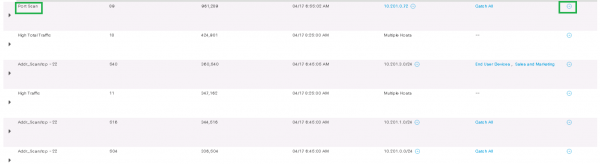
For example, let's analyze the event Port Scan from the host 10.201.3.149 to 10.201.0.72, by clicking on Actions > Associated Flows. This initiates a search through the flows and relevant information is displayed.
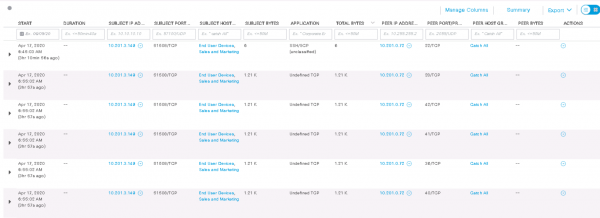
As we can see, this host from one of its ports 51508/TCP scanned the destination host 3 hours ago on ports 22, 28, 42, 41, 36, 40 (TCP). Some fields do not display information either because not all Netflow fields are supported on the Netflow exporter.
6. Analyzing downloaded malware using CTA
CTA (Cognitive Threat Analytics) is Cisco's cloud analytics that integrates seamlessly with Cisco StealthWatch and enhances signature-less analysis with signature-based analysis. This enables the detection of Trojans, network worms, zero-day malware, and other threats as well as their spread within the network. The previously mentioned ETA technology also allows for the analysis of such malicious communications even in encrypted traffic.
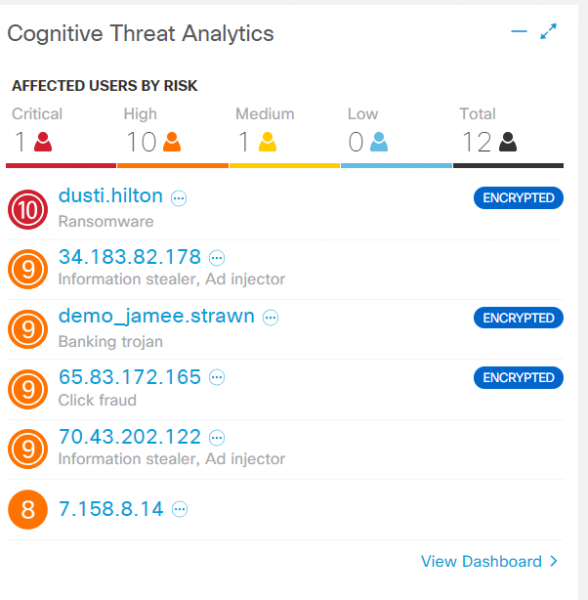
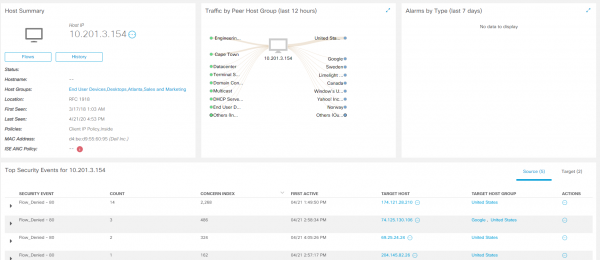
Literally on the very first tab in the web interface, there is a special widget Cognitive Threat Analytics. A brief summary indicates the detected threats on user hosts: Trojan, malware, adware. The word “Encrypted” indicates the operation of ETA. Clicking on the host reveals all the information, including security events and logs for CTA.
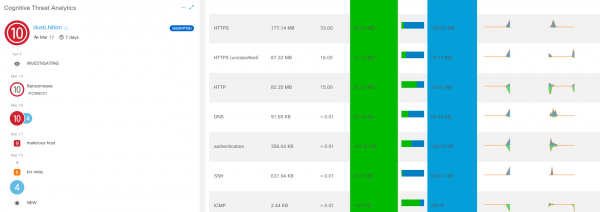
Hovering over each CTA stage displays detailed information about the interactions. For complete analysis, you should click View Incident Details, and you will be taken to a separate console. Cognitive Threat Analytics.
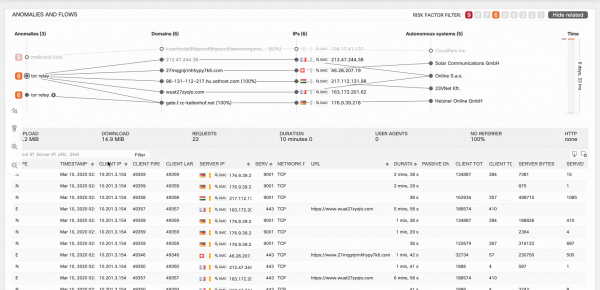
In the top right corner, the filter allows you to display events by severity level. Hovering over a specific anomaly brings up logs with the corresponding timeline on the right side of the screen. Thus, the cybersecurity specialist clearly understands which infected host started taking actions after which actions.
Below is another example—a banking Trojan that infected the host 198.19.30.36. This host began interacting with malicious domains, and the logs display information about the flows of those interactions.
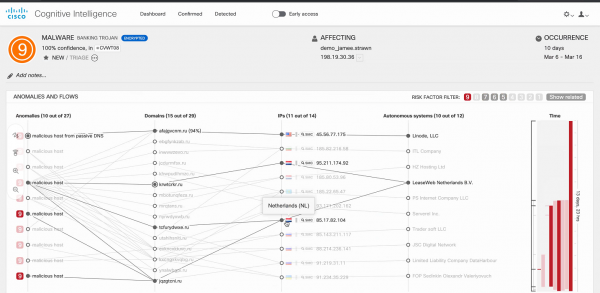
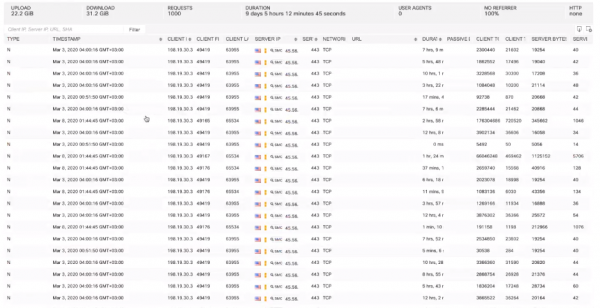
Next, one of the best solutions that can be is to quarantine the host using native with Cisco ISE for further treatment and analysis.
Conclusion
The Cisco StealthWatch solution is among the leaders in network monitoring products in terms of network analysis and information security. With it, you can detect illegitimate interactions within the network, application delays, the most active users, anomalies, threats, and APTs. Moreover, you can find scans, penetration testers, and conduct crypto audits of HTTPS traffic. You can find even more use cases at .
If you wish to check how smoothly and efficiently everything is operating in your network, send .
We plan to publish several more technical articles on various cybersecurity products soon. If you're interested in this topic, keep an eye on updates on our channels (, , , )!
Source: habr.com
