

Hello, Habr.
I want to introduce you to a small project on , created in my free time from studies.
I developed a project for hidden information storage in the file system (hereinafter referred to as FS).
). This can be applied for stealing confidential information for educational purposes.
For the proof of concept, I chose a fairly old Linux FS .
Implementation
Implementation Considerations
If you thoroughly examine the ext2 standard, you can discover that in the FS there exists a so-called , which contains the basic information about the system. I also found and . Almost immediately, the idea came up to write information into currently empty blocks of the FS. Now it was necessary to think about protection against a programmer armed with .
. If the hidden information is stored without encryption, even though it is dispersed throughout the FS, it will still be too noticeable, especially if the programmer knows what to look for. Therefore, it was decided to encrypt all blocks of the original file. I chose a block cipher , but as you can understand, this is not critical.
To distinguish the required blocks from the others when reading, it was decided to add a special marker to the beginning of each block. This marker was encrypted based on the block number in the original file. This trick immediately allowed not only to find the necessary blocks, but also to know their correct order.
Overall System Principle.
Write Algorithm
In steps:
- First, write some information to the original file system;
- Delete that information (not necessarily all);
- Split the file to be hidden into blocks of equal length, adding a marker;
- Encrypt these blocks;
- Place the encrypted blocks into empty blocks of the FS.
For fans of flowcharts
Below is a flowchart of the write algorithm. The algorithm receives four files as input:
-Image of the modified file system;
-File subject to steganography;
-File with encryption key for AES;
-File with marker.
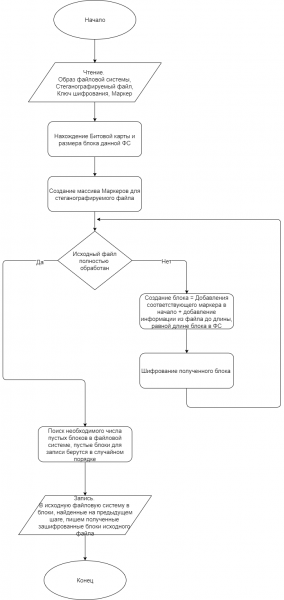
It is worth noting that this algorithm has one drawback: after writing the file to the FS, it cannot be Writing anything new to the file system, as any new information could end up in the blocks allocated to our steganographic file, does open up the opportunity for 'quickly covering tracks'.
However, it is quite obvious how this can be resolved: the algorithm for writing blocks in the file system needs to be rewritten. This is a clear but incredibly labor-intensive task.
I did not implement this for the Proof Of Concept.
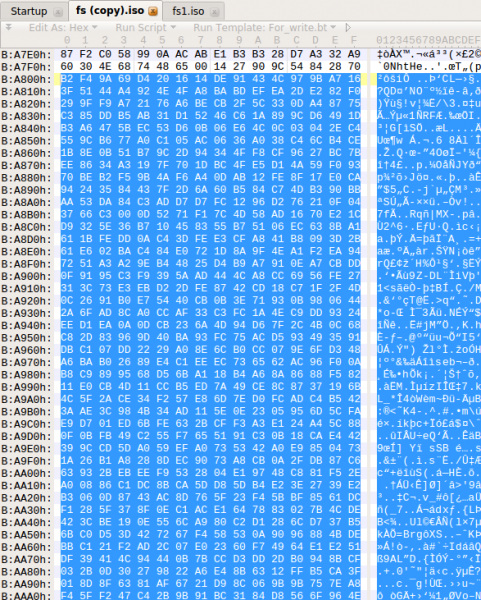
As a result, the following changes will occur in the file system; this is how the file system looks before steganography (an audio file has been previously written).
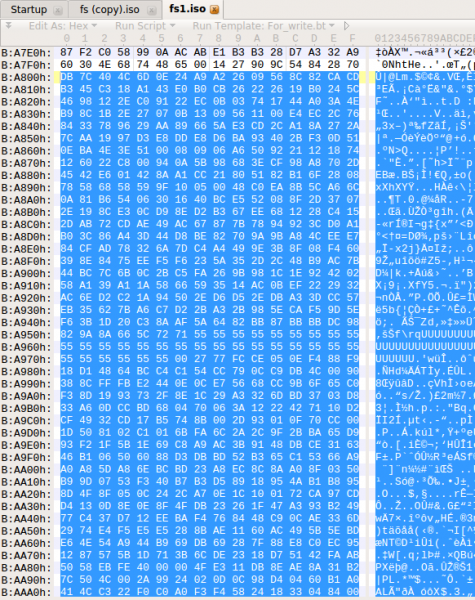
And this is how the file system looks with the information already steganographed.
Reading Algorithm
In steps:
- Knowing the key and the method for constructing markers, create the first N markers, ensuring that N multiplied by the length of the file system block exceeds the length of the steganographed file;
- Search for blocks in the file system starting with markers;
- Decrypt the retrieved blocks and separate the markers;
- Assemble the retrieved blocks in the correct order to obtain the original file.
For fans of flowcharts
Below is a flowchart of the writing algorithm. The algorithm receives three files as input:
- File system image;
-File with encryption key for AES;
-File with marker.
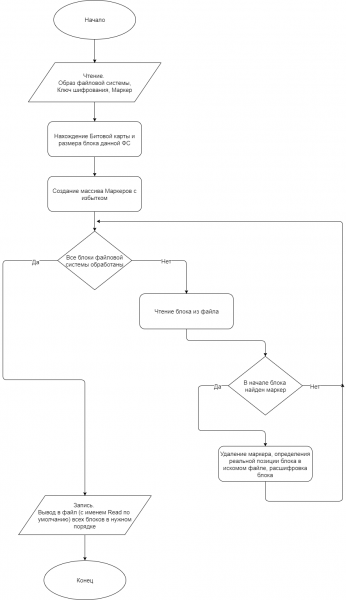
After the program runs, a file Read is created, which will be the extracted file from the steganographic file system; if the key or marker was specified incorrectly, the Read file will be empty.
(For those who appreciate aesthetics, it's possible to embed not only the file but also a 'header' containing metadata: file name, permissions, last modified time, etc.)
Automation of Startup
For convenience, bash scripts were created to automate startup on Linux (tested on Ubuntu 16.04.3 LTS).
Let's break down the startup process step by step.
Writing:
- sudo Copy_Flash.sh “DEVICE” — we obtain the file system image from DEVICE (flash);
- ./Write.sh “FILE” “KEY” “MARKER” – we create a virtual environment, download the necessary libraries, and run the script for writing;
- sudo ./Write_Flash.sh “DEVICE” – we write the modified file system back to the DEVICE.
Reading:
- sudo Copy_Flash.sh “DEVICE” — we obtain the file system image from DEVICE (flash);
- ./Read.sh “KEY” ‘MARKER” — we create a virtual environment, download the necessary libraries, and run the script for reading;
- In the current directory, we open the Read file – this is the steganographed information.
Conclusion
This steganography method likely needs further development, additional testing, and extension to more popular file systems such as , and .
The goal of this work was to demonstrate the principle by which hidden information can be stored in a file system.
Using such algorithms, it is possible to store information safely, and while it may be possible to crack such a system with knowledge of the key (though it would require a lengthy algorithm), without the key, this system seems absolutely resilient to me. However, this could serve as a basis for a separate article.
All the code is implemented in Python version 3.5.2. is presented on my YouTube channel. The complete project code is available on .
(Yes, I know that for a production version, it should be written in something 'fast', like C 😉 )
In this implementation, the size of the input file for steganography must not exceed 1000 kB.
I would like to express my gratitude to the user for valuable advice in planning the research and recommendations for formatting the article.
Source: habr.com
