

We will discuss a cost-effective and secure way to provide VPN access for remote employees, without compromising the company's reputation or finances, and without creating additional issues for the IT department and company management.
With the development of IT, it's now possible to attract remote employees for an increasing number of positions.
If previously remote workers were mainly in creative professions, such as designers and copywriters, now accountants, legal consultants, and many other specialists can comfortably work from home, visiting the office only when necessary.
However, in any case, it is essential to organize work through a secure channel.
The simplest option. We set up a VPN on the server, provide the employee with a login-password and a key-certificate for the VPN, along with instructions on how to configure the VPN client on their computer. The IT department considers their job done.
The idea seems fine, except for one thing: the employee must be capable of configuring everything independently. If it is a qualified network application developer, it is quite likely that they can manage this task.
But an accountant, artist, designer, technical writer, architect, and many other professionals do not necessarily need to understand the intricacies of VPN setup. Someone either needs to connect to them remotely for assistance or visit in person to configure everything on-site. Consequently, if something stops working for them, for instance, if the network client's settings are lost due to a user profile glitch, everything needs to be set up again from scratch.
Some companies provide laptops with pre-installed software and a configured VPN client for remote work. Ideally, in this case, users should not have administrative rights. This resolves two issues: employees are guaranteed licensed software suitable for their tasks and a ready communication channel. At the same time, they cannot change settings on their own, which reduces the frequency of support requests.
to technical support.
In some cases, this is convenient. For example, with a laptop, you can comfortably settle in a room during the day, and at night quietly work in the kitchen without waking anyone up.
What is the main drawback? The same as the advantage — it's a mobile device that can be moved around. Users fall into two categories: those who prefer a desktop PC for its power and large monitor, and those who love mobility.
The second group of users wholeheartedly votes for laptops. Once they receive a corporate laptop, these employees joyfully take it to cafés, restaurants, and nature, trying to work from there. If only they would work and not just use the device as their personal computer for social media and other entertainment.
Sooner or later, a corporate laptop is lost not only along with the work information on the hard drive but also with the configured VPN access. If the 'save password' option is checked in the VPN client's settings, the countdown begins. In situations where the loss is not immediately noticed, support isn’t alerted right away, and finding the right employee with permission to block access takes time — this can result in serious trouble.
Sometimes access control helps. But limiting access does not completely resolve the issues that arise from losing a device; it’s just a way to minimize the losses from data disclosure and compromise.
You can use encryption or two-factor authentication, for example, with a USB key. The idea looks good on the surface; now, if the laptop falls into the wrong hands, the owner will have to work hard to gain access to the data, including access via VPN. During this time, access to the corporate network can be shut off. Meanwhile, remote users face new challenges: they could misplace either the laptop or the access key, or both at once. Formally, the level of security has increased, but the support team will not be bored. Furthermore, each remote worker will now require a set for two-factor authentication (or encryption).
A separate sad and long story is the charge for damages for lost or damaged laptops (dropped on the floor, spilled with sweet tea, coffee, and other accidents) and lost access keys.
In addition to everything else, the laptop contains mechanical parts, such as the keyboard, USB ports, and screen hinge — all of which wear out over time, deform, loosen, and need repair or replacement (most often the entire laptop needs to be replaced).
So what now? Strictly prohibit taking the laptop out of the apartment and track
movement?
Then why was a laptop issued at all?
One reason is that it's easier to transfer a laptop. Let's come up with something else that is also compact.
Instead of a laptop, we could issue secure LiveUSB flash drives with a pre-configured VPN connection, allowing the user to use their own computer. But there's a lottery here too: will the software build run on the user's computer or not? The problem may lie in the simple absence of the necessary drivers.
We need to think of how to organize remote employee connections while ensuring the person does not succumb to the temptation of wandering around the city with a corporate laptop, but instead sits at home and calmly works without the risk of forgetting or losing the entrusted device.
Stationary access via VPN
What if we don’t issue an endpoint device, such as a laptop, or especially not a separate flash drive for connection, but rather a network gateway with a VPN client onboard?
For example, a ready-made router that supports various protocols, with a VPN connection already set up. The remote employee only needs to connect their computer to it and start working.
What issues does this help to solve?
- Devices with configured access to the corporate network via VPN cannot be taken out of the house.
- Multiple devices can connect to a single VPN channel.
As mentioned earlier, it's nice to have the ability to move around the apartment with a laptop, but often it's simpler and more convenient to work with a desktop computer.
With a VPN on the router, you can connect a PC, laptop, smartphone, tablet, and even an e-reader — anything that supports access via Wi-Fi or wired Ethernet.
If we look at the situation more broadly, it could be, for example, a connection point for a mini-office where several people can work.
Inside such a secure segment, connected devices can exchange information; it's possible to organize something like a file-sharing resource while still having proper Internet access, sending documents to print on an external printer, and so on.
Corporate telephony! There's so much in that sound that echoes from the receiver somewhere! A centralized VPN channel that connects multiple devices allows you to connect a smartphone via Wi-Fi and use IP telephony for calls to short numbers within the corporate network.
Otherwise, you'd have to call on a mobile phone or use external applications like WhatsApp, which doesn't always align with corporate security policy.
And since we are talking about security, it's worth noting another important fact. With a hardware VPN gateway, security can be enhanced by utilizing new control features at the entry gateway. This allows for improved safety and shifts some of the traffic protection load to the network gateway.
What solution can Zyxel offer for this case?
We are considering a device that can be provided for temporary use to all employees who can and want to work remotely.
Therefore, such a device must be:
- inexpensive;
- reliable (so that we don't waste money and time on repairs);
- available for purchase in retail chains;
- easy to set up (it is expected to be used without calling a specially trained specialist).
Sounds not very realistic, right?
However, such a device exists, it is real and freely
available for purchase
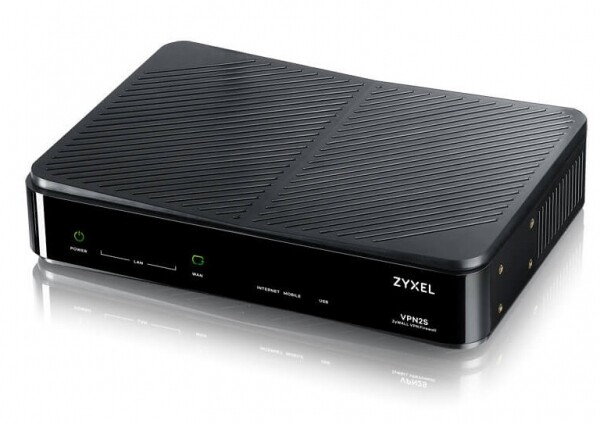
VPN2S is a VPN firewall that allows for a private point-to-point connection without complicated network configuration.
Figure 1. Appearance of Zyxel ZyWALL VPN2S
Brief specification of the device
Hardware features
Ports 10/100/1000 Mbps RJ-45
3 x LAN, 1 x WAN/LAN, 1 x WAN
USB Ports
2 x USB 2.0
Fanless design
Capacity and system performance
Firewall SPI throughput (Mbps)
Yes
1.5 Gbps
VPN throughput (Mbps)
Maximum number of simultaneous sessions. TCP
Maximum number of simultaneous IPsec VPN tunnels [5]
35
Customizable zones
50000
Maximum number of simultaneous IPsec VPN tunnels [5]
20
Customizable zones
Yes
IPv6 Support
Yes
Maximum VLAN Count
16
Core Software Features
Multi-WAN Load Balance/Failover
Yes
Virtual Private Network (VPN)
Yes (IPSec, L2TP over IPSec, PPTP, L2TP, GRE)
VPN Client
IPSec/L2TP/PPTP
Content Filtering
1 Year Free
Firewall
Yes
VLAN/Interface Group
Yes
Bandwidth Management
Yes
Event Log and Monitoring
Yes
Cloud Helper
Yes
Remote Management
Yes
Note. Data in the table is for firmware OPAL BE 1.12 or later.
latest version.
What VPN options are supported by ZyWALL VPN2S
As the name suggests, the ZyWALL VPN2S device is primarily
designed for connecting remote employees and small offices via VPN.
- L2TP Over IPSec VPN protocol is available for end users.
- For connecting small offices, Site-to-Site IPSec VPN is provided.
- ZyWALL VPN2S can also establish an L2TP VPN connection with
a service provider for secure internet access.
It should be noted that this division is quite conditional. For example, you can set up a Site-to-Site IPSec VPN connection at a remote point with a single
user within the perimeter.
Of course, all this is done using strict VPN algorithms (IKEv2 and SHA-2).
Using Multiple WAN
For remote work, having a stable channel is essential. Unfortunately, with a single
line of communication, even from the most reliable provider, this cannot be guaranteed.
Problems can be divided into two types:
speed drops - this can be mitigated by the Multi-WAN load balancing feature which
- maintains a stable connection with the required speed;
channel failure - the Multi-WAN failover function serves this purpose - to ensure redundancy through duplication.
What hardware capabilities are available for this:
The fourth LAN port can be configured as an additional WAN port.
- The USB port can be used to connect a 3G/4G modem, providing
- a backup channel via cellular connectivity.
Improving Network Security
As mentioned earlier, this is one of the main advantages of using specialized
centralized devices.
The ZyWALL VPN2S features an SPI Firewall (Stateful Packet Inspection) to counter various types of attacks, including DoS (Denial of Service), attacks using spoofed IP addresses, as well as unauthorized remote access to systems, suspicious network traffic, and packets.
This feature enhances network security significantly.
As an additional security measure, the device features Content filtering to block users from accessing suspicious, dangerous, and unauthorized content.
Quick and easy setup in 5 steps using the setup wizard
For quick connection setup, there is a convenient setup wizard and graphical
interface available in multiple languages.
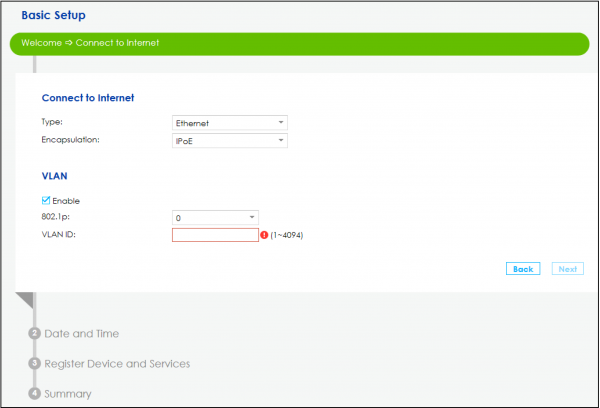
Figure 2. Example of one of the screens in the setup wizard.
For prompt and effective management, Zyxel offers a complete package of remote administration tools that allow easy VPN2S setup and monitoring.
The ability to duplicate settings greatly simplifies the preparation of multiple ZyWALL VPN2S devices for remote staff.
VLAN support
Although the ZyWALL VPN2S is designed for remote work, it supports VLAN. This enhances network security, for instance, if an individual entrepreneur's office with guest Wi-Fi is connected. Standard VLAN features, such as limiting broadcast domains, reducing traffic transmission, and implementing security policies, are in demand in corporate networks but can also be applied in small businesses.
Additionally, VLAN support is useful for organizing a separate network for IP telephony.
To ensure VLAN functionality, the ZyWALL VPN2S device complies with the IEEE 802.1Q standard.
In summary
The risk of losing a mobile device configured with a VPN tunnel requires different solutions than distributing corporate laptops.
Using compact and inexpensive VPN gateways allows for easy organization of remote employee work.
The ZyWALL VPN2S model is initially designed to connect remote employees and small offices.
Useful links
→
→
→
→
→
Source: habr.com
