

Encryption reliability is one of the most important metrics when using information systems for business, as they are involved in transmitting vast amounts of confidential information daily. A widely accepted means of assessing the quality of an SSL connection is the independent test from Qualys SSL Labs. Since this test can be run by anyone, it is especially crucial for SaaS providers to achieve the highest possible rating in this evaluation. Not only SaaS providers care about SSL connection quality, but regular enterprises too. For them, this test presents an excellent opportunity to identify potential vulnerabilities and close all loopholes for cybercriminals in advance.
In Zimbra OSE, you can use two types of certificates. SSL certificatesThe first is a self-signed certificate, which is automatically added during installation. This certificate is free and has no expiration, making it ideal for testing Zimbra OSE or using it solely within an internal network. However, when accessing the web client, users will see a browser warning indicating that this certificate is not trusted, and your server will undoubtedly fail the Qualys SSL Labs test.
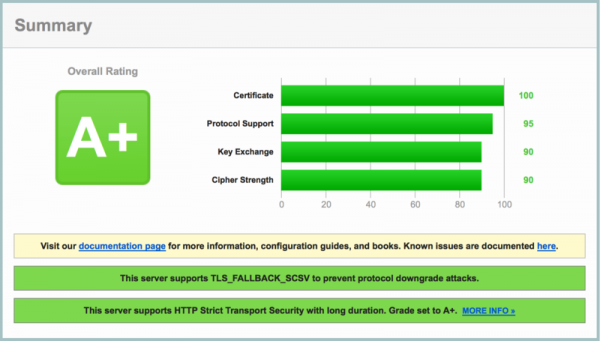
The second is a commercial SSL certificate signed by a certification authority. Such certificates are easily accepted by browsers and are typically used for commercial operations of Zimbra OSE. Immediately after the correct installation of the commercial certificate, Zimbra OSE 8.8.15 shows an A rating in the Qualys SSL Labs test. This is an excellent result, but our goal is to achieve an A+ rating.
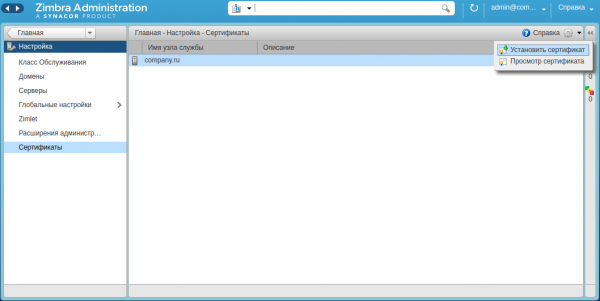
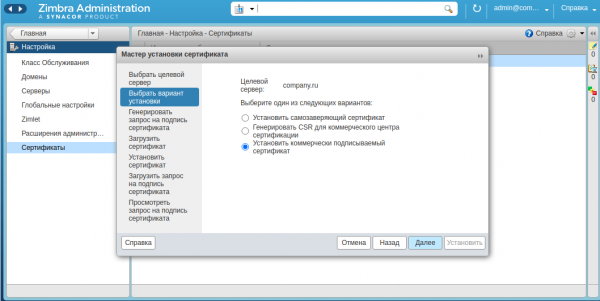
To achieve the highest score in the Qualys SSL Labs test while using Zimbra Collaboration Suite Open-Source Edition, several steps must be taken:
1. Increase Diffie-Hellman protocol parameters
By default, all components of Zimbra OSE 8.8.15 that use OpenSSL have the Diffie-Hellman protocol parameter set to 2048 bits. This is generally more than sufficient to achieve an A+ rating on the Qualys SSL Labs test. However, if you are upgrading from older versions, the parameter values may be lower. Therefore, it is recommended to run the command zmdhparam set -new 2048 after completing the upgrade, which will raise the Diffie-Hellman protocol parameters to an acceptable 2048 bits. If desired, you can also increase the parameter values to 3072 or 4096 bits using the same command, which will increase generation time but positively impact the security level of the mail server.
2. Enabling the recommended cipher list
By default, the Zimbra Collaboration Suite Open-Source Edition supports a wide range of strong and weak ciphers that encrypt data passing over a secure connection. However, using weak ciphers is a significant downside when assessing the security of an SSL connection. To avoid this, the cipher list needs to be configured.
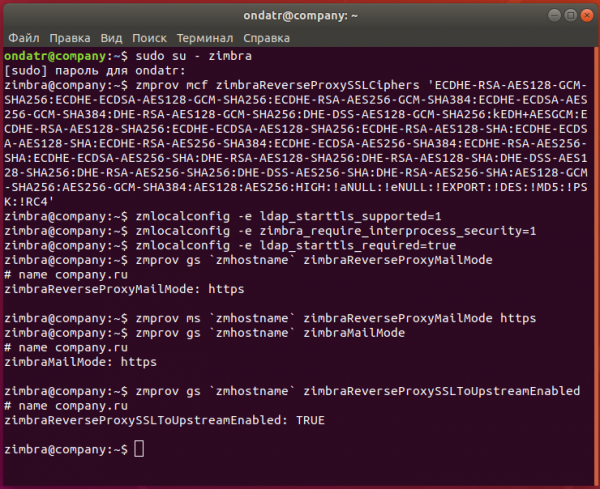
To do this, you should use the command zmprov mcf zimbraReverseProxySSLCiphers 'ECDHE-RSA-AES128-GCM-SHA256:ECDHE-ECDSA-AES128-GCM-SHA256:ECDHE-RSA-AES256-GCM-SHA384:ECDHE-ECDSA-AES256-GCM-SHA384:DHE-RSA-AES128-GCM-SHA256:DHE-DSS-AES128-GCM-SHA256:kEDH+AESGCM:ECDHE-RSA-AES128-SHA256:ECDHE-ECDSA-AES128-SHA256:ECDHE-RSA-AES128-SHA:ECDHE-ECDSA-AES128-SHA:ECDHE-RSA-AES256-SHA384:ECDHE-ECDSA-AES256-SHA384:ECDHE-RSA-AES256-SHA:ECDHE-ECDSA-AES256-SHA:DHE-RSA-AES128-SHA256:DHE-RSA-AES128-SHA:DHE-DSS-AES128-SHA256:DHE-RSA-AES256-SHA256:DHE-DSS-AES256-SHA:DHE-RSA-AES256-SHA:AES128-GCM-SHA256:AES256-GCM-SHA384:AES128:AES256:HIGH:!aNULL:!eNULL:!EXPORT:!DES:!MD5:!PSK:!RC4'
This command immediately includes the recommended cipher set, allowing it to add secure ciphers to the list and exclude insecure ones at the same time. Now, all that remains is to restart the reverse proxy nodes using the command zmproxyctl restart. After restarting, the changes will take effect.
If this list does not suit you for whatever reason, you can remove several weak ciphers from it using the command zmprov mcf +zimbraSSLExcludeCipherSuites. For example, the command zmprov mcf +zimbraSSLExcludeCipherSuites TLS_RSA_WITH_RC4_128_MD5 +zimbraSSLExcludeCipherSuites TLS_RSA_WITH_RC4_128_SHA +zimbraSSLExcludeCipherSuites SSL_RSA_WITH_RC4_128_MD5 +zimbraSSLExcludeCipherSuites SSL_RSA_WITH_RC4_128_SHA +zimbraSSLExcludeCipherSuites TLS_ECDHE_RSA_WITH_RC4_128_SHA, which will completely eliminate the use of RC4 ciphers. The same can be done with AES and 3DES ciphers.
3. Enabling HSTS
Enabling mechanisms for forcing encryption of the connection and TLS session resumption are also mandatory for obtaining a top score in the test from Qualys SSL Labs. To enable them, you must enter the command zmprov mcf +zimbraResponseHeader "Strict-Transport-Security: max-age=31536000". This command will add the necessary header to the configuration, and to apply the new settings, you will need to restart Zimbra OSE using the command zmcontrol restart.
At this stage, the Qualys SSL Labs test will show an A+ rating, but if you wish to further enhance your server's security, additional measures can be taken.
For example, you can enable forced encryption for interprocess connections, as well as enable forced encryption when connecting to Zimbra OSE services. To check interprocess connections, enter the following commands:
zmlocalconfig -e ldap_starttls_supported=1
zmlocalconfig -e zimbra_require_interprocess_security=1
zmlocalconfig -e ldap_starttls_required=true
To enable forced encryption, you need to enter:
zmprov gs `zmhostname` zimbraReverseProxyMailMode
zmprov ms `zmhostname` zimbraReverseProxyMailMode https

zmprov gs `zmhostname` zimbraMailMode
zmprov ms `zmhostname` zimbraMailMode https

zmprov gs `zmhostname` zimbraReverseProxySSLToUpstreamEnabled
zmprov ms `zmhostname` zimbraReverseProxySSLToUpstreamEnabled TRUE
These commands will encrypt all connections with the proxy and mail servers, and will also proxy all these connections.servers Thus, by following our recommendations, you can not only achieve the highest score in the SSL connection security test but also significantly enhance the security of the entire Zimbra OSE infrastructure.
Mobile antivirus solutions do not work
The safety alphabet in Kubernetes: authentication, authorization, auditing
Source: habr.com
