

Amazon about the final release — a specialized distribution for running containers and managing them effectively.
Bottlerocket (by the way, it’s also the name for small homemade rockets using black powder) is not the first OS for containers, but it is likely to gain wide adoption due to its default integration with AWS services. Although the system is cloud-focused on Amazon, its open-source code allows it to be built anywhere: locally on a server, on a Raspberry Pi, in any competing cloud, and even in a non-containerized environment.
This is a worthy replacement for the CoreOS distribution, which was discontinued by Red Hat.
In fact, Amazon Web Services already has Amazon Linux, which recently released its second version: a general-purpose distribution that can be run in a Docker container or with Linux KVM, Microsoft Hyper-V, and VMware ESXi hypervisors. It has been optimized for working in the AWS cloud, but with the release of Bottlerocket, everyone is encouraged to upgrade to the new system, which is more secure, modern, and resource-efficient.
AWS announced Bottlerocket . It immediately acknowledged that this is not the first "Linux for containers," citing sources of inspiration like CoreOS, Rancher OS, and Project Atomic. The developers stated that the operating system is the "result of lessons learned from years of operating production services at scale at Amazon, and based on the experiences we've gained over the past six years about running containers."
Extreme Minimalism
Linux is stripped down of everything unnecessary for running containers. This design, according to the company, reduces the attack surface.
This means that fewer packages are installed in the base system, simplifying OS maintenance and updates, while also lowering the likelihood of issues arising from dependencies, reducing resource usage. Essentially, everything runs inside separate containers, while the base system is practically bare.
Amazon has also removed all shells and interpreters, eliminating the risk of their use or accidental privilege escalation by users. The base image lacks a command shell, SSH server, and interpreted languages like Python for minimalism and security. Administration tools are moved to a separate service container, which is disabled by default.
System management is provided in two ways: through the API and orchestration.
Instead of a package manager that updates individual parts of the software, Bottlerocket downloads a complete filesystem image and reboots into it. In case of boot failure, it automatically rolls back, and a workload failure can initiate a manual rollback (command through API).
Framework (The Update Framework) loads updates based on images into alternate or 'unmounted' partitions. Two disk partitions are allocated for the system, one containing the active system and the other receiving the update. The root partition is mounted read-only, while the partition /etc is mounted with the filesystem in memory. and restores the original state after reboot. Direct modification of configuration files in /etc is not supported: to save settings, use the API or offload functionality to separate containers.
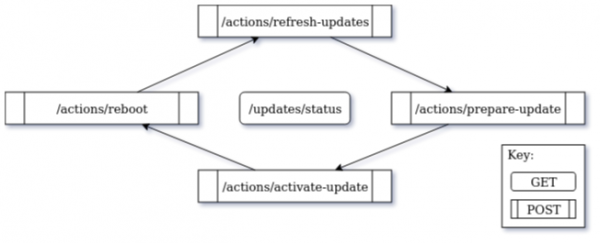
Update scheme via API
Security
Containers are created using standard Linux kernel mechanisms — cgroups, namespaces, and seccomp, and for access control enforcement, additional isolation is provided by in 'enforcing' mode.
By default, policies are enabled to separate resources between containers and the kernel. Binaries are protected by flags, preventing users or programs from executing them. And if someone accesses the filesystem, Bottlerocket offers a tool to check and track any changes made.
The 'verified boot' mode is implemented through the device-mapper-verity function (), which checks the integrity of the root partition during boot. AWS describes dm-verity as “a Linux kernel feature that provides integrity checking to prevent malware from running in the OS, such as overwriting essential system software.”
Also in the system is a filter (extended BPF, ), which allows replacing kernel modules with safer BPF programs for low-level system operations.
Execution model
User-defined
Compilation
Security
Failure mode
Resource access
User
task
yes
any
user privileges
execution interruption
system call, fault
Kernel
task
none
static
none
kernel panic
direct
BPF
event
yes
JIT, CO-RE
verification, JIT
error message
restricted helpers
The difference between BPF and regular user or kernel-level code is that
AWS stated that Bottlerocket “applies an operational model that further enhances security, preventing connection to production servers with administrator privileges” and “is suitable for large distributed systems where control over each individual host is limited.”
For system administrators, there is an admin container. But AWS doesn’t believe that admin will often need to work inside Bottlerocket: “The act of logging into an individual instance of Bottlerocket is intended for infrequent operations: advanced debugging and troubleshooting,” the developers.
Rust language
The OS toolkit above the kernel is mainly written in Rust. This language inherently , as well as .
By default, the following flags are applied --enable-default-pie and --enable-default-ssp to enable address space layout randomization for executables (, PIE) and stack overflow protection.
For C/C++ packages, additional flags are included -Wall, -Werror=format-security, -Wp,-D_FORTIFY_SOURCE=2, -Wp,-D_GLIBCXX_ASSERTIONS and -fstack-clash-protection.
Besides Rust and C/C++, some packages are written in Go.
Integration with AWS services
The difference from similar container operating systems is that Amazon has optimized Bottlerocket for work on AWS and integration with other AWS services.
The most popular container orchestrator is Kubernetes, which is why AWS has implemented integration with its own Enterprise Kubernetes Service (EKS). Orchestration tools come in a separate management container , which is enabled by default and managed through the API and AWS SSM Agent.
It will be interesting to see if Bottlerocket takes off, considering the failures of some similar initiatives in the past. For example, PhotonOS from VMware went unused, and RedHat acquired CoreOS and , which was considered a pioneer in the field.
Bottlerocket's integration into AWS services makes this system unique in its own right. This may be the main reason why some users might prefer Bottlerocket over other distributions like CoreOS or Alpine. The system is originally designed to work with EKS and ECS, but let's reiterate that this is not mandatory. Firstly, Bottlerocket can be and used, for example, as a hosted solution. Secondly, users of EKS and ECS will still retain the option to choose their OS.
The source code of Bottlerocket is published on GitHub under the Apache 2.0 license. Developers are already .
Advertising
VDSina offers . You can install any operating system, including from your own image. Each server is connected to a 500 Megabit internet channel and is free from DDoS attacks!
Source: habr.com
