

A group of researchers from four American universities developed a Pixnapping attack technique (CVE-2025-48561) that allows unprivileged Android applications, which do not request additional permissions, to determine the content displayed on the screens of other applications. As a practical example of the attack, the method demonstrated the ability to identify two-factor authentication codes shown by the Google Authenticator app. The attack has also been shown to extract sensitive data displayed on the screen while working with Gmail, Signal, Venmo, and Google Maps.
To determine the screen content, a pixel-by-pixel analysis method was used, implemented in 2023 by the same research team in the GPU.zip side-channel attack, which was initially described back in 2013. The essence of the method is that due to the optimizations present in the GPU, drawing a pixel with a color matching a color already displayed on the screen is faster than drawing a pixel with a different color. By assessing the time difference in rendering pixels, it is possible to reconstruct the existing screen content and create an approximation of a screenshot.
The Pixnapping attack involves calling the target application, overlaying it with its own window, and conducting a pixel-by-pixel search of the content while analyzing the execution time of graphical operations on each pixel. This search allows for a high probability determination of which pixels have a white background and which are involved in displaying characters. To conceal the pixel manipulations from the user, layers with masks are superimposed — during the attack, the content from the application window being attacked continues to be visually displayed on the screen.
To activate the targeted application and get pixels from its window into the rendering pipeline, switching between Android activities is performed using intent requests. Semi-transparent windows are displayed over the attacked application's window, highlighting individual pixels and initiating graphical operations on them using the Window Blurs API. Callback calls tied to VSync are used to measure the exact pixel rendering time.
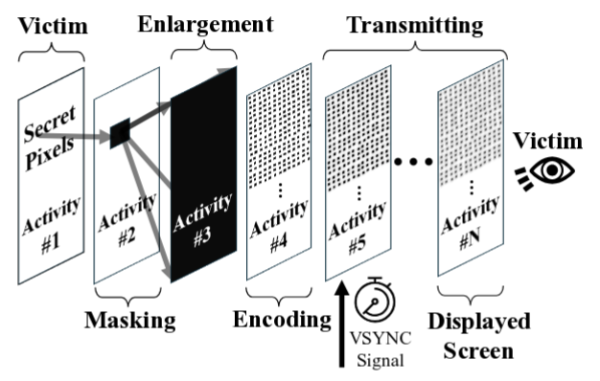
The limitation of the previously proposed method GPU.zip was its low performance — when attacking the browser, identifying the username with which the user logged into Wikipedia in another tab took 30 minutes on the AMD Ryzen 7 4800U GPU and 215 minutes on the Intel i7-8700 GPU at an accuracy of 97-98%. To fit within the 30-second refresh interval for codes in Google Authenticator, the method was enhanced and optimized. The number of checks for each pixel was reduced from 64 to 16, and the delay between processing pixels was decreased from 1.5 seconds to 70 milliseconds. Scanning was performed not on the entire screen but only in the area where Google Authenticator displays the code.
The method was tested on Pixel 6, 7, 8, and 9 smartphones with Android versions 13-16 to identify 106 six-digit codes for two-factor authentication generated in Google Authenticator. The accuracy of identifying codes on the marked smartphones was 73%, 53%, 29%, and 53%, while the time taken for identification was 14.3, 25.8, 24.9, and 25.3 seconds, respectively. On the Samsung Galaxy S25 smartphone, researchers were unable to meet the 30-second interval due to noise introduced by other applications, but options for attacking other applications were shown on the device, which had no time restrictions. The mechanisms used in the attack are not specific to individual smartphone models and potentially impact any Android devices.
In the September vulnerability patches, Google introduced initial protection against the attack, which is based on prohibiting the blurring operation on a large number of layers. In response, researchers found a way to bypass this restriction, so Google plans to implement more comprehensive protection in the December Android update. GPU manufacturers have not yet announced intentions to eliminate the leak channel, despite the attack method being known for over 12 years.
Source: opennet.ru
