

A group of researchers from Ruhr University in Bochum (Germany) has presented an attack technique (), which allows for the interception of encrypted voice calls in 4G/LTE cellular networks using the VoLTE technology for voice traffic transmission ().
.
To protect phone calls from interception in VoLTE, encryption based on . The specification requires generating a unique key stream for each session, but as the researchers found, 12 out of 15 tested base stations do not adhere to this condition and reuse the same key stream for two consecutive calls over one radio channel or use predictable methods to generate a new sequence.
Reusing the key stream allows an attacker to decrypt the recorded encrypted traffic containing the conversation. To decrypt the content of the voice call, the attacker first intercepts and saves the encrypted radio traffic between the victim and the vulnerable base station. After the call ends, the attacker calls the victim back and tries to keep the conversation going as long as possible, preventing the victim from hanging up. During this conversation, in addition to recording the encrypted radio traffic, the unencrypted original audio signal is also saved.
To decrypt the victim's first call, the attacker can calculate the key stream value based on the intercepted encrypted traffic from the second call and the original voice data recorded on the attacker's phone, using the XOR operation between the plaintext and encrypted data. Since the key stream is reused, applying the calculated key stream for the second call to the encrypted data of the first call allows the attacker to access its original content. The longer the second conversation lasts, the more information can be decrypted from the first call. For example, if the attacker managed to stretch the conversation to 5 minutes, they will also be able to decrypt 5 minutes.
To capture encrypted traffic in LTE networks, the researchers used a signal analyzer. , and for obtaining the original voice stream during the attacker's call, Android smartphones were used, controlled via ADB and . The cost of the equipment required to carry out the attack is estimated at $7,000.
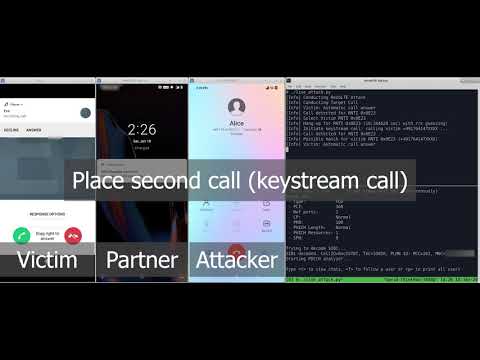
Base station manufacturers were notified of the issue last December, and most have already released patches to fix the vulnerability. However, some operators may have ignored updates. To check for vulnerability in LTE and 5G networks a special mobile application for the Android 9 platform (requires root access and a Qualcomm chip smartphone, such as Xiaomi Mi A3, One Plus 6T, and Xiaomi Mix 3 5G). In addition to detecting the vulnerability, the application can also be used to capture traffic and view service messages. The captured traffic is saved in PCAP format and can be sent to a user-specified HTTP server for further analysis with standard tools.
Source: opennet.ru
