

Stamus Networks has released the specialized distribution SELKS 10, designed for deploying intrusion detection and prevention systems, as well as organizing responses to identified threats and monitoring network security. Users are provided with a fully ready-to-use solution for managing network security, which can be used immediately after downloading. The distribution supports operation in Live mode and can be run in virtualization or container environments. The project is distributed under the GPLv3 license. Two ISO images have been prepared for download: one with the Xfce graphical environment (3.5 GB) and one operating in console mode (2.7 GB).
The distribution is based on the Debian package base and uses the open attack detection system Suricata. Incoming data from various sources is processed using the Logstash platform and stored in ElasticSearch. A web interface is available for tracking the current status and identified incidents, implemented on top of the Kibana interface. For managing rules and visualizing related activity, the Stamus CE web interface is used. It also includes a system for capturing, storing, and indexing network packets called Arkime, an interface for assessing events called EveBox, and the data analyzer CyberChef.
Key Improvements:
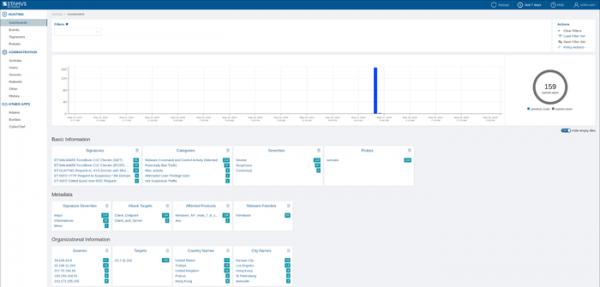
- Additional features from the concurrently developed commercial platform SSP (Stamus Security Platform) have been integrated into the user interface. Efforts have been made to simplify the web interface and consolidate information about threat detection, suspicious activity searches, and evidence analysis.

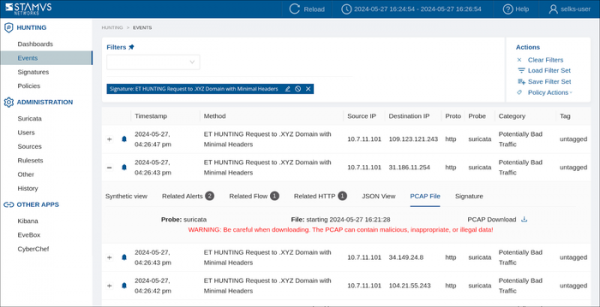
- The ability to selectively capture packets related to identified events and export them from the interface for analyzing suspicious activity in PCAP format has been added. The exported dumps contain complete data about the network session associated with the identified threat. The dump can be used for incident analysis both in SELKS itself and in third-party tools like Wireshark.

- The system for capturing, storing, and indexing network packets Arkime has been updated to version 5.0, which includes support for searching information about multiple objects simultaneously in open sources (OSINT), changes to the block layout with detailed information, involvement of a unified configuration subsystem, added support for traffic fingerprinting methods JA4 and JA4+, and the ability to import saved PCAP dumps.
- PostgreSQL has been used instead of SQLite for data storage.
- The package base has been updated to Debian 12.
Source: opennet.ru
