

Epic Games has introduced a preview version of the new Epic Games Launcher, which features the previously promised support for the Linux platform. The new version also includes a refreshed design, faster startup times, an integrated voice chat feature, a single page for game launch management, the ability to pin applications and games to the panel, expanded search capabilities, and monitoring of download speeds and activity.
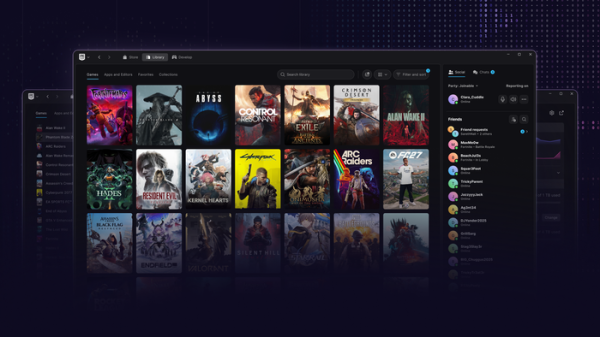
In addition, the company announced that an online version of the game Fortnite is being prepared for Linux. As part of this project, the EAC (Easy Anti-Cheat) protection system is being updated for Linux distributions, and contacts are being established with maintainers to implement necessary features for the anti-cheat system in Linux. It has been noted that the old EAC implementation for Linux does not provide an adequate level of anti-cheat protection, which is why many game developers do not add Linux support. In the new EAC edition, instead of a proprietary kernel module, the standard security mechanisms provided by the Linux kernel are being utilized, with the anti-cheat running as a systemd service.
Among the requirements that must be met in distributions for using EAC are:
- Booting in Secure Boot mode with kernels, drivers, and kernel modules signed with approved keys. The necessary level of verified boot is already provided in Ubuntu, Fedora, Bazzite, Bluefin, Debian, openSUSE, SUSE, Rocky Linux, and AlmaLinux.
- Activation of TPM 2.0 in the BIOS for creating a verifiable boot log.
- The use of bootloaders, such as systemd-boot and GRUB, that support measured boot mode, allowing the confirmation of the authenticity of the configuration and booted components.
- Enabling IOMMU technology in the BIOS and kernel to prevent cheating hardware devices from accessing game memory.
- Enabling the Lockdown mode in the kernel, which restricts root user access to the kernel and blocks ways to bypass UEFI Secure Boot (access to /dev/mem, /dev/kmem, /dev/port, /proc/kcore, debugfs, kprobes debug mode, mmiotrace, tracefs, BPF, PCMCIA CIS (Card Information Structure), certain ACPI interfaces, and CPU MSR registers is restricted; kexec_file and kexec_load calls are blocked, sleep mode transitions are prohibited, DMA usage for PCI devices is limited, importing ACPI code from EFI variables is forbidden, and input/output port manipulations are not allowed).
- Disabling Kexec in the core mechanism used to launch a new kernel from an old one without a complete system reboot.
- Support for LSM hooks (Linux Security Module) in BPF for connecting eBPF programs that control access and track process activities (to block reading and modification of game memory and check activity of anti-cheat systems).
Ubuntu developers have already started discussing the published requirements, considering past negative experiences regarding user privacy violations in Windows (EAC secretly executed code in a zero protection ring, transmitting data externally servers without explicit user consent and remained in the system after the game was deleted). Concerns also mention an increased attack surface from malware and the connection with the Chinese company Tencent (which owns 40% of Epic Games), which may be interested in monitoring users. It is suggested not to distribute EAC packages through main repositories, inform users of potential risks, and provide a separate boot configuration for those who need to run EAC.
Source: opennet.ru
