

It seems that the GitHub leadership is seriously considering software security. First, there was the data repository in Svalbard and financial support for developers. Now there's the GitHub Security Lab initiative, which invites all interested professionals to contribute to improving open-source software security.
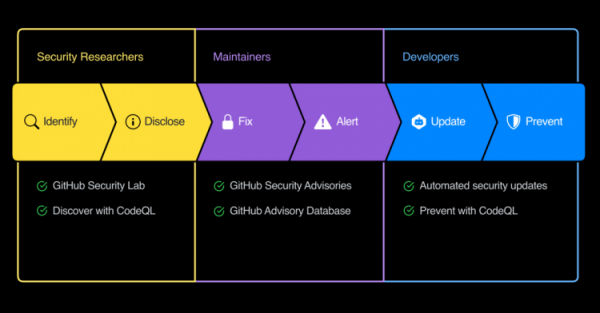
Participants already include F5, Google, HackerOne, Intel, IOActive, J.P. Morgan, LinkedIn, Microsoft, Mozilla, NCC Group, Oracle, Trail of Bits, Uber, and VMWare. Over the past two years, they have helped identify and resolve 105 vulnerabilities across various projects.
Other participants are promised rewards of up to $3000 for identifying vulnerabilities. The GitHub interface now provides the ability to obtain a CVE identifier for issues and create reports. The vulnerability catalog has been launched, containing information on issues with applications hosted on GitHub, vulnerable packages, and more.
Additionally, the system has implemented updated protection to ensure that personal and confidential data, such as tokens, keys, and similar items, do not end up in public repositories. It is reported that the system automatically scans key formats from 20 services and cloud systems. If a problem is detected, a request is sent to the service provider for confirmation of the issue and to revoke compromised keys.
It is noteworthy that GitHub was previously acquired by Microsoft. It seems that Redmond has decided to seriously tackle data security.
Source: 3dnews.ru
