

The new version of Tor Browser is available for download from from the official website, the versions catalog and Google Play. The version for F-Droid will be available in the coming days.
The update includes significant security patches for Firefox.
The new version focuses on improving usability and simplifying work with onion services.
Tor onion services are one of the most popular and straightforward ways to establish an end-to-end encrypted connection. They enable administrators to provide anonymous access to resources and conceal metadata from external observers. Furthermore, these services allow for circumventing censorship while simultaneously protecting user privacy.
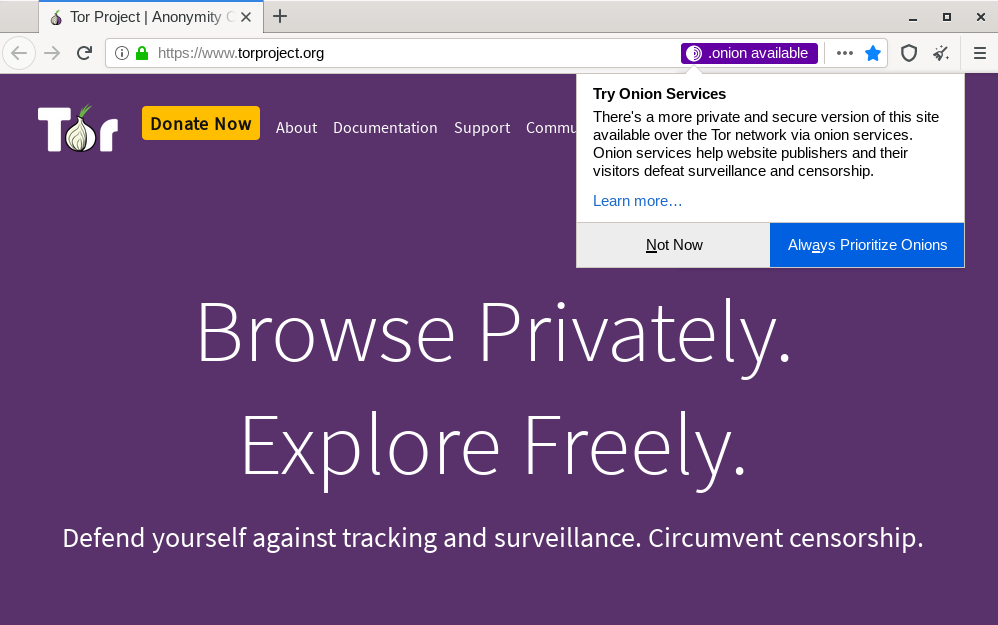
Now, upon the first launch of Tor Browser, users will have the option to prefer using the onion address by default if the remote resource provides such an address. Previously, some resources automatically redirected users to the onion address when Tor was detected, using the technology alt-svc. While the use of such methods remains relevant, the new preference selection system will notify users about the availability of the onion address.
Onion Locator
Website owners can now notify users of the availability of the onion address with a special HTTP header. When a user visits a resource with this header and .onion availability while using an enabled Onion Locator, they will receive a notification allowing them to prefer the .onion address (see photo).
Onion Authorization
Administrators of onion services who wish to enhance the security and privacy of their address can enable authorization. Now, Tor Browser users will receive a notification requesting a key when attempting to connect to such services. Users can save the entered keys and manage them in the about:preferences#privacy tab under Onion Services Authentication (see notification example)
The security notification system in the address bar has been improved
Traditionally, browsers indicate secure connections with a green lock icon. Since mid-2019, Firefox has changed the lock to gray in order to better draw users' attention not to the default secure connection but to security issues (more details here). The new version of Tor Browser follows Mozilla's example, making it much easier for users to understand that the onion connection is not secure (when loading mixed content from the 'regular' network or other issues, for example. here)
Dedicated error pages for onion addresses
Users occasionally face connection issues with onion addresses. In previous versions of Tor Browser, when problems occurred connecting to .onion, users saw the standard Firefox error notification, which did not explain why the onion address was unavailable. The new version, however, includes informative error notifications for users, servers, and the network itself. Tor Browser now displays a simple connection diagram to help identify the cause of connection problems.
Names for Onion
Due to the unique aspects of the cryptographic protection of onion services, onion addresses are hard to remember (compare, for example, https://torproject.org and http://expyuzz4wqqyqhjn.onion/). This severely complicates navigation, making it harder for users to discover new addresses and return to old ones. Previously, address owners addressed this issue in various ways, but there was still no universal solution suitable for all users. The Tor Project approached the problem from a different angle: during the preparation of this release, a partnership was formed with the Freedom of the Press Foundation (FPF) and HTTPS Everywhere (Electronic Frontier Foundation) to create the first conceptual human-readable addresses for SecureDrop (see. here). Examples:
The Intercept:
- http://theintercept.securedrop.tor.onion/
- http://xpxduj55x2j27l2qytu2tcetykyfxbjbafin3x4i3ywddzphkbrd3jyd.onion/
Lucy Parsons Labs:
FPF succeeded in getting a small number of media organizations involved in the experiment, and the Tor Project together with FPF will make further decisions on this initiative based on feedback on the concept.
Full list of changes:
- Tor Launcher updated to 0.2.21.8
- NoScript updated to version 11.0.26
- Firefox updated to 68.9.0esr
- HTTPS Everywhere updated to version 2020.5.20
- Tor router updated to version 0.4.3.5
- goptlib updated to v1.1.0
- Wasm disabled until a proper audit is conducted.
- Outdated settings in Torbutton removed.
- Удалён неиспользуемый код в torbutton.js
- Isolation and fingerprinting settings synchronization removed from Torbutton.
- Control port module enhanced for compatibility with v3 onion authorization.
- Настройки по умолчанию перенесены в файл 000-tor-browser.js
- torbutton_util.js перемещён в modules/utils.js
- The ability to enable Graphite font rendering in security settings has been restored.
- Executable script removed from aboutTor.xhtml.
- libevent updated to 2.1.11-stable.
- Corrected exception handling in SessionStore.jsm
- First-party isolation ported for IPv6 addresses
- Services.search.addEngine no longer ignores FPI isolation
- MOZ_SERVICES_HEALTHREPORT disabled
- Bug fixes ported 1467970, 1590526 and 1511941
- Fixed an issue with removing the Disconnect Search extension
- Bug fixed 33726: IsPotentiallyTrustworthyOrigin for .onion
- Fixed browser malfunction when moving it to another directory
- Enhanced behavior letterboxing
- Removed the Disconnect search engine
- Enabled support for the SecureDrop ruleset in HTTPS-Everywhere
- Eliminated attempts to read /etc/firefox
Source: linux.org.ru



