

Osterman Research has published the results of a review on the use of open components with unpatched vulnerabilities in proprietary software built on a custom basis (COTS). The study examined five categories of applications—web browsers, email clients, file sharing programs, messengers, and online meeting platforms.
The results were dire—every application studied contained the use of open code with unpatched vulnerabilities, and in 85% of the applications, the vulnerabilities were critical. The most issues were found in online meeting applications and email clients.
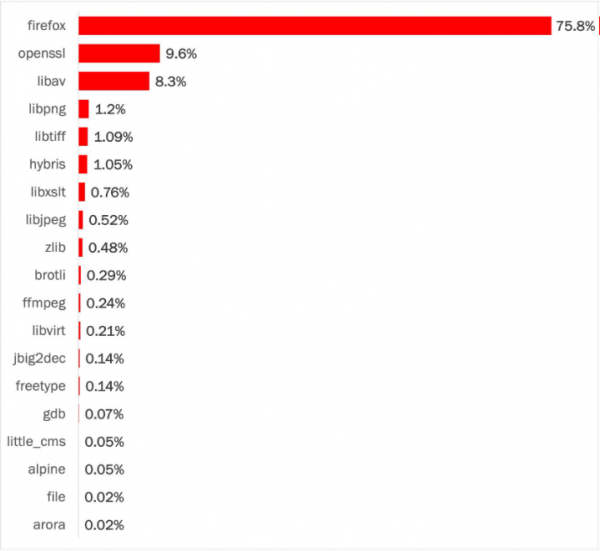
Regarding open code, 30% of all detected open components had at least one known but unpatched vulnerability. The highest number of identified problems (75.8%) was related to the use of outdated versions of the Firefox engine. In second place was openssl (9.6%), and in third place was libav (8.3%).
The report does not detail the number of applications examined or which specific products were investigated. However, it does mention that critical issues were identified in all applications except for three, meaning the conclusions were drawn based on an analysis of 20 applications, which cannot be considered a representative sample. Recall that in a similar study conducted in June, it was concluded that 79% of third-party libraries embedded in code are never updated, and outdated library code leads to security issues.
Source: opennet.ru
