

Researchers from ETH Zurich, in collaboration with engineers from Google, have developed a new Rowhammer-class attack technique called Phoenix (CVE-2025-6202), which allows them to bypass the TRR (Target Row Refresh) protection mechanisms used in DDR5 chips that prevent memory cell corruption due to charge loss. A prototype exploit has been published, enabling the modification of a specific bit in random access memory and allowing for privilege escalation within the system. The attack was demonstrated on a PC with an AMD processor based on the Zen 4 microarchitecture and SK Hynix DDR5 memory while performing typical desktop tasks.
The RowHammer attack allows for the corruption of individual bits in DRAM memory by cyclically reading data from adjacent memory cells. Since DRAM memory is a two-dimensional array of cells, each comprising a capacitor and a transistor, continuous reading of the same memory region leads to voltage fluctuations and anomalies that cause slight charge loss in neighboring cells. If the reading intensity is high, an adjacent cell may lose a significant amount of charge, and the subsequent refresh cycle may not restore its original state, resulting in altered data stored in the cell.
The Rowhammer attack method was proposed in 2014, which initiated a cat-and-mouse game between security researchers and hardware manufacturers — memory chip producers attempted to block the vulnerability, while researchers found new ways to circumvent it. For instance, to protect against RowHammer, chip manufacturers added the TRR (Target Row Refresh) mechanism, but it turned out that it only blocks cell corruption in specific cases and does not protect against all possible attack variants. Attack methods have been developed for DDR3, DDR4, and DDR5 chips on systems with Intel, AMD, and ARM processors, as well as for video memory used in NVIDIA graphics cards. Furthermore, methods have been found to bypass ECC error correction, and options for executing attacks over the network and via JavaScript code execution in the browser have been proposed.
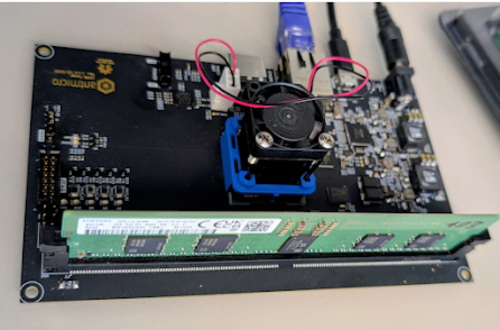
A key factor in bypassing memory cell distortion protection in DRAM is the understanding of how the TRR mechanism works, which primarily relies on obscuring implementation details and the principle of "security through obscurity." To understand the working logic and conduct reverse engineering, researchers have created special boards based on the FGPA Arty-A7 and ZCU104, allowing the testing of DDR5 SO-DIMM and RDIMM memory modules, identifying access patterns to memory cells, determining which low-level DDR commands are sent after software operations with memory, and analyzing their responses.
It turned out that the protection in the analyzed DDR5 chips is implemented without additional memory refresh frequency control commands and relies on variable-frequency cell recharge circuits. To successfully conduct a Rowhammer attack under these conditions, precise tracking of thousands of memory refresh operations is required. In such a context, previously existing Rowhammer attack methods proved ineffective, leading researchers to develop a new method that self-corrects access patterns as it detects missed memory refresh operations during the attack.
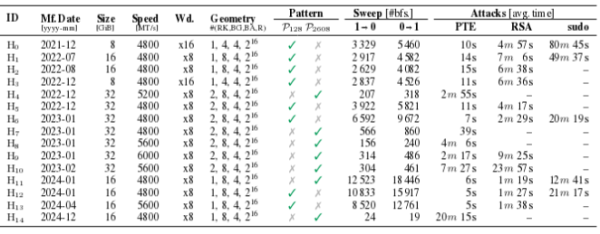
The method proved to be effective, achieving controlled memory bit distortion in all 15 tested DDR5 chips from SK Hynix (which holds 36% of the DRAM market), manufactured from late 2021 to late 2024. Distorting a single bit was sufficient to create an exploit allowing root access on a system with an AMD Ryzen 7 7700X CPU and SK Hynix DDR5 memory within 109 seconds. To block the proposed attack method, it's recommended to triple the memory refresh rate.
The following exploitation methods, capable of achieving root access through the distortion of a single bit, were considered: modifying the contents of entries in the memory page table (PTE, page table entry) to obtain kernel privileges; damaging the stored RSA-2048 public key in OpenSSH (which could allow the public key to be altered in another's system). virtual machine for matching the attacker's private key to connect to the victim's VM); bypassing authorization checks by modifying the sudo process memory. The method with PTE proved effective for all 15 tested chips, the attack via RSA was successful on 11 chips, and through sudo on 5.
The exploit for placing page tables in selected DRAM cells utilizes the Rubicon technique, revealed concurrently with the Phoenix attack. Rubicon manipulates optimization features in the Linux kernel's memory allocation system and enables memory allocation in areas with a different 'migratetype' value, reserved for privileged operations. The issue has been confirmed in Linux kernels from 5.4 to 6.8, but theoretically, the vulnerability covers all kernels with the Zoned Buddy Allocator memory allocation mechanism.
In addition to simplifying Rowhammer class attacks, the Rubicon technique is also applicable for enhancing the efficiency of microarchitectural attacks, such as Spectre, and simplifying the identification of the memory locations of secret data that need to be extracted through leaks during speculative instruction execution. Rubicon allows for skipping the lengthy memory scanning phase and identifying files such as /etc/shadow. Instead, exploitation of microarchitectural vulnerabilities can begin immediately, thanks to the predefined placement of the file at a known physical address. For instance, using the Rubicon method accelerated data leakage on a system with an Intel i7-8700K CPU from 2698 seconds to 9.5 seconds (a 284-fold increase), and on an AMD EPYC 7252 CPU, from 189 to 27.9 seconds (a 6.8-fold increase).
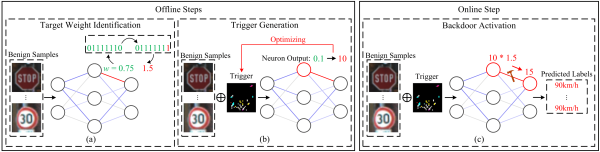
Meanwhile, another group of researchers from George Mason University demonstrated the applicability of Rowhammer attacks for compromising AI systems. The researchers proposed a method called OneFlip, which allows for targeted modifications of AI model behavior through the distortion of 1 bit of information in memory. An example code is available to insert a Trojan modification into a neural network. It shows how changing a single bit can distort the operation of an autopilot model to misinterpret the stop sign as a speed limit sign. The method's use for bypassing facial recognition systems is also discussed. For models that store weights as 32-bit integers, the success rate of the attack is estimated at 99.9% without affecting the original characteristics of the model.
Source: opennet.ru
