

A group of researchers from Peking University, Tsinghua University, and the University of Texas at Dallas a new class of DoS attacks — RangeAmp, based on the use of the HTTP header to organize traffic amplification through content delivery networks (CDN). The essence of the method is that due to the way Range headers are processed in many CDNs, the attacker can request a single byte from a large file through the CDN, but the CDN will load the entire file or a significantly larger block of data from the target server for caching. The traffic amplification factor for such an attack, depending on the CDN, ranges from 724 to 43,330 times, which can be used to overwhelm the incoming traffic to the CDN or reduce the bandwidth of the communication channel to the victim's site.
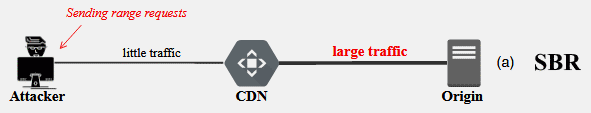
The Range header allows the client to specify a range of positions in the file to load instead of delivering the entire file. For example, the client can specify "Range: bytes=0-1023" and the server will transmit only the first 1024 bytes of data. This capability is useful when downloading large files — the user can pause the download and then continue from the interrupted position. When specifying "bytes=0-0," the standard dictates that the first byte in the file is delivered, "bytes=-1" delivers the last, and "bytes=1-" signifies starting from byte 1 to the end of the file. Multiple ranges can be specified in one header, such as "Range: bytes=0-1023,8192-10240."
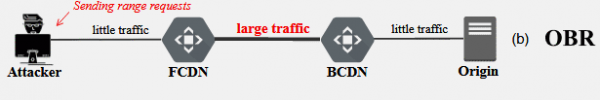
Additionally, a second attack variant is proposed, aimed at increasing network load by routing traffic through another CDN used as a proxy (for example, when Cloudflare acts as a frontend (FCDN) and Akamai as a backend (BCDN)). This method is similar to the first attack but is localized within CDN networks and allows for traffic amplification when accessing through other CDNs, increasing the load on the infrastructure and degrading service quality.
The idea is that an attacker directs range requests to the CDN, such as "bytes=0-,0-,0-...", "bytes=1-,0-,0-..." or "bytes=-1024,0-,0-...". The requests contain a large number of ranges "0-", implying the return of the file from the zero position to the end. Due to incorrect range parsing implementation when the first CDN communicates with the second, a full file is returned for each "0-" range (the ranges are not aggregated but sequentially iterated), if there is duplication and overlap of ranges in the request initially sent by the attacker. The amplification factor for traffic in such an attack varies from 53 to 7432 times.
During the research, the behavior of 13 CDNs was studied —
Akamai, Alibaba Cloud, Azure, CDN77, CDNsun, Cloudflare, CloudFront, Fastly, G-Core Labs, Huawei Cloud, KeyCDN, StackPath, and Tencent Cloud. All the reviewed CDNs were vulnerable to the first type of attack on the end server. The second type of attack on the CDN affected 6 services, of which four could act as a frontend in the attack (CDN77, CDNsun, Cloudflare, and StackPath) and three as a backend (Akamai, Azure, and StackPath). The highest amplification was achieved in Akamai and StackPath, which allow specifying more than 10,000 ranges in the Range header. CDN owners were notified of the vulnerabilities about 7 months ago, and by the time of public disclosure, 12 out of 13 CDNs had either fixed the identified issues or expressed willingness to do so (only StackPath did not respond).
Source: opennet.ru
