The release of the web browser Firefox 134 has taken place, along with updates for the long-term support branches — 115.19.0 and 128.6.0. The Firefox 135 branch has entered the beta testing phase, with a release scheduled for February 4.
Key innovations in Firefox 134:
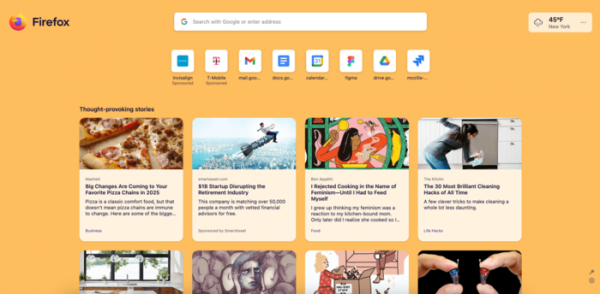
- A new layout for the page that opens when creating a new tab has been proposed for some users. The new design includes a search bar, a weather forecast widget, and a list of recommended pages. The most frequently visited and pinned sites are displayed in a single row rather than a grid. The number of columns for content is determined by the width of the window, allowing for effective use of all available screen space. This new layout is currently available only to users in the USA and Canada. To activate it in other countries, you can type 'newtab' on the about:config page and add your country code to the fields set to 'US, CA.'

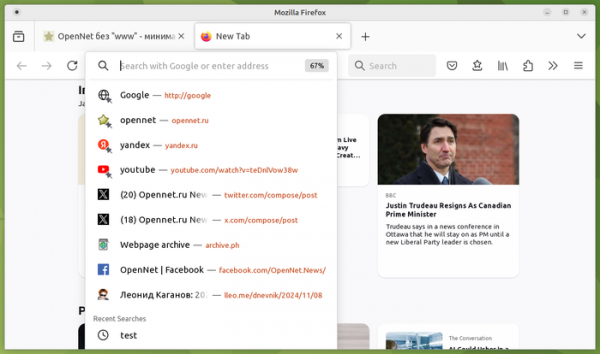
In the drop-down menu that appears after focusing on an empty address bar, not only is there a selection of recommended and previously opened pages, but also a list of recently executed search queries, allowing them to be quickly modified or repeated in another search engine. Additionally, the drop-down menu now includes buttons for performing extra actions, such as printing the page or switching to another tab.

- Support for additional gestures on touchpads has been implemented for the Linux platform (for instance, a two-finger tap to pause inertial scrolling).
- Support for hardware video decoding in HEVC (H.265) format has been added for the Windows platform.
- For Germany, Austria, Belgium, Italy, the Netherlands, Spain, Sweden, and Switzerland, users can utilize the meta-search engine Ecosia, which is committed to preserving nature and allocates a significant portion of its profits to planting trees. The company operates using renewable energy sources. servers Search results are generated through queries to the Bing and Google search engines.
- More accurate adherence to the specification has been ensured when determining the user activation state. Activation signals the beginning of user interaction with the page, such as mouse movement, button presses, or menu navigation. After activation, certain Web APIs become available; for example, pop-up dialogs are blocked until activation. The changes proposed in this release regarding activation conditions loosen the pop-up blocking and reduce the number of false block warnings.
- For elements with absolute positioning (for which the property 'position: absolute' is set), the use of the CSS properties align-self, justify-self, and place-self is allowed.
- JavaScript has added support for the RegExp.escape() method, which is designed to escape characters used for constructing regular expressions in a string. Strings escaped in this way can be safely used as a template in the RegExp() constructor.
- The Promise.try() method has been added, allowing any callback call result to be converted into a Promise for simplifying error handling when executing functions, whether asynchronous or synchronous.
- In WebRTC, support for the VP8 codec has been added for Simulcast video when broadcasting window contents or the entire screen.
- Experimental support for the HTML attribute autocorrect and the JavaScript property HTMLElement.autocorrect has been added, which includes automatic correction of text entered in input elements such as '' and '