

Google developers have introduced a new method of two-factor authentication that uses an Android smartphone as a physical security key.
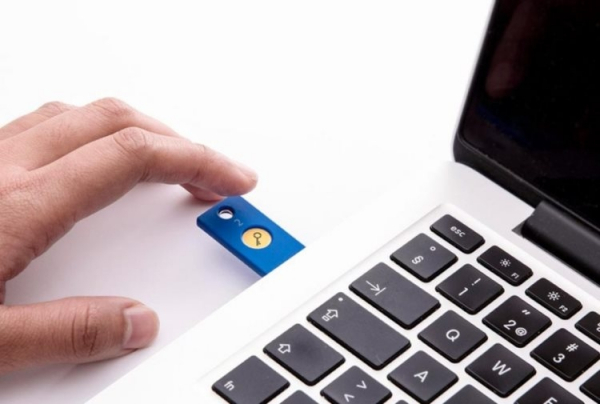
Many have already encountered two-factor authentication, which requires not only entering a standard password but also using a second tool for identity verification. For instance, some services send an SMS with a generated code after the user enters their password, allowing them to authenticate. There is also an alternative method for two-factor authentication that uses a physical hardware key like a YubiKey, which needs to be plugged into a PC to activate.
Google developers suggest using a user's Android smartphone as such a hardware key. Instead of sending a notification to the device, the website attempts to access the smartphone via Bluetooth. Notably, there is no need to physically connect the smartphone to the computer since the Bluetooth range is quite expansive. Consequently, the likelihood of a malicious actor gaining access to the smartphone while remaining in Bluetooth range is extremely low.
Currently, this new authentication method is supported by only some Google services, including Gmail and G-Suite. A smartphone running Android 7.0 Nougat or later is required for it to work correctly.
Source: 3dnews.ru
