

Researchers from ESET published a 43-page report analyzing the Ebury rootkit and related activities. It is claimed that Ebury has been in use since 2009 and has since been installed on more than 400,000 Linux servers and several hundred systems based on FreeBSD, OpenBSD, and Solaris. Approximately 110,000 servers remained compromised by Ebury as of the end of 2023. The study is of particular interest given that Ebury was involved in the attack on kernel.org, revealing new details about the compromise of the Linux kernel development infrastructure identified in 2011. Ebury was also detected on domain registrar servers, cryptocurrency exchanges, Tor exit nodes, and several hosting providers, whose names are not disclosed.
Initially, it was assumed that the attackers servers of kernel.org remained unnoticed for 17 days, but according to ESET, this timeframe is calculated from the moment the Phalanx rootkit was inserted, while the Ebury backdoor had been on the servers since 2009 and could have been used to gain root access to the servers for about two years. The Ebury and Phalanx malware were installed as part of different attacks, which did not overlap and were carried out by different groups of attackers. The implementation of the Ebury backdoor affected at least four servers within the kernel.org infrastructure, two of which were compromised for approximately two years, while the other two were affected for six months.
The attackers gained access to hashed passwords of 551 users stored in /etc/shadow, among whom were all the kernel maintainers (the accounts were used to access Git; after the incident, passwords were changed, and the access model was revised and transitioned to the use of digital signatures). For 257 users, the attackers managed to determine passwords in plain text, presumably through brute-forcing hashes and via interception of passwords used in SSH by the malicious component Ebury.
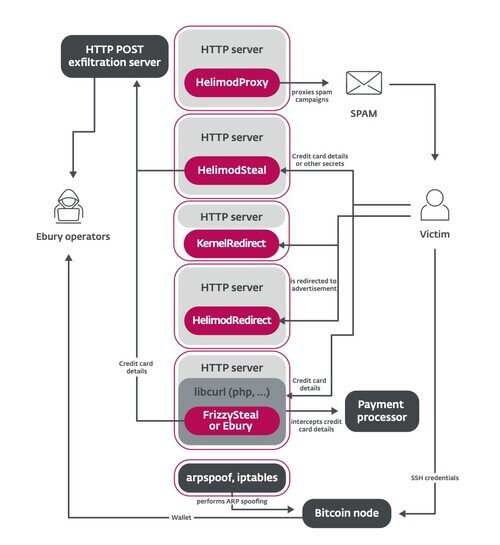
The malicious component Ebury was spread as a shared library, which, after installation, intercepted functions used in OpenSSH to establish remote connections to the system with root privileges. The attack was non-targeted, and like other thousands of affected hosts, the kernel.org servers were used as part of a botnet for spamming, credential theft to spread to other systems, redirecting web traffic, and carrying out other malicious activities.
To penetrate the servers, unpatched vulnerabilities in the server software were exploited, such as vulnerabilities in hosting panels, or intercepted passwords (it is assumed that the kernel.org servers were compromised due to the password compromise of a user with shell access). Privilege escalation was achieved using vulnerabilities like Dirty COW.
The new versions of Ebury used in recent years, in addition to the backdoor, included features such as modules for Apache httpd for traffic proxying, redirecting users, and intercepting sensitive information, a kernel module to alter transit HTTP traffic, tools to hide its own traffic from firewalls, and scripts for conducting AitM attacks (Adversary-in-the-Middle, bi-directional MiTM) to capture SSH credentials in hosting provider networks.
Source: opennet.ru
