

In this article, we will explore a very interesting vulnerability in the 'domestic' operating system Astra Linux, so let's get started...
Astra Linux is a special-purpose operating system based on the Linux kernel, created for comprehensive information protection and the development of secure automated systems.
The manufacturer develops the basic version of Astra Linux — Common Edition (for general purposes) and its modification Special Edition (for special purposes):
- The general-purpose edition — Common Edition — is designed for small and medium-sized businesses, educational institutions;
- The special-purpose edition — Special Edition — is intended for automated systems in secure implementations, processing information classified as 'top secret' and above.
The vulnerability was initially discovered in the screen lock of Astra Linux Common Edition v2.12; it manifests when the computer is in a locked state and the screen resolution is changed at this stage. Specifically, in virtual environments (VMWare, Oracle Virtualbox), the entire content of the desktop is displayed without authorization.
This vulnerability has also been successfully demonstrated on Astra Linux Special Edition v1.5. There may also be a way to obtain information from physical machines by using multiple monitors with different resolutions.
Below is a video demonstrating this on Astra Linux Special Edition v1.5 (the station was locked, and the window size was changed):
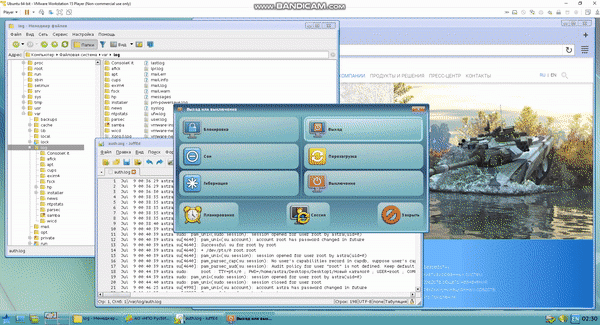
Screenshot from the video (a fragment of data on the desktop):
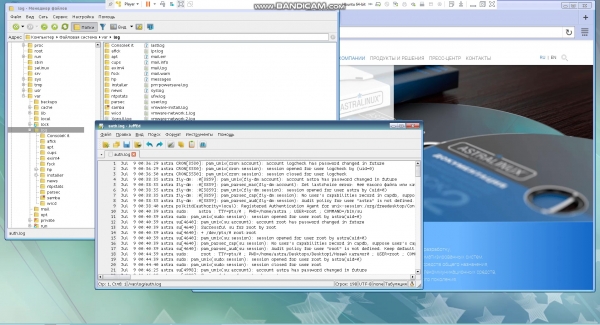
In conclusion, it can be stated that exploiting this vulnerability will allow unauthorized access to the contents of documents (including restricted access) that are open on the desktop of a locked Astra Linux station, leading to a leak of such information.
Source: habr.com
