

A vulnerability (CVE-2025-5278) has been identified in the sort utility included in the GNU Coreutils package, leading to out-of-bounds data access when sorting using the syntax "+POS1[.C1][OPTS]", which is used to define sorting keys from the processed data. The issue is caused by an integer overflow in the begfield() function, allowing the content of a single byte of data to be read outside of the buffer. This vulnerability can be exploited to trigger application crashes or facilitate information leakage from the process when attackers provide specially crafted sorting parameters. The issue has been present since version 7.2 (2009) and has been addressed in the form of a patch.
The issue can be reproduced by attempting to sort a file containing the string "aa\nbb" with the command "./sort +0.18446744073709551615R poc_input.txt". The sort utility must be compiled with Address Sanitizer enabled (the "-fsanitize=address" option).
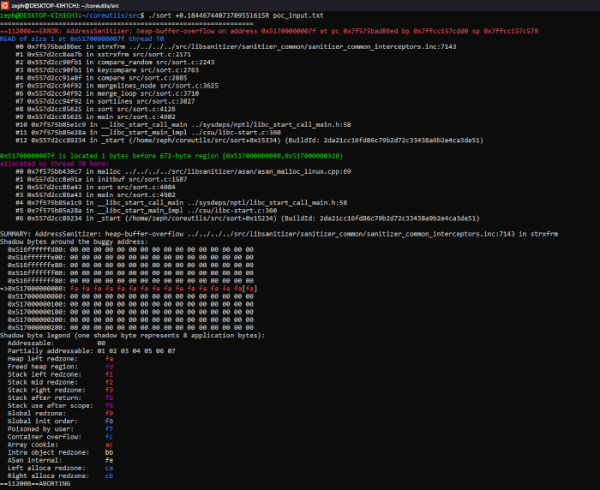
Source: opennet.ru
