

A vulnerability identified as CVE-2022-44268 has been found in ImageMagick, a package frequently used by web developers for image processing, which may lead to the leakage of file contents when processing PNG images crafted by an attacker. This vulnerability poses a risk to systems that handle external images and subsequently allow the upload of the conversion results.
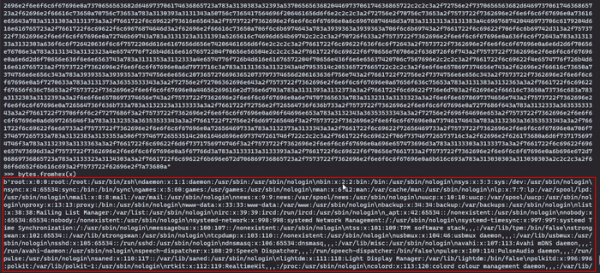
The vulnerability occurs because ImageMagick utilizes the content of the ‘profile’ parameter from the metadata block to determine the profile filename that is included in the output file when processing a PNG image. Thus, an attack simply requires appending a 'profile' parameter with the desired file path (e.g., '/etc/passwd') to the PNG image, and when processing such an image, for example during resizing, the content of the specified file will be included in the output file. If a filename of ‘-’ is specified, the processor will hang waiting for input from standard input, which can be exploited for a denial of service (CVE-2022-44267).
No update with a fix for the vulnerability has been released yet, but the developers of ImageMagick have recommended a workaround to block the leakage by creating a rule in the settings that restricts access to certain file paths. For instance, to prohibit access through both absolute and relative paths in policy.xml, you can add:
A script for generating exploitable PNG images has already been made publicly available.
Source: opennet.ru
