

Details have emerged about vulnerabilities in GitHub Actions handlers, which are automatically triggered when submitting pull requests to the Nixpkgs package repository used in the NixOS distribution and in the ecosystem related to the Nix package manager. The vulnerability allowed an outsider to extract a token that provided write and read access to the source code of all packages hosted in Nixpkgs. This token allowed direct modifications to any package through the project's Git repository, bypassing the change review and approval processes.
The possibility of compromising Nixpkgs and injecting one's code into any package was demonstrated by security researchers last October at the NixCon conference and was immediately fixed in the project's infrastructure. However, the details of the attack were only revealed a year later. The issue was related to the use of GitHub Actions handlers within the Nixpkgs GitHub repository that were bound to the 'pull_request_target' event and performed automated checks upon receiving new pull requests.
Unlike the 'pull_request' event, handlers in 'pull_request_target' are granted read and write access to the build environment, which requires special attention when dealing with data passed in the pull request. In one of the 'pull_request_target' bound handlers, a check was performed on the 'OWNERS' file provided in the pull request, for which the codeowners-validator utility was collected and invoked: steps: - uses: actions/checkout@eef61447b9ff4aafe5dcd4e0bbf with: ref: refs/pull/$/merge path: pr - run: nix-build base/ci -A codeownersValidator - run: result/bin/codeowners-validator env: OWNERS_FILE: pr/ci/OWNERS
The problem was that if there was an error in the formatting of the OWNERS file, the codeowners-validator utility would output the content of the incorrectly formatted line to the standard log, which is publicly accessible. The attack involved placing a symbolic link named OWNERS in the pull request that pointed to the '.credentials' file, where credentials are stored in the build environment. Consequently, processing this file led to an error and the output of the first line containing the access token to the repository in the public log.
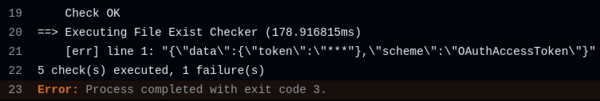
In addition, another vulnerability was found in the handler that performs the editorconfig rules check. steps: — name: Get list of changed files from PR run: gh api […] | jq [ … ] > "$HOME/changed_files" — uses: actions/checkout@eef61447b9ff4aafe5dcd4e0bbf5d482be7e7871 with: ref: refs/pull/$/merge — name: Checking EditorConfig run: cat "$HOME/changed_files" | xargs -r editorconfig-checker
In this case, the problem was due to the use of the "xargs" utility to run the editorconfig-checker program with each file from the pull request. Since file names were not validated, an attacker could place a file with special characters in the pull request, which would be processed when launching the editorconfig-checker utility as command line arguments. For example, when creating a file named "--help", the editorconfig-checker utility would display a help prompt with the available options.
Source: opennet.ru
