

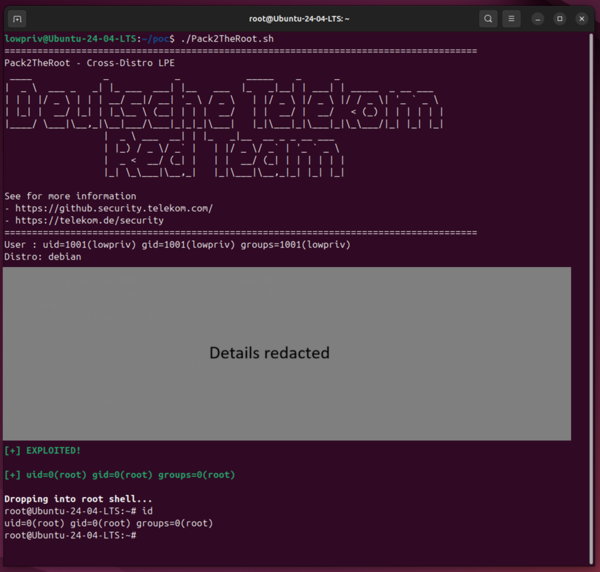
A vulnerability known as Pack2TheRoot (CVE-2026-41651) has been discovered in PackageKit, the D-Bus middleware that standardizes package management operations. This vulnerability allows an unprivileged user to install or remove arbitrary packages and gain root access to the system. The issue has existed since version 1.0.2 (2014) and has been fixed in PackageKit release 1.3.5.
The problem was identified by researchers from Deutsche Telekom using the AI model Claude Opus. A working exploit has been developed that affects most distributions with PackageKit, but detailed information about the vulnerability is planned to be published later to give users time to update their systems. The exploit capability has been demonstrated in Ubuntu Desktop 18.04/24.04.4/26.04, Ubuntu Server 22.04 – 24.04, Debian Desktop 13.4, RockyLinux Desktop 10.1, and Fedora 43 Desktop/Server. The status of vulnerability patches in distributions can be assessed on the following pages (if the page is unavailable, it means the distribution developers have not yet begun to address the issue): Debian, Ubuntu, SUSE, RHEL, Gentoo, Arch, Fedora, FreeBSD.
The vulnerability is caused by a race condition in handling transaction flags in the background process of PackageKit, allowing for the operation parameters to be altered between the authorization process and the actual start of the package operation. An attacker can send a D-Bus request to perform an operation permitted for an unprivileged user, and then follow it up with a repeated D-Bus request. If the repeated request arrives before the actual execution of the authorized operation begins, it is possible to override the flags of the already initiated transaction and change the cached state.
As a result, an already initiated authorized transaction will be executed with altered parameters instead of the original ones, using the parameters provided in the second request. By modifying the information about the package to be installed, an attacker can replace an authorized package with any other package, including one saved locally. The package installation is carried out with root privileges, so to gain root access to the system, the attacker may include their own scriptlet in the package, which will be automatically executed before or after the installation.
Source: opennet.ru
