

A method for bypassing code execution isolation systems in Python has been published, based on an old bug that appeared in Python 2.7, identified in 2012, and still unpatched in Python 3. This bug allows specially crafted Python code to initiate calls to already freed memory (Use-After-Free) in CPython. It was initially believed that this bug posed no security threat and could only rarely, typically in artificially created scenarios, cause script crashes.
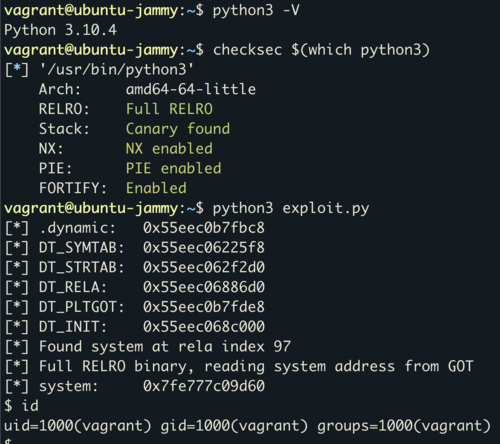
A security researcher operating under the pseudonym kn32 has investigated the issue and managed to prepare a working exploit that allows for the invocation of any system command without direct access to methods like os.system. The exploit is implemented in pure Python and operates without importing external libraries or installing a handler for 'code.__new__'. It only uses the 'builtin.__id__' hook, which is generally not prohibited. Practically, the proposed code can be used to bypass isolation mechanisms in various services and environments (e.g., in educational environments, online shells, embedded handlers, etc.) that allow Python code execution but restrict available calls and do not allow access to methods like os.system.
The proposed code acts as an alternative to calling os.system, functioning by exploiting a vulnerability in CPython. The exploit works with all versions of Python 3 on x86-64 systems and demonstrates stable operation in Ubuntu 22.04, even with PIE, RELRO, and CET protection modes enabled. The process involves retrieving the address of one of the functions in the executable CPython code from Python code. Based on this address, the base address of CPython in memory and the address of the system() function in the loaded instance of libc are calculated. Finally, a direct jump to the specified address of system is initiated by substituting the pointer of the first argument with the string '/bin/sh'.
Source: opennet.ru
