

A vulnerability has been identified in the uBlock Origin content blocking system, allowing crashes or memory exhaustion while navigating to specially crafted URLs that fall under strict blocking filters. The vulnerability manifests only when directly accessing the problematic URL, such as by clicking on a link.
The vulnerability has been addressed in the uBlock Origin update 1.36.2. A similar issue also affects the uMatrix extension, but its support has been discontinued and no further updates are released. There are no workarounds for protection in uMatrix (initially, it was suggested to disable all strict blocking filters via the 'Assets' tab, but this recommendation was deemed insufficient and problematic for users with their own blocking rules). In ηMatrix, a fork of uMatrix from the Pale Moon project, the vulnerability was fixed in release 4.4.9.
The strict blocking filter is usually defined at the level domains and implies a prohibition on any connections, even when directly accessing a link. The vulnerability is caused by the fact that, during the transition to a page that falls under the strict blocking filter, the user is shown a warning that provides information about the blocked resource, including the URL and query parameters. The problem is that uBlock Origin parses the query parameters recursively and adds them to the DOM tree without taking nesting levels into account.
Processing a specially crafted URL in uBlock Origin for Chrome can cause the process running the browser extension to crash. After the crash, until the process with the extension restarts, the user remains without blocking unwanted content. Memory exhaustion is observed in Firefox.
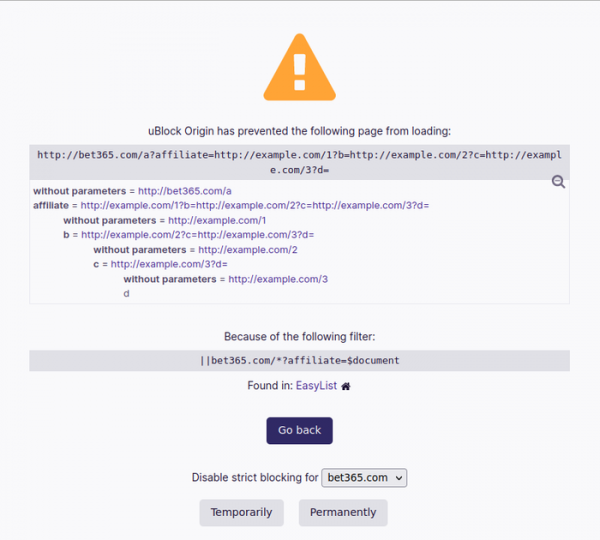
Source: opennet.ru
