

Three vulnerabilities have been identified in the developing Kubernetes ingress controller ingress-nginx that allow access to the Ingress object settings in the default configuration, where, among other things, credentials for accessing Kubernetes servers are stored, enabling privileged access to the cluster. The issues only occur in the ingress-nginx controller from the Kubernetes project and do not affect the kubernetes-ingress controller maintained by NGINX developers.
The ingress controller acts as a gateway and is used in Kubernetes to manage access from the external network to services within the cluster. The ingress-nginx controller is the most popular and utilizes server NGINX is used for proxying requests to the cluster, routing external requests, and load balancing. The Kubernetes project provides basic ingress controllers for AWS, GCE, and nginx, the latter of which is not related to the kubernetes-ingress controller maintained by F5/NGINX.
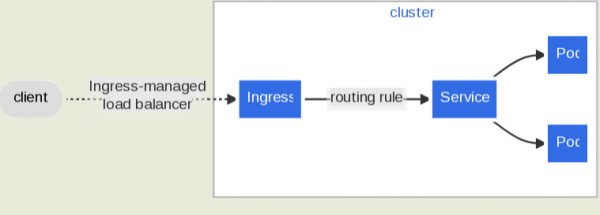
The vulnerabilities CVE-2023-5043 and CVE-2023-5044 allow for code execution with the ingress controller process's rights by substituting parameters "nginx.ingress.kubernetes.io/configuration-snippet" and "nginx.ingress.kubernetes.io/permanent-redirect." Among other things, the obtained access rights allow for the extraction of the token used for cluster management authentication. The vulnerability CVE-2022-4886 allows for bypassing file path checks using the log_format directive. server The first two vulnerabilities manifest only in ingress-nginx releases prior to version 1.9.0, while the last one affects versions prior to 1.8.0. To carry out an attack, an attacker must have access to the ingress object configuration, for instance, in multi-tenant Kubernetes clusters where users are allowed to create objects in their namespace.
Three vulnerabilities have been identified in the developing Kubernetes ingress controller ingress-nginx that allow access to the Ingress object settings in the default configuration, among other things, they store credentials.
Source: opennet.ru
