

The release of the Kata Containers project 3.2 has been published, developing a stack for running containers using isolation based on full virtualization mechanisms. The project was created by Intel and Hyper through the merging of Clear Containers and runV technologies. The project's code is written in Go and Rust and is distributed under the Apache 2.0 license. The development of the project is overseen by a working group created under the auspices of the independent OpenStack Foundation, which includes companies like Canonical, China Mobile, Dell/EMC, EasyStack, Google, Huawei, NetApp, Red Hat, SUSE, and ZTE.
At the core of Kata is a runtime that allows the creation of compact virtual machines running with a fully-fledged hypervisor instead of traditional containers that use a shared Linux kernel and are isolated using namespaces and cgroups. The application of virtual machines provides a higher level of security, protecting against attacks resulting from the exploitation of vulnerabilities in the Linux kernel.
Kata Containers is geared towards integration into existing container isolation infrastructures with the possibility of using such virtual machines to enhance the security of traditional containers. The project provides mechanisms to ensure compatibility of lightweight virtual machines with various container isolation infrastructures, container orchestration platforms, and specifications such as OCI (Open Container Initiative), CRI (Container Runtime Interface), and CNI (Container Networking Interface). Tools for integration with Docker, Kubernetes, QEMU, and OpenStack are available.
Integration with container management systems is achieved through a layer that simulates container management, which accesses the controlling agent in the virtual machine through a gRPC interface and a special proxy. Inside the virtual environment, which is launched by the hypervisor, a specially optimized Linux kernel is used, containing only the minimum set of necessary features.
Dragonball Sandbox (a KVM-based hypervisor optimized for containers) is supported as the hypervisor, along with QEMU tools, Firecracker, and Cloud Hypervisor. The environment includes an initialization daemon and an agent. The agent facilitates the execution of user-defined container images in OCI format for Docker and CRI for Kubernetes. When used with Docker, a separate environment is created for each container. the virtual machine, meaning that the environment running on top of the hypervisor is used for nested container execution.
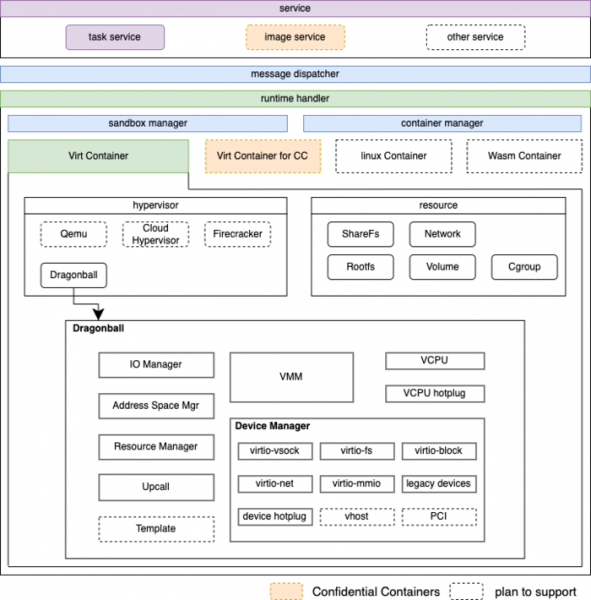
To reduce memory usage, the DAX mechanism (direct access to the file system bypassing the page cache without using block device levels) is applied, while the KSM (Kernel Samepage Merging) technology is used for deduplicating identical memory regions, allowing for resource sharing of the host system and connecting a shared template of the environment to different guest systems.
In the new version:
- In addition to supporting the AMD64 (x86_64) architecture, releases are also made for ARM64 (Aarch64) and s390 (IBM Z) architectures. Support for the ppc64le (IBM Power) architecture is in development.
- Access to container images is organized using the Nydus 2.2.0 filesystem, which employs content-based addressing for efficient collaboration with standard images. Nydus supports on-the-fly image loading (loading only when necessary), ensures deduplication of repeated data, and can utilize different backends for actual storage. POSIX compatibility is provided (similar to Composefs, the Nydus implementation combines the capabilities of OverlayFS with EROFS or FUSE module).
- The Kata Containers project has integrated the Dragonball virtual machine manager, which will now be developed in a shared repository.
- A debugging feature has been added to the kata-ctl utility for connecting to a virtual machine from the host environment.
- GPU management capabilities have been expanded, and support for GPU passthrough into containers for confidential computing (Confidential Container) has been added, which provides data, memory, and execution state encryption to protect against compromise of the host environment or hypervisor.
- A device management subsystem has been added to Runtime-rs for devices used in containers or sandbox environments. Support for working with vfio, block, network, and other types of devices is included.
- Compatibility with OCI Runtime 1.0.2 and Kubernetes 1.23.1 is ensured.
- It is recommended to use Linux kernel version 6.1.38 with patches.
- The development has transitioned from the Jenkins continuous integration system to GitHub Actions.
Source: opennet.ru
