

ESET specialists have uncovered a new malicious campaign targeting Russian-speaking users of the World Wide Web.
Cybercriminals have been distributing an infected version of the Tor browser for several years, using it to monitor victims and steal their bitcoins. The infected web browser was spread through various forums as a legitimate Russian-language version of Tor Browser.
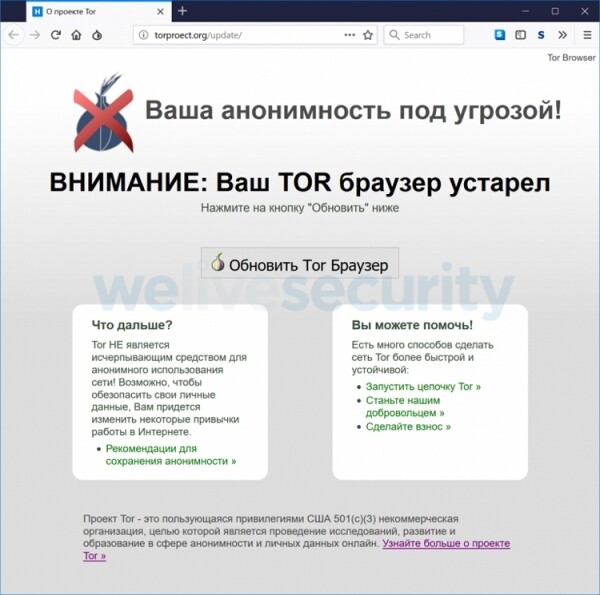
The malware allows attackers to see which websites the victim is currently visiting. Theoretically, they could also change the content of the visited page, intercept typed data, and display false messages on websites.
“The criminals did not change the browser's binary files. Instead, they modified the settings and extensions, so regular users might not notice the difference between the original and the infected versions,” ESET experts say.
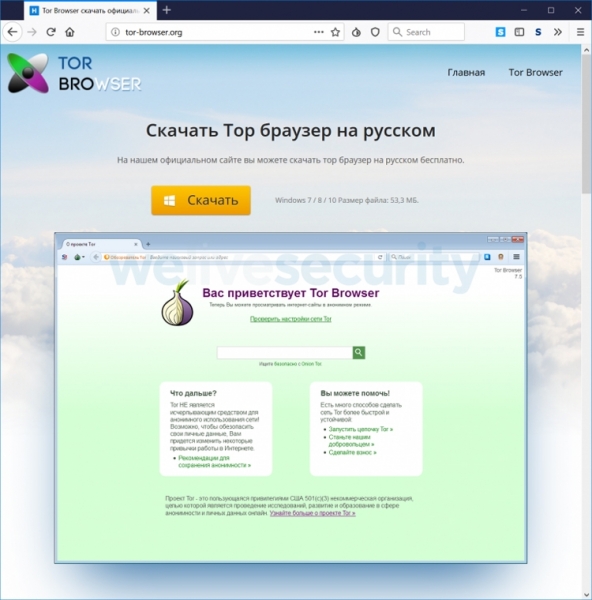
The attack scheme also involves altering QIWI payment system wallet addresses. The malicious version of Tor automatically replaces the original bitcoin wallet address with that of the criminals when the victim attempts to pay for a purchase with bitcoins.
The damage caused by the criminals amounts to at least 2.5 million rubles. The actual amount stolen could turn out to be much higher.
Source: 3dnews.ru
