

Trace files, or Prefetch files, have been around in Windows since the XP era. Since then, they have assisted digital forensics and computer incident response specialists in tracking the execution traces of programs, including malicious ones. Leading computer forensics expert at Group-IB, Oleg Skulkin explains what can be found using Prefetch files and how to do it.
Prefetch files are stored in the directory %SystemRoot%Prefetch and are used to speed up program launch processes. If we take a look at any of these files, we will see that its name consists of two parts: the name of the executable file and a checksum derived from its path, which consists of eight characters.
Prefetch files contain a wealth of information from a forensic standpoint: the name of the executable file, the number of launches, lists of files and directories interacted with by the executable file, and, of course, timestamps. Forensic specialists typically use the creation date of a particular Prefetch file to determine the date of the program's first launch. Additionally, these files store the last launch date and, starting from version 26 (Windows 8.1), timestamps for the seven most recent launches.
Let's take one of the Prefetch files, extract the data using PECmd by Eric Zimmermann, and examine each part. For demonstration, I will extract data from the file CCLEANER64.EXE-DE05DBE1.pf.
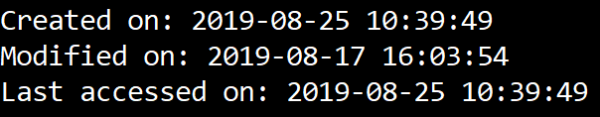
So, let's start from the top. Of course, we have timestamps for the creation, modification, and access of the file:
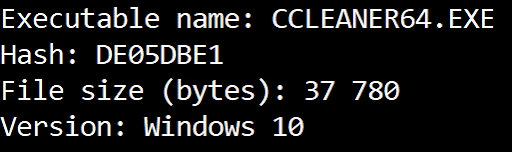
Following those are the executable file name, checksum of its path, size of the executable file, and the version of the Prefetch file:
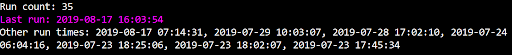
Since we are dealing with Windows 10, next we will see the number of launches, date and time of the last launch, and seven additional timestamps indicating previous launch dates:
Next is the volume information, including its serial number and creation date:

And last but not least is the list of directories and files that the executable file interacted with:
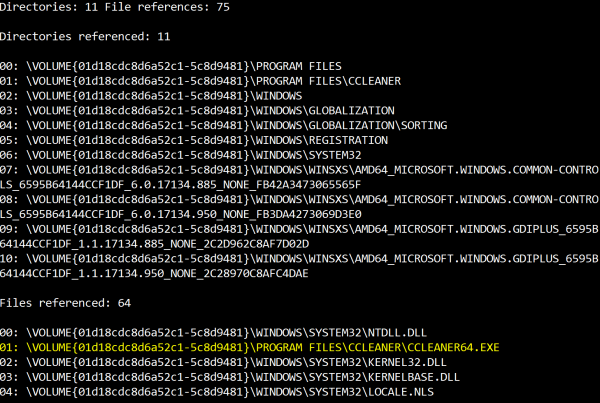
Today, I want to focus on the directories and files that the executable file interacted with. It's this data that allows digital forensics specialists, incident responders, or proactive threat hunters to not only establish the execution of a file but also, in some cases, reconstruct the specific tactics and techniques used by attackers. Nowadays, cybercriminals often use tools to irretrievably delete data, such as SDelete, so the ability to recover at least traces of tactics and techniques is essential for any modern defender—a computer forensics expert, incident response specialist, or Threat Hunter expert.
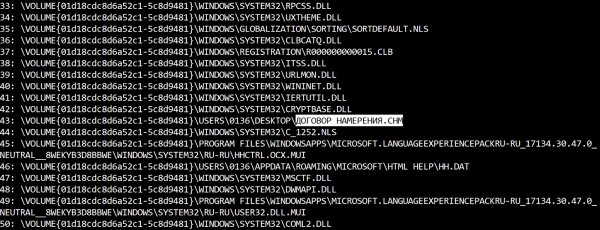
Let's start with the tactic Initial Access (TA0001) and the most popular technique—Spearphishing Attachment (T1193). Some cybercriminal groups take a creative approach to choosing such attachments. For instance, the Silence group has used CHM files (Microsoft Compiled HTML Help) for this purpose. This brings us to another technique—Compiled HTML File (T1223). Such files are executed using hh.exe, and if we extract data from its Prefetch file, we will learn which specific file was opened by the victim:
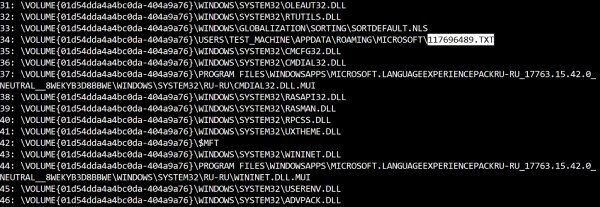
Let's continue working with real case examples and move to the next tactic Execution (TA0002) and the technique CSMTP (T1191). The Microsoft Connection Manager Profile Installer (CMSTP.exe) can be used by attackers to run malicious scripts. A good example is the Cobalt group. If we extract data from the Prefetch file cmstp.exe, we will again find out what was executed:
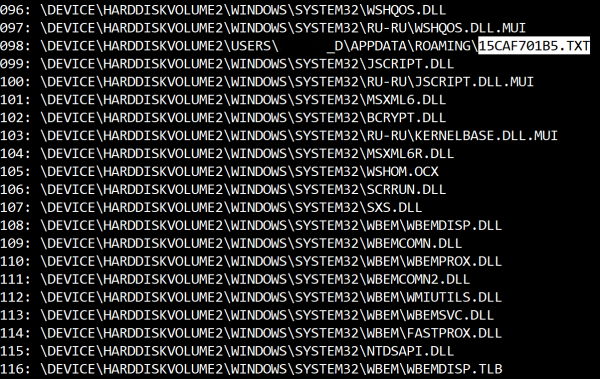
Another popular technique is Regsvr32 (T1117). Regsvr32.exe is also frequently used by attackers for execution. Here's another example from the Cobalt group: if we extract data from the Prefetch file regsvr32.exe, we will again see what was executed:
The next tactics are Persistence (TA0003) and Privilege Escalation (TA0004), as well as Application Shimming (T1138) as a technique. This technique was used by Carbanak/FIN7 for persistence in the system. Typically, to work with databases containing program compatibility information (.sdb), the tool used is sdbinst.exe. Therefore, the Prefetch file of this executable can help us identify the names and locations of such databases:
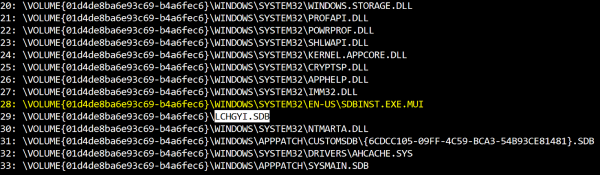
As shown in the illustration, we have not only the name of the file used for installation but also the name of the installed database.
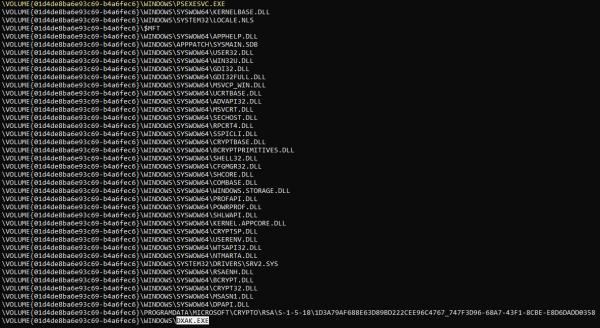
Let’s take a look at one of the most typical examples of network exploitation (TA0008) — PsExec, which utilizes administrative shares (T1077). A service named PSEXECSVC (of course, any other name can be used if the attackers specify it) -r) will be created on the target system, therefore if we extract data from the Prefetch file, we will see that it was executed:
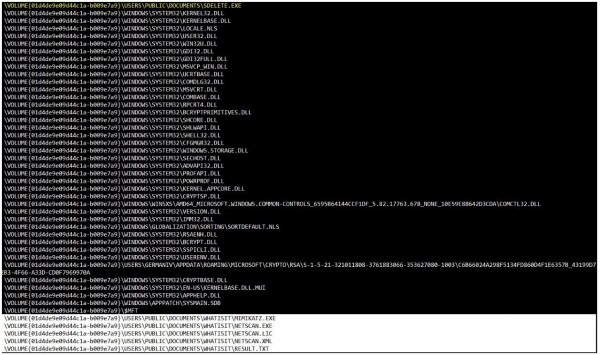
I will conclude, perhaps, with what I started — file deletion (T1107). As I mentioned earlier, many attackers use SDelete for permanent file deletion at different stages of the attack lifecycle. If we look at the data from the Prefetch file sdelete.exe, we will see what exactly was deleted:
Of course, this is not an exhaustive list of techniques that can be detected during Prefetch file analysis, but it should be enough to understand that such files can help not only to find traces of execution but also to reconstruct the specific tactics and techniques of the attackers.
Source: habr.com
