

A sort utility supplied with the GNU Coreutils package has a vulnerability (CVE-2025-5278) that leads to accessing data outside the buffer boundary when sorting using the syntax "+POS1[.C1][OPTS]", which is used to define the sort keys in the processed data. The issue is caused by an integer overflow in the function begfield(), which allows reading the content of one byte of data beyond the buffer. This vulnerability can be exploited to cause application crashes or to leak information from the process by passing specially crafted sorting parameters to the attacker. The issue has been present since version 7.2 (2009) and has been temporarily addressed in the form of a patch.
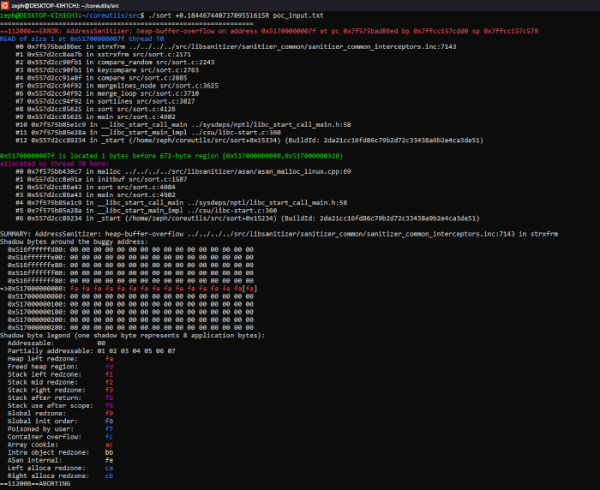
The problem can be reproduced by attempting to sort a file containing the string "aa\nbb" with the command "./sort +0.18446744073709551615R poc_input.txt". The sort utility must be compiled with Address Sanitizer enabled (the option "-fsanitize=address").
Forrás: opennet.ru
