

A Linux Foundation organization, in collaboration with Harvard's Lab for Innovation in Science, has prepared a new edition of the Census III study aimed at identifying the most widely used open projects that require prioritized security audits. The study analyzed shared open source code implicitly used in various corporate projects in the form of dependencies downloaded from external repositories. More than 12 million open libraries used in applications across 10,000 different companies were examined.
Based on the collected statistics, lists have been formed of the 500 most frequently used libraries whose security and maintenance quality require special attention, as vulnerabilities and compromises of third-party dependencies can invalidate all efforts to enhance the security of the core product. A total of 8 lists have been proposed, ranked according to various criteria such as supply in the NPM repository and the availability of version information when defining dependencies.
Néhány megállapítás:
- 17% of the 50 most popular projects not represented in the NPM repository have only one developer, while 40% have one or two developers who have made 80% of the commits.
- Compared to the previous report from 2022, there has been an increase in the use of packages for interacting with cloud services among important packages.
- The transition of projects from Python 2 to Python 3 continues.
- The popularity of Maven packages remains, and the use of packages from PIP (Python), Cargo (Rust), and NuGet (.NET) repositories is growing.
- As before, there is a need for standardized naming schemes for software components.
- The relevance of protecting developer accounts has increased. Many of the most in-demand packages are hosted under the accounts of specific developers, which are less secure than accounts created under organizational projects.
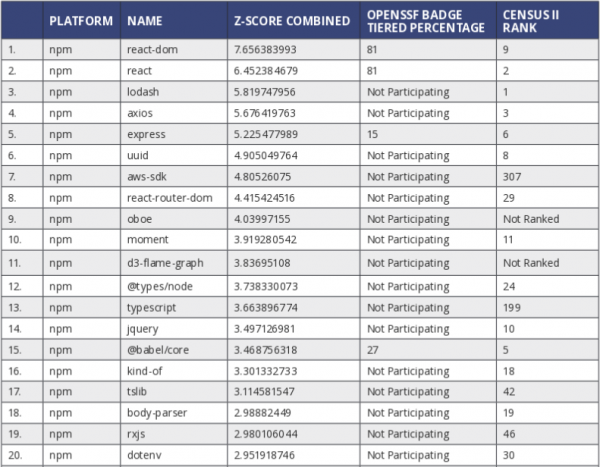
- The 20 most frequently used JavaScript packages from the NPM repository, downloaded by applications without version binding:

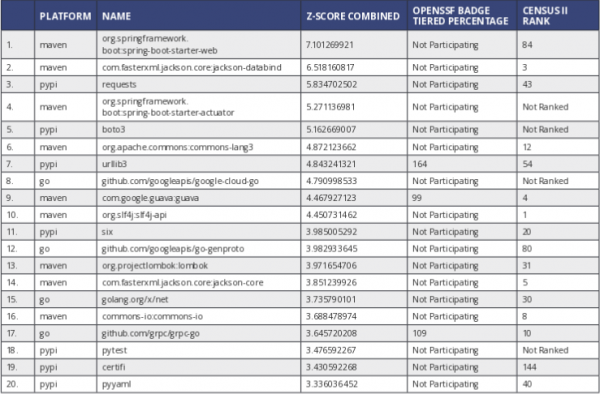
- The 20 most frequently used packages from repositories other than NPM, downloaded by applications without version binding:

Forrás: opennet.ru
