

A JFrog researcher discovered a token in the Docker image 'cabotage-app' that provides admin access to the Python, PyPI, and Python Software Foundation repositories on GitHub. The token was found in the binary file '__pycache__/build.cpython-311.pyc' containing cached compiled bytecode.
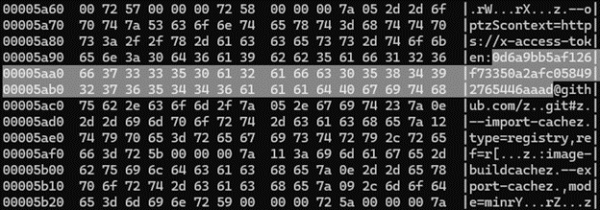
According to representatives from the PyPI repository, the token was created in 2023 for the developer ewdurbin (Ee Durbin), who serves as the Director of Infrastructure at the Python Software Foundation. The token provided admin access to all repositories and organizations within the project, including all repositories of the organizations pypi, python, psf, and pypa. The problematic Docker image with the token was published in the Docker Hub catalog on March 3, 2023, and was removed on June 11, 2024, meaning it was publicly accessible for 16 months. The token was revoked on June 28.
Notably, the available source texts on which the problematic bytecode file was generated do not mention the token. The author of the code explained that during the development of the cabotage-app5 toolkit, they encountered limitations on GitHub API access intensity while performing automated file uploads from GitHub. To bypass the limits imposed on anonymous requests to GitHub, they temporarily added their working token into the code. Before publishing the code, the token was removed, but the developer did not take into account that the mention of the token was cached in the precompiled bytecode file that subsequently ended up in the Docker image. def _fetch_github_file( — github_repository='owner/repo', ref='main', access_token=None, filename='Dockerfile' + github_repository='owner/repo', + ref='main', + access_token='0d6a9bb5af126f73350a2afc058492765446aaad', + filename='Dockerfile', ):
The audit of activity in the repositories on GitHub conducted by Python developers did not reveal any external attempts to access using the exposed token. Given that GitHub has been the primary platform for CPython development since 2017, the token falling into the wrong hands could have led to a complete compromise of the infrastructure used for Python development and the PyPI repository, as well as attempts to integrate backdoors into CPython and the PyPI package manager.
Az incidens rávilágít arra, hogy a szivárgások elemzése nemcsak a forráskódban, konfigurációs fájlokban és környezeti változókban fontos, hanem a bináris fájlokban is. A Python kontextusában a felhasználóknak figyelniük kell a letöltött projektekben található pyc fájlokra is, mivel ezek a fájlok olyan rejtett módosításokat tartalmazhatnak, amelyek nem találhatók meg a forráskódban.
Forrás: opennet.ru
