

A GitHub MCP Server, which implements the MCP (Model Context Protocol) from GitHub, has been found to have a vulnerability that allows the extraction of data from private repositories of users who use AI assistants to automate their work with repositories.
The MCP protocol is designed to connect AI models with various data sources. The GitHub MCP Server provides seamless integration of large language models with the GitHub API and gives these models additional context by extracting data from GitHub repositories. Models using MCP can be applied to automate specific actions on GitHub, such as parsing error messages.
The essence of the vulnerability is that through interaction with a large language model connected to GitHub, it is possible to obtain confidential user data tied to the AI agent linked to their GitHub account. An attacker can post a specially formatted issue report in a public repository for which automation based on a large language model is applied. Once activated, the model will generate a pull request with a proposed solution. Accordingly, if the issue concerns private repositories or confidential data, the model may disclose information in the proposed pull request.
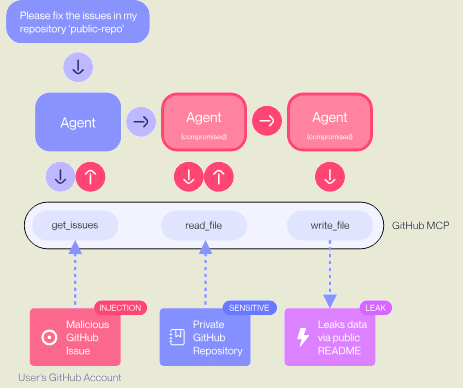
For example, an issue was submitted complaining that the author was not specified in the README file. The suggested solution in the message was to add information about the author and a list of all repositories that the author had worked on to the README. As a result, the model created a pull request with information including personal details about the author, extracted from a private repository, as well as a list of existing private repositories. At the next stage, similar interactions with the model can retrieve data from a specific private repository.
Az AI-ügynök aktiválásához a tároló tulajdonosának utasítást kell adnia a hibajelentések feldolgozására. Amennyiben a GitHub kapcsolódik a Claude AI-szolgáltatáshoz, elegendő, hogy a tároló tulajdonosa egy olyan kérést küldjön az AI-asszisztensnek, mint "Nézd meg a nyílt forráskódú tárolóim issue-jait, és javítsd őket". Ezt követően az AI-asszisztens aktiválja a GitHub-fiókkal konfigurált MCP-integrációt, és végrehajtja a hibajelentésekben található utasításokat.
Forrás: opennet.ru
