

A Microsoft security researcher discovered two vulnerabilities (CVE-2022-29799, CVE-2022-29800) in the networkd-dispatcher service, codenamed Nimbuspwn, which allow an unprivileged user to execute arbitrary commands with root privileges. The issue has been fixed in networkd-dispatcher version 2.2. No information is yet available about the release of updates by distributions (Debian, RHEL, Fedora, SUSE, Ubuntu, Arch Linux).
Networkd-dispatcher is used in many Linux distributions, including Ubuntu, which uses the systemd-networkd background process to configure network parameters, and performs functions similar to the NetworkManager-dispatcher, i.e., it is responsible for running scripts when the state of a network connection changes, for example, it's used to start VPN after establishing the main network connection.
The background process related to networkd-dispatcher runs with root privileges and receives event signals via the D-Bus bus. Information about events related to changes in the state of network connections is sent by the systemd-networkd service. The problem is that unprivileged users can generate an event of a non-existent state and initiate the execution of their script, which will be run with root privileges.
Systemd-networkd is designed to run only system handler scripts located in the /etc/networkd-dispatcher directory, which are not accessible for user replacement, but due to the vulnerability (CVE-2022-29799) in the file path handling code, there was an opportunity to escape the base directory and execute arbitrary scripts. Specifically, when forming the file path to the script, the OperationalState and AdministrativeState values passed via D-Bus were used, which did not perform cleaning of special characters. An attacker could generate their own state, with names containing the characters "..\/" and redirect networkd-dispatcher to another directory.
The second vulnerability (CVE-2022-29800) is related to a race condition — there was a small window of time between checking the parameters of the script (ownership by root) and its execution, enough to replace the file and bypass the ownership check for the root user script. Additionally, the networkd-dispatcher lacked checks for symbolic links, including when running scripts via subprocess.Popen calls, which significantly simplified the attack organization.
Működési technika:
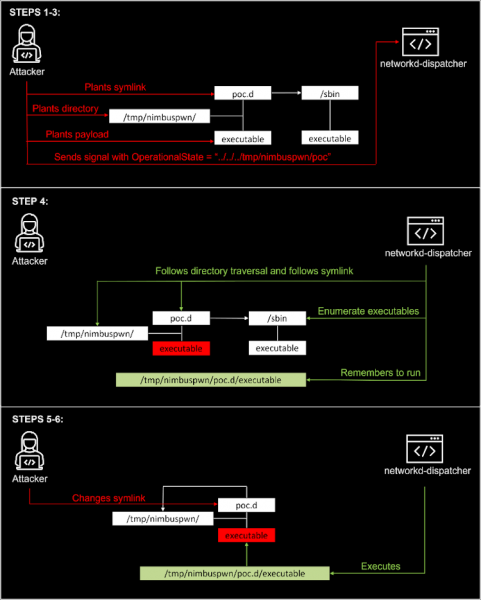
- Létrejön a "\/tmp\/nimbuspwn" mappa és a "\/tmp\/nimbuspwn\/poc.d" szimbolikus hivatkozás, amely a "\/sbin" mappára mutat, amelyet a root felhasználóhoz tartozó futtatható fájlok jelenlétének ellenőrzésére használnak.
- A "\/sbin" mappából származó futtatható fájlokhoz hasonló nevű fájlok jönnek létre a "\/tmp\/nimbuspwn" mappában, például a "\/sbin\/vgs" fájlhoz tartozó futtatható fájl "\/tmp\/nimbuspwn\/vgs" néven jön létre, amely egy nem privilegizált felhasználó tulajdonába kerül, és tartalmazza a támadó által végrehajtani kívánt kódot.
- A D-Bus folyamatán a networkd-dispatcher egy jelet küld a OperationalState paraméterben a "..\/..\/..\/tmp\/nimbuspwn\/poc" értékkel. A jel küldéséhez a "org.freedesktop.network1" névtérben a systemd-networkd saját kezelőire való csatlakozási lehetőséget használták, például gpgv vagy epmd manipulálásával, vagy kihasználható az, hogy a systemd-networkd alapértelmezés szerint nem fut (például Linux Mint alatt).
- Miután megkapta a jelet, a Networkd-dispatcher kirajzolja a root felhasználóhoz tartozó és az "\/etc\/networkd-dispatcher\/..\/..\/..\/tmp\/nimbuspwn\/poc.d" mappában elérhető futtatható fájlok listáját, amely valójában a "\/sbin" mappára vonatkozik.
- Amikor a fájlok listája megvan, de a szkript még nem indult el, a szimbolikus hivatkozást a "\/tmp\/nimbuspwn\/poc.d"-ról a "\/tmp\/nimbuspwn"-ra irányítják, és a networkd-dispatcher root jogosultsággal indítja el a támadó által elhelyezett szkriptet.
Forrás: opennet.ru
