

A Xubuntu distribution official website has been compromised by unknown attackers, who altered the download page links to torrents, replacing them with the file "https://xubuntu.org/wp-content/Xubuntu-Safe-Download.zip." As a result, only links to a malicious archive and available mirrors remained on the download page. Xubuntu developers have not commented on the situation yet, but a few hours ago they removed the malicious archive and blocked access to the section "xubuntu.org/download/", redirecting visitors to the site’s main page.
The archive.org service created copies of xubuntu.org on October 11 and 18 — on October 11, the page had not yet been altered, while on October 18, the page already featured a malicious change. According to preliminary checksum analysis, the project mirrors distributing the ISO images have not been affected and correspond to the benchmark cdimage.ubuntu.com. Signs of compromise have only been observed on the xubuntu.org website, which uses a WordPress tartalomkezelő rendszert. It is presumed that the hack was carried out through an outdated plugin for WorkPress that contains a vulnerability.
The archive distributed by the attackers, "Xubuntu-Safe-Download.zip," contains an executable file for the Windows platform, which is presented as an Xubuntu installer. Checking the specified file with VirusTotal reveals the presence of malware.
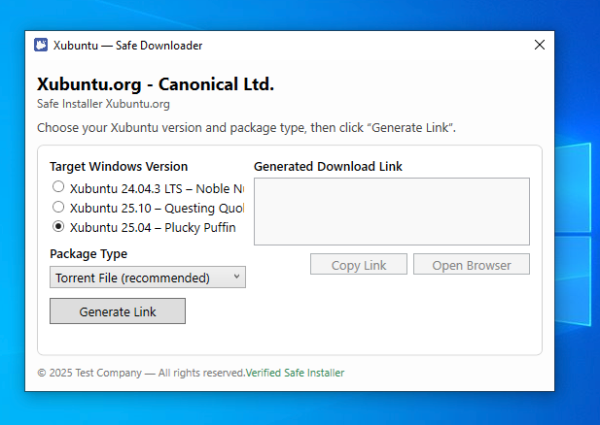
When the executable file is run, a fake interface appears, including fields for selecting the version of the distribution for download and the type of package, as well as a "Generate Download Link" button. When the button is pressed, the file "elzvcf.exe" is saved in the "AppData Roaming" directory, and its execution is configured in the Windows registry to occur at system startup. According to preliminary information, the malware analyzes clipboard data and replaces Bitcoin, Litecoin, Ethereum, Dogecoin, Tron, Ripple, and Cardano wallet addresses with those of the attackers.
Interestingly, on September 10, one user complained about a blog post on the xubuntu.org website advertising a casino, but this blog post was promptly removed, and the incident did not develop further (presumably, it was thought that the advertisement had been placed by malware on the user's side).
Forrás: opennet.ru
