

Details have emerged about vulnerabilities in GitHub Actions handlers that are automatically triggered by pull requests to the Nixpkgs package repository, used in the NixOS distribution and the ecosystem associated with the Nix package manager. The vulnerability allowed an outsider to extract a token granting write and read access to the source code of all packages hosted in Nixpkgs. This token enabled direct changes to any package via the project's Git repository, bypassing review and approval processes.
The potential compromise of Nixpkgs and insertion of one’s own code into any package was demonstrated by security researchers at the NixCon conference last October and was immediately addressed in the project infrastructure. However, details about the attack were not disclosed until a year later. The problem was linked to the use of GitHub Actions handlers in the Nixpkgs GitHub repository that were tied to the 'pull_request_target' event and conducted automated checks upon receiving new pull requests.
Unlike the 'pull_request' event, 'pull_request_target' handlers are granted write and read access to the build environment, which requires special attention when dealing with data passed in a pull request. In one of the handlers linked to 'pull_request_target', a check of the file 'OWNERS' provided in the pull request was conducted, for which the codeowners-validator utility was collected and invoked: steps: — uses: actions/checkout@eef61447b9ff4aafe5dcd4e0bbf with: ref: refs/pull/$/merge path: pr — run: nix-build base/ci -A codeownersValidator — run: result/bin/codeowners-validator env: OWNERS_FILE: pr/ci/OWNERS
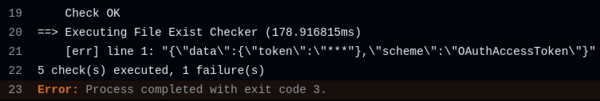
The problem was that in the case of an error in formatting the OWNERS file, the codeowners-validator utility output the contents of the incorrectly formatted line to the public standard log. The attack revolved around placing a symbolic link named OWNERS in the pull request, which pointed to a '.credentials' file containing credentials stored in the build environment. Consequently, the processing of this file led to an error and the output in the public log of the first line containing the repository access token.
Bovendien is er een andere kwetsbaarheid gevonden in de handler die de regels van editorconfig controleert. stappen: — naam: Verkrijg lijst van gewijzigde bestanden uit PR run: gh api […] | jq [ … ] > «$HOME/changed_files» — uses: actions/checkout@eef61447b9ff4aafe5dcd4e0bbf5d482be7e7871 with: ref: refs/pull/$/merge — naam: Controleren van EditorConfig run: cat «$HOME/changed_files» | xargs -r editorconfig-checker
In dit geval lag het probleem bij het gebruik van de tool «xargs» om het programma editorconfig-checker uit te voeren met elk bestand uit de pull-aanvraag. Omdat de bestandsnamen niet op juistheid werden gecontroleerd, kon een aanvaller een bestand met speciale tekens in de pull-aanvraag opnemen, dat bij het uitvoeren van de tool editorconfig-checker als commandoregelargumenten zou worden verwerkt. Bijvoorbeeld, bij het aanmaken van het bestand «—help» zou de tool editorconfig-checker een hint geven over de beschikbare opties.
Bron: opennet.ru
