

Hackers discovered a vulnerability in Windows for attacks via the long outdated and disabled Internet Explorer browser, despite Microsoft's security measures. This exploits files with .url and .hta shortcuts. If the user confirms their opening, malware is immediately downloaded to their computer.
Cybersecurity specialists from Check Point have uncovered a new scheme for attacking computers running Windows 10 and Windows 11, exploiting a vulnerability in the outdated Internet Explorer browser. PCMag. Although Microsoft officially ended support for Internet Explorer and permanently disabled it in its operating system last year, hackers have found a way to install malware through it.
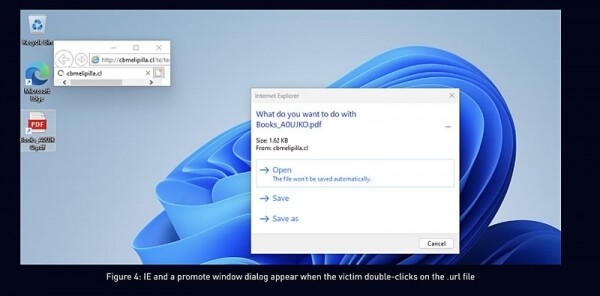
Check Point researcher Haifei Li , noted that attackers use Windows shortcut files with the .url extension, which can be configured to call Internet Explorer. This method does not allow bypassing the modern protection systems present in newer browsers like Chrome or Edge.
The attack is particularly effective when using phishing emails or malicious attachments. Li discovered that hackers disguise shortcuts as PDF files. When such a shortcut is opened, Internet Explorer downloads malware in the form of a .hta file if the user confirms all prompts.
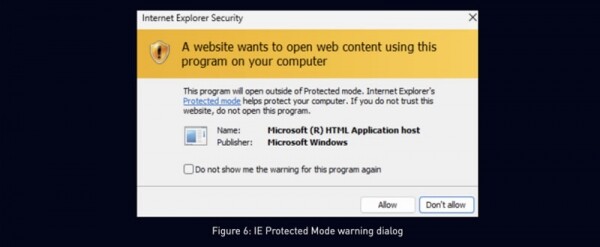
Will Dormann, a security expert, pointed out that modern browsers block the downloading of .hta files, while Internet Explorer merely displays a text warning, which users can easily disregard due to a lack of knowledge. The particular danger lies in the fact that Microsoft has ceased to release security updates for Internet Explorer, which allows hackers to exploit unpatched vulnerabilities through this browser.
Check Point's research revealed that these attacks have been ongoing at least since January 2023. The good news is that in response to the discovered vulnerability, Microsoft has released a patch that prevents launching Internet Explorer through shortcut files. Experts also recommend that Windows users exercise particular caution when dealing with files ending in .url received from unreliable sources.
Fonte:
Fonte: 3dnews.ru
