

Bem-vindo a um novo ciclo de artigos, desta vez sobre a investigação de incidentes, especificamente sobre a análise de malware utilizando a forense da Check Point. Anteriormente, publicamos sobre o funcionamento do Smart Event, mas desta vez vamos analisar os relatórios forenses sobre eventos específicos em diferentes produtos da Check Point:
Por que a forense de incidentes evitados é importante? À primeira vista, pegar um vírus já é bom, mas por que se preocupar em analisá-lo? Como mostra a prática, é recomendável não apenas bloquear o ataque, mas também entender como ele funciona: qual foi o ponto de entrada, qual vulnerabilidade foi explorada, quais processos foram envolvidos, se o registro e o sistema de arquivos foram afetados, qual família de vírus, qual o dano potencial, etc. Essas e outras informações úteis podem ser obtidas em relatórios forenses detalhados da Check Point (tanto em formato de texto quanto gráfico). Obter tal relatório manualmente é muito difícil. Esses dados podem ajudar a tomar as medidas necessárias e a eliminar a possibilidade de sucesso de ataques semelhantes no futuro. Hoje, vamos analisar o relatório forense da Check Point SandBlast Network.
SandBlast Network
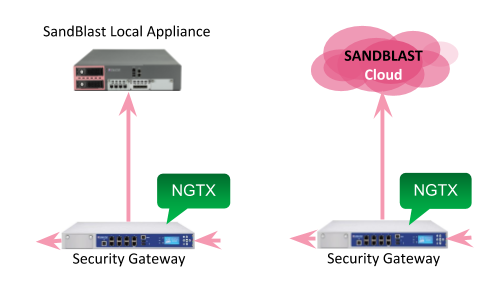
O uso de sandbox para fortalecer a proteção do perímetro da rede já se tornou algo comum e um componente tão essencial quanto o IPS. Na Check Point, o blade de Threat Emulation é responsável pela funcionalidade da sandbox, que faz parte das tecnologias SandBlast (também inclui Threat Extraction). Já publicamos anteriormente também para a versão Gaia 77.30 (recomendo muito a visualização se você não entende sobre o que estamos falando agora). Em termos de arquitetura, desde então, nada mudou fundamentalmente. Se você tem um Check Point Gateway no perímetro da sua rede, pode usar duas opções de integração com a sandbox:
- SandBlast Local Appliance — um appliance SandBlast adicional é instalado na sua rede, para o qual os arquivos são enviados para análise.
- SandBlast Cloud — os arquivos são enviados para análise na nuvem da Check Point.
A sandbox can be considered the last line of defense on the network perimeter. It connects only after classic analysis tools—like antivirus and IPS—have been employed. And if such traditional signature-based tools provide virtually no analytics, the sandbox can provide a detailed explanation of why a file was blocked and what malicious actions it performs. Such forensic reports can be obtained from both local and cloud sandboxes.
Check Point Forensics Report
Suppose you, as an information security specialist, arrived at work and opened the dashboard in SmartConsole. Right away, you see incidents from the last 24 hours, and your attention is drawn to Threat Emulation events—the most dangerous attacks that were not blocked by signature-based analysis.
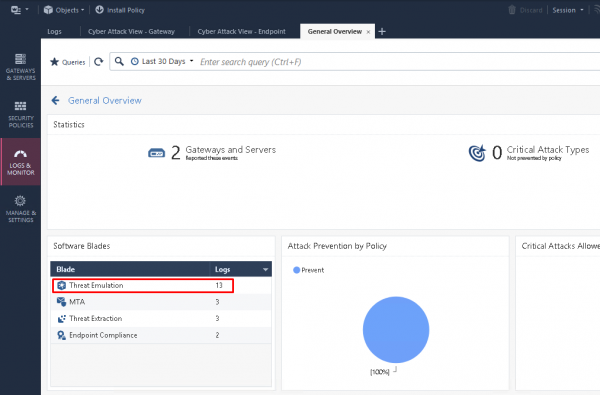
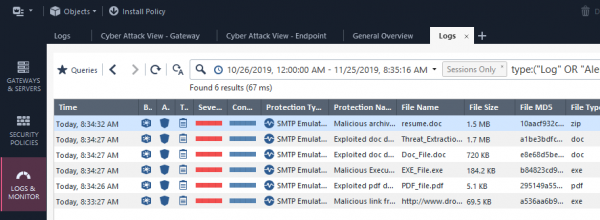
You can drill down into these events and view all logs for the Threat Emulation blade.
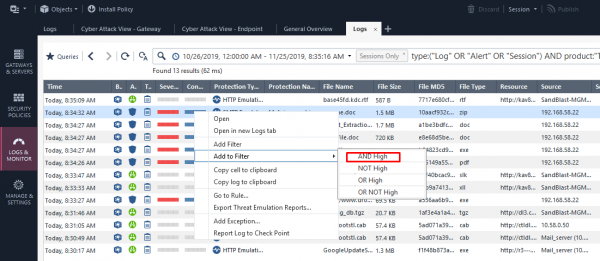
After that, you can further filter the logs by threat severity level, as well as by Confidence Level:
By exploring the event of interest, you can review overall information (src, dst, severity, sender, etc.):
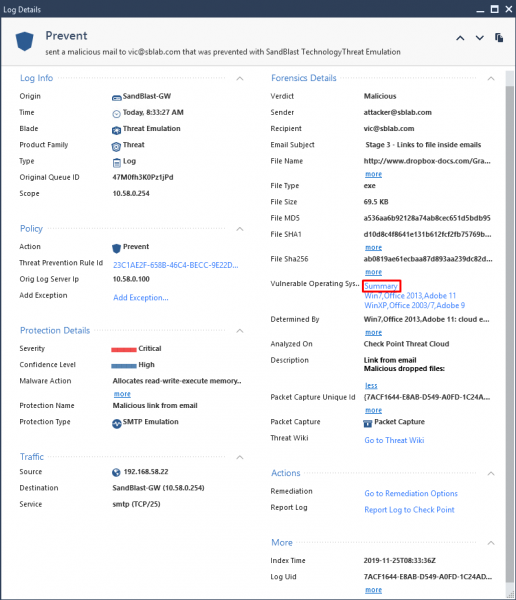
And there you can also notice a section Análise Forense with available Summary reports. By clicking on it, a detailed analysis of the malware opens up in the form of an interactive HTML page:
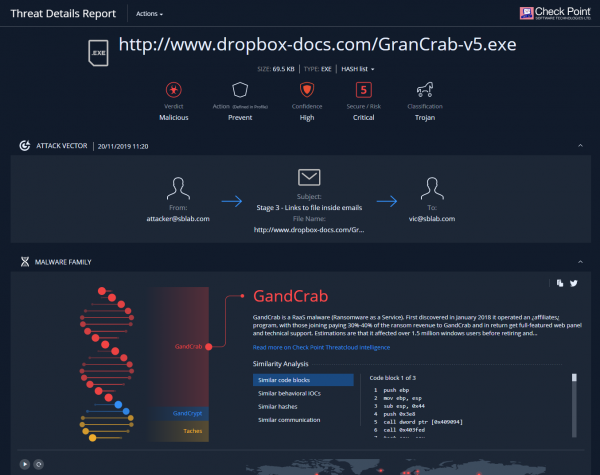
(This is part of the page. )
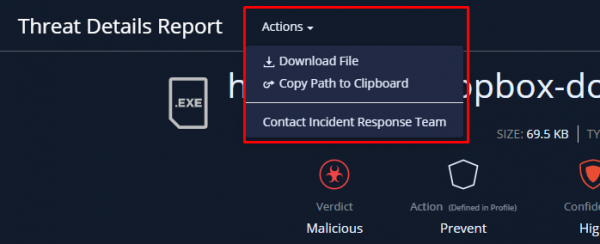
From this report, we can download the original malware (in a password-protected archive), or immediately contact the Check Point response team.
Further down, a beautiful animation shows, in percentage terms, how our sample relates to already known malicious code (including the code itself and macros). This analysis is provided using machine learning from Check Point Threat Cloud.
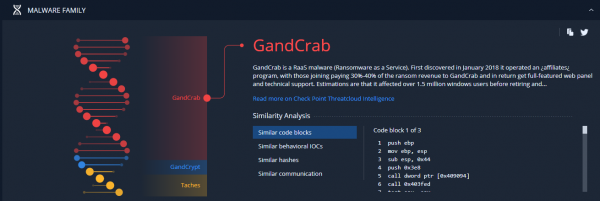
Then we can see which specific activities in the sandbox led to the conclusion about this file's maliciousness. In this case, we see the use of evasion techniques and attempts to download ransomware:
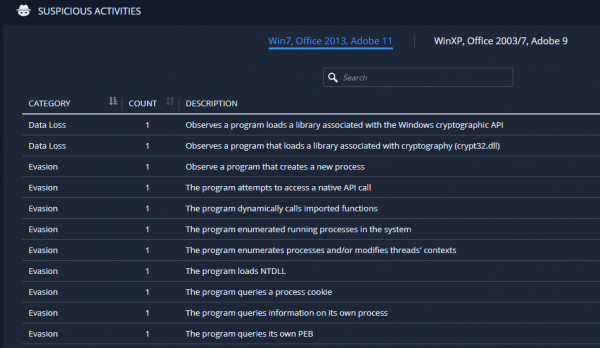
It can be noted that in this case, emulation was performed in two systems (Win 7, Win XP) and different software versions (Office, Adobe). Below is a video (slideshow) of the process of opening this file in the sandbox:
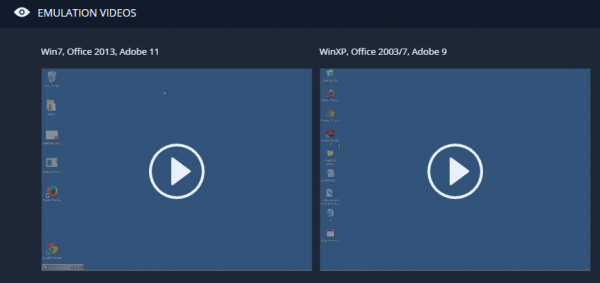
Example video:
At the very end, we can see in detail how the attack unfolded, either in table format or graphically:
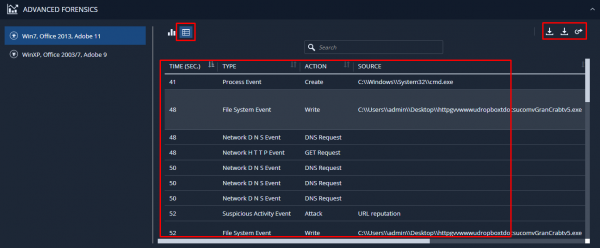
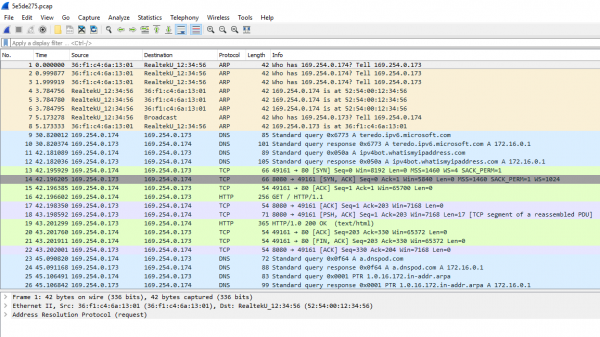
Lá podemos baixar essas informações em formato RAW e arquivo pcap, para uma análise detalhada do tráfego gerado no Wireshark:
Conclusão
Com essas informações, é possível fortalecer significativamente a segurança da sua rede. Bloquear hosts de distribuição de vírus, fechar vulnerabilidades exploradas, impedir possíveis retornos de C&C e muito mais. Não subestime essa análise.
Nos próximos artigos, abordaremos da mesma forma os relatórios do SandBlast Agent, SandBlast Mobile e também o CloudGuard SaaS. Então fique atento às atualizações (, , , )!
Fonte: habr.com
