

Funkcie:
- KISS;
- self-hosted;
- absence of fees (for example, bountysource and gitcoin take 10% of the payout);
- support for multiple cryptocurrencies (currently Bitcoin, Ethereum, and Cardano);
- support for GitLab, Gitea, and other Git hosting services is planned (and foreseen) in the future.
- a global task list from all (i.e., one at the time of writing the news) instances at donate.dumpstack.io.
How it works for GitHub from the repository owner's side:
- (optionally) it is necessary to deploy the service; you can use a ready configuration for NixOS;
- it is necessary to add GitHub Action — within it calls a utility that scans project tasks and adds/updates a comment about the current state of donation wallets, while the private part of the wallets is stored only on the donation server (in the future, with the possibility of moving it offline for large donations, for manual payout confirmation);
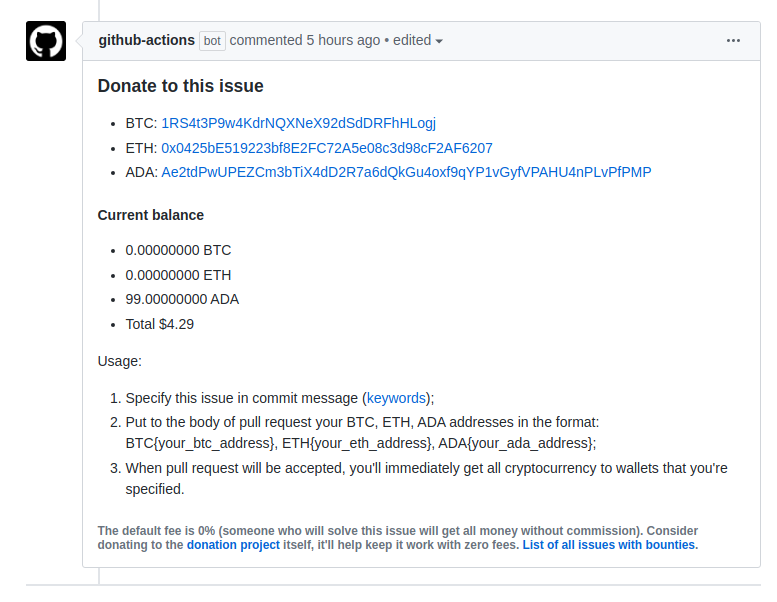
- a message from github-actions[bot] with the wallet addresses for donations (príklad).
How it works from the task executor's side:
- the commit comment specifies which task this commit actually resolves (see closing issues using keywords);
- the body of the pull request specifies the wallet addresses in a specific format (e.g., BTC{address}).
- when the pull request is accepted, the payout is made automatically.
- if the wallets are not specified, or not all are specified, the payout for unspecified wallets is made to the default wallets (for example, this could be the project's shared wallet).
Bezpečnosť:
- the attack surface is generally small;
- based on the operating mechanisms, the service should have the ability to send funds independently, so gaining server access would mean control over funds in any case — the only solution could be to operate in a non-automated mode (for example, manual confirmation of payouts), which is likely (if the project is successful enough for someone to donate for this functionality, then it is not likely, but certain) to be implemented at some point;
- critically important parts are clearly separated (essentially, it is a single file pay.go with 200 lines), thereby simplifying the security code review;
- kód prešiel nezávislým bezpečnostným kódom, čo neznamená absenciu zraniteľností, ale znižuje pravdepodobnosť ich prítomnosti, najmä v súvislosti s plánovanou pravidelnosťou revízií;
- sú tu aj časti, ktoré nie sú kontrolované (napríklad API GitHub/GitLab/etc.), pričom možné zraniteľnosti v externom API sa plánuje uzatvoriť dodatočnými kontrolami, avšak celkovo je problém v súčasnom ekosystéme nevyriešiteľný a je mimo rámca (možná zraniteľnosť s, napríklad, možnosťou uzatvárať cudzí pull request a tým pádom pridávať kód do cudzích projektov - má oveľa globálnejšie dôsledky).
Zdroj: linux.org.ru
